Fortinet Community
Recently active
Hello, I want to confirm is this a bug or not As the image shows, the first image dont have the "quarantined message was released by administrator" while the second image do, those emails are released.I though the first image was deleted but actually already released. The fortimail is on v6.0.3 Thanks in advance
Hi, Managing multiple firewalls and has set it to have automatic patch schedule the SAME for all, following this link:https://community.fortinet.com/t5/FortiGate/Technical-Tip-Automatic-Patch-Upgrades/ta-p/272899 However, I noticed that during actual patch schedule, the said firewalls are not updating the same time. Some will have its automatic patch schedule the day after or 3 days after. Is it possible to sync them all? What are being considered in the automatic patch schedule aside from the SAME config for each firewall? Thank you!
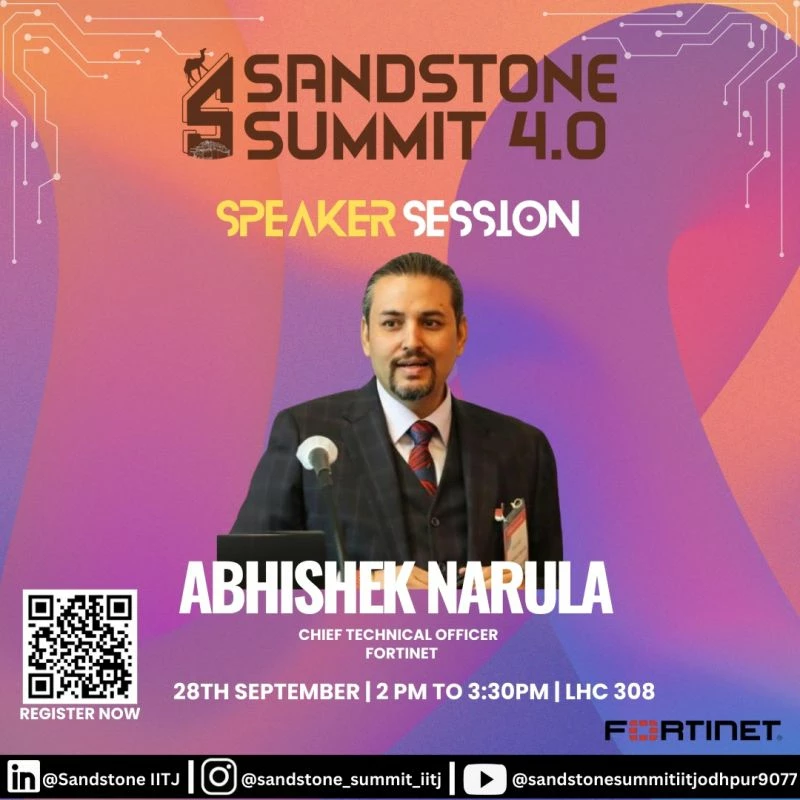
Abhishek Narula, CTO (SOAR Business), would be talking about "Building Career in Cybersecurity & AI" at IIT Jodhpur Sandstone Summit 4.0 https://www.linkedin.com/feed/update/urn:li:activity:7244574804937195521/
Hi, I am attempting to upgrade my HA firewall by following these KBs:FortiGate HA upgrade procedure and the st... - Fortinet CommunityHow to upgrade FortiGate firmware - Fortinet Community However, the upgraded did not pushed through and I am seeing this error on the secondary firewall:Get image from ha master OK. Check image file integrity error! I already tried to check if this is the correct image file from the support site and was able to confirm that this is okay. What is causing this issue? Anything that I should do to successfully upgrade the HA cluster? Thank you!
Im getting this error when launching Secrets in FortiPAM from a Public IP (VIP)
What's up all. Novice at networking here, bear with me. Trying to dump my cheap home firewalls and go with the real thing. Looking to purchase a Fortigate Firewall and Catalyst 1200 Series Switch. Pretty basic setup. I need to:Create VLANS and have them access the internetCompletely isolate the VLANS at Layer 3I have been looking at a few different ways to do this but need help. I can figure out most of the config but could use assistance with the design / have a few config questions. Would you:Go layer 2 VLANS at the switch and then tag them up to the firewall and create firewall policies to separate the VLANS? Would I even need to tag them on the firewall?Would inter-vlans need to be created on the firewall to deny all traffic or could I just create firewall polices for each lan and have the switch handle the tagging?orGo Inter-vlan on the switch and create ACLS on the switch as opposed to having the firewall do the work. It seems strange to me to have a firewall perform switchi
Hi, We are having 4201F in HA integrated with ACI. We see that traceroute is adding 20ms when trace land on FortiGate IP. Looking for opinions to minimize it. Thanks
Is there any way to link two FortiSwitches together so that they can be managed as a single logical unit?. All I can find are options to direct manage to each switch IP, FortiGate Fortilink (but still each switch) or FortiManager. What i'm looking for is a similar way Cisco do the stackwise virtual so that two switches are a logical unit despite being in different locations. You configure both switches via one IP address and you see all ports listed together. I know you can use MCLAG to create a Layer 2 link between the switches so that other edge stacks can connect to both. But I cannot see how to configure and use both switches as one logical unit. Also it gets more complicated as I need to have the FortiSwitches routing so they will have layer 3 IPs and also do some BGP dynamic routing. For routing, is VRRP the only option here if the switches cannot be setup as a single logical stack? The only way I can see it working is:2 Core FortiSwitches independantly manage
after uograde to fortiios 7.4.5 unable to connect fortiguard serversfortigate 400f i can ping all fortiguard servers but cannot connect to servers thanks
Hi Community, Forti sandbox generates malware package, when it found any new malicious file hash the malware package will be updated, and we have the1)Contribute detected suspicious files to Forti Sandbox Community Cloud. " 2)Contribute detected suspicious URL to FortiGuard 3)Upload detection statistics to FortiGuard. Feature in the sandbox,Now my query is if the locally detected file rated as malicious but actually it is a false positive not actually malicious, this signature will be created and contribute this signature to "Sandbox Community Cloud". Or FortiGuard Next time when any one Across the global using Sandbox community cloud" or FortiGuard will also rate this as malicious or not based on this signature? Thanks.
Hi.This is my network: The IPTV service works perfectly if i connect the iptv deco (10.11.12.69) directly to ISP router. If i connect to FGT, the live TV (multicast traffic) works perfect, but VOD (video on demmand) fails. The IPTV works with this subnet: I think the fortigate is routing correctly. But something is bad configured. The INTERNET ROUTER is configured with FULL CONE NAT is VLAN of IPTV service.theoretically, the iptv decoder requests the resource to a server A, but the resource is returned by a server B, to which the IPTV decoder has not established a connection previously. That's what I think is the reason why it's required full cone natI try to:Create manually static routes Configure Full Cone Nat in firewall policy.Configure ip pool in policy Nothing works. This is the logs when i try play some VOD video.2019.570072 lan out 10.64.0.1 -> 10.11.12.69: icmp: time exceeded in-transit2020.252251 lan in 10.11.12.69.50865 -> 172.26.22.11.9153: sy
Hi,Is it possible to configure in split tunnel wildcard FQDN?I have some sites, x.abc.com, I want to set a wildcard FQDN to *.abc.com. It is possible?
We have a number of FortiGate firewalls that we want to create the same Geo Block Group holding a fairly long list of countries to block. We don’t have a FortiManager. Does someone have a script to generate this geo block group on the firewalls from a list of countries? I have found scripts to create a group of IP address but not geo group lists.
Dear All, I have one stand alone Firewall and configured SDWAN (ISP1 & ISP2). The problem which I am facing is If ISP1 goes down then traffic is not flowing to another link (ISP2). I can see that in routing table there are two routes present in the routing table of the firewall but the link which are currently down route is not removing from the routing table. what can be issue however I have configured update static route. FGT_Primeary # get router info routing-table allCodes: K - kernel, C - connected, S - static, R - RIP, B - BGPO - OSPF, IA - OSPF inter areaN1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2E1 - OSPF external type 1, E2 - OSPF external type 2i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area* - candidate defaultRouting table for VRF=0S* 0.0.0.0/0 [1/0] via 192.168.50.1, port1, [1/0][1/0] via 192.168.51.1, port2, [1/0]C 10.1.1.0/24 is directly connected, port3C 192.168.50.0/28 is directly connected, port
Hello ZTNA adminsFortiClient EMS 7.4.0 and FortiOS 7.2.9.When any client is inside (on-fabric) its ZTNA TAGs are visible on FortiClient, FortiClient EMS and on FGT as well.When I connect any client from the WAN (off-fabric) the TAGs are seen on the FortiClient and FortiClient EMS, but are never synced to FortiGate, until the client is back on-fabric again.Any idea?
Hello team!!! We have 2 FGT100F in HA and configured interfaces called "mgmt" as "in band"Now we need to access from a computer in any other interface and get:150.0.0.4 is the IP of Fortigate HA in a specific VLAN and 150.0.0.3 is another device in the same VLAN.I know this is a public IP, but this is complicated to change the IP in all the devices in this VLAN.From 150.0.0.3 I can ping 150.0.0.4, but not the HA IP on mgmt interfaceFrom another device in mgmt interface, I can ping the HA IP on mgmt interface, and each Fortigate as wellPreviously, we had disabled src-check in mgmt interfaceI tried to add a local-in policy to allow this (config firewall local-in-policy), but still the same behaviorWe need to access to Fortigate from any VLAN, using the IP on the mgmt interface. Is this possible? Thanks in advance.Regards,Damián
Hello FCT adminsFCT/EMS 7.4.0.On my Linux I have 2 software detected as PUS: ipscan and pgadmin4.I wanted to test the feature on Windows 10 so I installed the 2 above tools on a Windows client.The new software was inventoried however they are not detected as PUA.Does PUA function the same way on Linux and Windows?Why these apps are detected PUA on Linux but not on Windows?
Hello, Does the FG-901G AC version(NOT DC) have a location for a 2-hole grounding lug on chassis? The quickstart guide shows that the DC version ships with grounding lugs. We have an AC version coming and not sure if we can use a 2-hole 6AWG grounding lug on it.. Thankyou.. full P/N FG-901G-TAA-FGDUS
Hello everybody,I've a problem in my network with my FortiGate.I've a simple SSL-VPN (web mode is disabled) whose access is restricted to italian and albanian addresses:The problem is that there are many connection attempts, and each of these attempts has a different IP address: date=2024-09-27 time=12:27:33 id=7419267613974331394 itime="2024-09-27 12:27:34" euid=5123 epid=3 dsteuid=3 dstepid=3 logver=702101706 logid=0101039426 type="event" subtype="vpn" level="alert" action="ssl-login-fail" msg="SSL user failed to logged in" logdesc="SSL VPN login fail" user="abl0000" remip=87.4.68.245 group="N/A" tunnelid=0 tunneltype="ssl-web" dst_host="N/A" reason="sslvpn_login_unknown_user" eventtime=1727432853997409279 tz="+0200" devid="FGT60FTK23099PH2" vd="root" dtime="2024-09-27 12:27:33" itime_t=1727432854 devname="ntd-fg"date=2024-09-27 time=12:16:21 id=7419264723461341184 itime="2024-09-27 12:16:21" euid=4699 epid=3 dsteuid=3 dstepid=3 logver=702101706 logid=0101039426 type="event" sub
Hello folks,in my deployment i'm using a fortigate 200F with Sso (Azure) and everything was working correctly before upgrading from 7.0.12M to 7.2.7.After the upgrade i'm facing that authd process is constantly consuming 97% of cpu resources and Sso is not working anymore.Thought it was a bug so decided to upgrade newly from 7.2.7 to 7.4.3 but i still have the issue.Tried to reboot the firewall (a HA pair) and until there are no authentication requests from clients, the cpu is ok (authd process is not present in the process list or is at 2%), as soon as there's an authetication request the authd process goes to 97% and so the cpu.In this condition the Sso is not working, i check the configuration and nothing changed, took a debug and sniffer packet from client and all the routing is ok, checked fsso configuration both on firewall and Azure and it's ok.Did you face something similar? Do you have any advise? The upgrade triggered something but i can't understand what is the ro
I am currently experiencing issues while attempting to upgrade the Fortigate firmware to version 7.2.4. The upgrade is failing both through the GUI and TFTP methods. The original firmware version is 7.0.10. However, when attempting to upgrade to random version 7.2.6 or downgrade to version 6.4.14, I can successfully perform the upgrade or downgrade using TFTP. If anyone has encountered the same issue and has found a solution, please let me know. The model of the Fortigate is 80F. I wanted to upgrade to 7.2.4Booting OS... No default firmware. Error: Default firmware boot failed!!! Switch to BACKUP after 31 seconds. Press any key to stop. FOS boot failed. You may try backup. Please power cycle. System halted. System will auto-reboot after 59 seconds ('CTRL+D' to reboot immediately). resetting ... FortiGate-80F (05:42-06.01.2023) Ver:05000100 Serial number: FGT80FTK23045999 CPU: 1200MHz Total RAM: 4 GB Initializing boot device... Initializing MAC... NP6XLITE#0 Please wait for OS
Currently have device profile rules not linked to any policy. Then changed what host role the device profile rule give in registration settings. Devices in this group are not updating with the new Role. Deleting the device and NAC relearning/profiling to the same rule does then apply the new role. Is there a more automated way for the devices in a rule to update their role? Thanks
Hi, has anyone been able to (or even tried to) convert a running instance of a FortiNAC appliance running in a VMWare environment to a Hyper-V environment? We're looking to move away from vmware and I was curious if I could just move it like I did my windows machines. Any suggestions / tips / words of wisdom are appreciated. --mike
HI,I have problems with the credential cache of the mfa vpn with okta, in the sense that the first login with mfa works correctly but if I disconnect and try to reconnect the forticlient dosentt ask me for the credentials or the mfa and it connects without asking me anything, I I was wondering if on the okta/fortigate side I can configure something that forces forticlient to request the mfa login every time without having to delete the forticlient cache file. I use the free forticlient version. Thanks in advance. Giuseppe
I have configured the SD-WAN, but unable to create the static route it gets this error "You cannot have duplicated routes on SD-WAN and non-SD-WAN interfaces.object set operator error, -9100 discard the settingCommand fail. Return code -9100" i couldn't see such route either in GUI or in CLI
Already have an account? Login
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.