

Fortilover
Explorer III
June 21, 2024
Solved

What is going on with Version 7.4.4?

  • June 21, 2024
  • 12 replies
  • 16502 views

Dear all.


After upgrading to version 7.4.4 we experience massive performance and handling issues. Can anyone of you confirm this?


What I can see among other things are the following facts:


  1. When adding new entries to an already existing address group the entries in the group are sorted alphabetically the entries on the right which I want to choose are not. They are sorted by creation. So new entries are at the end.
  2. When adding new entries to a already existing address group the entries on the right I want to add are only loaded when I scoll down and this takes very long. It is like only 30 entries are loaded and the others are not. They will be loaded only when I scroll down to the end. We use hundreds and thousands of entries and the scrolling for new created entries takes minutes now and not only 1-2 seconds like in version 7.4.0. In 7.4.0 just all where loaded directly and I was able to scroll down to the end immediately.
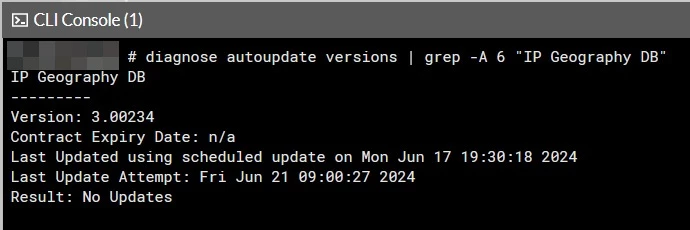
  3. The country database in order to block IPs seems to be completely wrong. Most of the IPs are assigned to Finnland although they are located in Ukraine, Germany, Netherlands, United Arabic Emirates and so on... I have checked the update status of the country database and it seems up to date but it is definetely wrong. countrydb.jpg
  4. Mailing for Actions (Security Fabric -> Automation) is still working but now with another additional Reply To Address (DoNotReply@fortinet-notifications.com). Like described here: https://community.fortinet.com/t5/FortiGate/Technical-Tip-Unable-to-send-FortiToken-email-using-custom-smtp/ta-p/317048
  5. The bad thing is that mail delivery for 2FA User Logins (SSL VPN for instance) is not working at all anymore. Could be related to the article I have posted in point 4. I have tried everything. It just does not work anymore with custom defined smtp servers. Thanks for that... :(
  6. In the list for Adresses for instance we see the column Ref like in the other versions 7.4.0. But now I cannot filter or sort by Ref anymore. It is/was helpful to see which entries are not used anymore. Now this is not possible anymore in our environment because we have thousands of entries... and scrolling down until to the end and looking for entries with 0 references is quite imppossible.
  7. Bookmarks for websites in VPN Portals seem not to work like before. The connection to the internal server is just blocked although nothing has been changed before and after the update related to those settings. Means our Websites we have provided through Web mode SSL VPN for external accesses will not work anymore.
  8. There are more and more warning messages in the GUI related to legacy web modes: "For increased security, use SSL-VPN tunnel mode instead of the legacy web mode." If it is unsafe why is it now displayed as a warning and not disabled to use?

I really love my Fortigate and the Fortinet infrastructure like you can see in my nickname :) I really do. But this update is really really bad to be honest. Do you experience the same? I am really sure we will rollback to 7.4.0 in the next days. 7.4.4 is quiet impossible to use in comparison to 7.4.4... And why are address groups an address lists now separated? Why?! :D Come on guys from fortinet. Who made this decisions? Can you not just add an option to switch between the old and new GUI so that customers can choose on their own what to use? In my personal opinion this is not a good update for real hugh environments like we have with thousands of entries... 

I think I will find more "not so well" changes. But probably not because I think first off all the best idea is to rollback.


With kindest Regards a not so happy FortiLover after updating :(

Best answer by Fortilover

Dear all.


Together with the german support team we have figgured out why we had so much trouble after updating to 7.4.4. We have still an old Hardware Revision of the Fortigate 100F which has only 4GB of RAM. Newer Hardware revision has already 8GB RAM. That RAM is quite always full so that it comes to massive performance issues (conserved mode). It seems so that in our configuration we use so much features that this model or 4GB RAM in total is not enough. It is the IPSengine to be more precise. That engine processes will be used not only by IPS checks. It is used for SSL inspections as well and so on... Like I said... with our amount of used features and connected devices it is not enough RAM.


Personally I ask myself why Fortinet is so "thrifty" (no affront) in its Hardware designs when it comes to RAM. To be honest... It is 2024 :) The use of 4GB modules is probably not really uptodate in nowerdays. But hey :) I would wish that the minimum of every Fortigate is at least 16GB of RAM or more. When I check the prices for RAM modules it does not make really differences between 4GB and 16GB RAM modules. And I think customers would be happy to have a device that is future-proof... only because of the RAM as newer versions with more features really consumes more memory. And if I have to pay 50 Euros more for more RAM... I would be happy. It is a difference to upgrade RAM compared to buy a new 400F with a 5 year support contract and EP bundle.


So I just wanted to give a feedback. The question is solved hereby. We need a bigger Hardware for our needs. Looking for a 400F model I think as it has 16GB RAM. Hopefully future-proof. You can see it here. This comparision is really handy dandy. Hardware comparison for Fortigate models 


If I could I would like to configure the hardware before buying. But it is the way it is :) You want just more RAM although your CPU is sleeping all the time. Then buy a more powerful hardware... that seems to be the only good solution for now. The 400F model is not that cheap compared to our 100F. I would say the 100F is enough for us when I could increase the RAM... But this seems not the way Fortinet would like to have it :) So we probably buy the 400F or 401F.


With kindest regards

FortiLover

12 replies

AEK
SuperUser
SuperUser
June 21, 2024

Hi FortiLover

I went through the 7.4.4's known issues and didn't find the bugs you described above, this should mean that you may have discovered new issues in this version. I think if you report these bugs by opening a ticket, Fortinet will handle this issues seriously and correct them in future patches.


On the other hand 7.4.0 seems to be a very nice version with nice new features but it is very new and it has not yet reached maturity. So you may already know that you should not install 7.4.x (from 7.4.0 to 7.4.4) in critical production environment, you should rather install the recommended version: 7.2.8, which is stable and vulnerability free (so far).

Ref:  https://community.fortinet.com/t5/FortiGate/Technical-Tip-Recommended-Release-for-FortiOS/ta-p/227178


AEK
Pittstate
Explorer
June 21, 2024

Running 7.4.4 on a new install of 1800F in HA. I see no major issues with performance on 7.4.4. It's not without its behavioral issues, so if you're coming from an earlier version, you will see some changes. Most of the issues I've had are moving from a stand alone (on 7.0.14) to an HA config and some of the nuances there. I've also encountered a behavioral change in how the FG handles timeouts with remote/ldap authentications. I also realize that I'm making a two version jump to the bleeding edge, so I accept the risks that come with the territory.


I did notice the sorting issue mentioned in your point #1, and as for #2 you can always filter your search instead of scrolling the gui. If you have thousands of entries, filtering would seem more efficient anyway. I do that and I only have several hundred entries because I don't want to scroll. But these are minor QoL issues and will be fixed as 7.4 matures.


Regarding your point #7 and #8, they have disabled web mode by default in new installs. They also tell you to disable it in the 7.4.4 administrator's guide sslvpn security best practices section.


Based on what you've written it looks like you've migrated into the 7.4 series and so these features will be enabled and you'll get warnings. To me, it looks like Fortinet is moving away from sslvpn type connections and trying to move people towards certificate based IPSEC or ZTNA policy. A skeptic would say this is for financial purposes, getting people to license their other products. But nearly all the major exploits against a FG in the last few years have involved the sslvpn component. All the major security vendors have had their sslvpns exploited in some fashion in the last year. So, it makes sense for them to try to limit the attack surface.


Why don't they just disable it? Because people who had it configured would complain that it suddenly stopped working. So instead they give you a warning message and nudge you to start migrating away from it. Also, I'd imagine Fortinet would disable it if they could as sslvpn has been a major thorn in their side for at least the last 3 years from major security exploit perspective. All of the emergency maintenance patches I've performed have been because of an sslvpn exploit of some kind.

Fortilover
FortiloverAuthorAnswer
Explorer III
September 18, 2024

Dear all.


Together with the german support team we have figgured out why we had so much trouble after updating to 7.4.4. We have still an old Hardware Revision of the Fortigate 100F which has only 4GB of RAM. Newer Hardware revision has already 8GB RAM. That RAM is quite always full so that it comes to massive performance issues (conserved mode). It seems so that in our configuration we use so much features that this model or 4GB RAM in total is not enough. It is the IPSengine to be more precise. That engine processes will be used not only by IPS checks. It is used for SSL inspections as well and so on... Like I said... with our amount of used features and connected devices it is not enough RAM.


Personally I ask myself why Fortinet is so "thrifty" (no affront) in its Hardware designs when it comes to RAM. To be honest... It is 2024 :) The use of 4GB modules is probably not really uptodate in nowerdays. But hey :) I would wish that the minimum of every Fortigate is at least 16GB of RAM or more. When I check the prices for RAM modules it does not make really differences between 4GB and 16GB RAM modules. And I think customers would be happy to have a device that is future-proof... only because of the RAM as newer versions with more features really consumes more memory. And if I have to pay 50 Euros more for more RAM... I would be happy. It is a difference to upgrade RAM compared to buy a new 400F with a 5 year support contract and EP bundle.


So I just wanted to give a feedback. The question is solved hereby. We need a bigger Hardware for our needs. Looking for a 400F model I think as it has 16GB RAM. Hopefully future-proof. You can see it here. This comparision is really handy dandy. Hardware comparison for Fortigate models 


If I could I would like to configure the hardware before buying. But it is the way it is :) You want just more RAM although your CPU is sleeping all the time. Then buy a more powerful hardware... that seems to be the only good solution for now. The 400F model is not that cheap compared to our 100F. I would say the 100F is enough for us when I could increase the RAM... But this seems not the way Fortinet would like to have it :) So we probably buy the 400F or 401F.


With kindest regards

FortiLover

AlexC-FTNT
Staff
Staff
September 18, 2024

Just a hint on memory: the memory chips used are usually not the regular PC modules that are fine-tuned for speed and low latency. On top of that, the memory chips on firewalls are also designed with reliability in mind, and different read/write patterns. That's what makes them more expensive than the memory chips you find on the market

Fortilover
Explorer III
September 18, 2024

I understand that. And still I think that those modules will not be that expensive. To be honest. It is still a difference if I would have the choice to pay, let's say 300-500€ more for an RAM upgrade instead of buying a new 401F with EP or UTP bundle for the next 5 years you know?. But I understand your point and this is fully correct.

JPIZZLE
Explorer II
September 19, 2024

Hello, FortiLover.  I'm experiencing issues with 7.4.4 on 201E cluster but in other ways.  Security Fabric view is unavailable, HA has trouble syncing, I see web interface errors like "Time is out of sync," and the web interface freezes as the CPU spikes to 100% almost immediately.  I can use Putty to run the 'fnsysctl killall httpsd' to temporarily regain access to the web interface, but the Security Fabric, Firmware and Registration, and other views no longer work.  Memory is not maxed.  I plan to roll the fabric back to the stable release soon if Fortinet continues to miss the scheduled patch release.


** Update: The day of the 7.4.5 release, definitions hit my FortiGate fleet.  By the following Sunday, my FortiGate fleet behaved much better.  I saw my security fabric and firmware and registration screens for the first time since 7.4.5 was released.  The time sync error still occurs, however.  I'm happy to be able to administer the firewalls.  I'm convinced that the issues were something to do with the intrusion detection or application control.


*** Update: Just because I'm a glutton for punishment, I applied the 7.4.5 release to the FortGates and the 7.6.0 release to the Forti switches.  So far, so good.

Pittstate
Explorer
September 19, 2024

Or you can go up to 7.4.5, which looks like it was released yesterday.

They labeled it "mature". Guess we'll see.

Fortilover
Explorer III
October 8, 2024

We have updated the firewall to 7.4.5 like suggested from @Pittstate and additional to this we have installed/configured FortiAnalyzer and disabled the option on the firewall to write logs into memory. After a restart of the firewall we can confirm that the RAM usage so far is not that high that the conserved mode is triggered (works now for round about 2 weeks). But it is important to restart the firewall after the configuration as the logs seem to stay parked in the memory. Now we see a usage of 60%-75% with FortiGate 100F (1st hardware revision with 4GB RAM). It is still not really enough RAM but for us it is a temporary solution until we have a better model. Probably we do not need to update to a Fortigate 4xx series model. We probably just need the 2nd hardware revision of our Firewall.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
