




FortiCNAPP AI Assist – Accelerating the Investigation and Remediation of Cloud Threats
FortiCNAPP AI Assist: From signal overload to action
SOC Analyst burnout and the cybersecurity skills gap continue to worsen. SOC teams shouldn’t need deep detection expertise to understand what happened and decide what to do next — and FortiCNAPP AI Assist is built around that simple observation. Shaped for and by analysts using the product daily, every change targets a specific friction point between “alert fired” and “incident resolved.” The result is an AI-assisted triage workflow that correlates context, prioritizes findings, generates remediation grounded in the specific alert, and calls out exactly where confidence ends and assumptions begin.
This matters because composite alerts — FortiCNAPP's high-fidelity signals that correlate multiple indicators into coherent attack narratives — carry a lot of context by design. As Fortinet's white paper on AI-driven investigation and remediation describes, the opportunity is in bridging the gap between surfacing correlated alert observations and guiding analysts to confident action. AI Assist now offers end-to-end action plans: Starting from setting context with summarization through step-by-step remediation, on every alert type, with explicit confidence reasoning at each step.
"What do I do next?" Leveraging AI tools to empower the Security Analyst
SOC workflows move fast. When a composite alert fires, analysts need to quickly assess severity, scope, and the right first action — often across multiple alerts in a single shift. The most effective teams do this by correlating context across entities, events, and timelines, and moving directly from signal to response. The question is how much of that work can be automated, so analysts can focus on the decisions that actually require human judgment.
That's what AI Assist is designed to do. Rather than requiring analysts to manually assemble context across tabs and views, AI Assist correlates the available signal, structures it by priority, and produces remediation grounded in the specific entities involved — not a generic playbook. The result is a faster path from alert to action, regardless of an analyst's familiarity with the underlying detection logic.
The alerts user interface has also been refreshed to support this. The alerts Dashboard now defaults to sorting by severity with a stable secondary sort by start time, so the most critical and recent signals surface first. Analysts can also interact with the trend overview to focus on alert spikes and quickly drill into periods of heightened activity. Page size is larger. Bulk actions have safer confirmation handling. Workflows and page layout have been optimized for fast scanning and responsive drill downs. Filtering is smoothly integrated within dashboard cells which allows contextual examination without typing or searching attribute lists. These improvements make the triage environment faster to navigate before a single AI Assist prompt is typed.
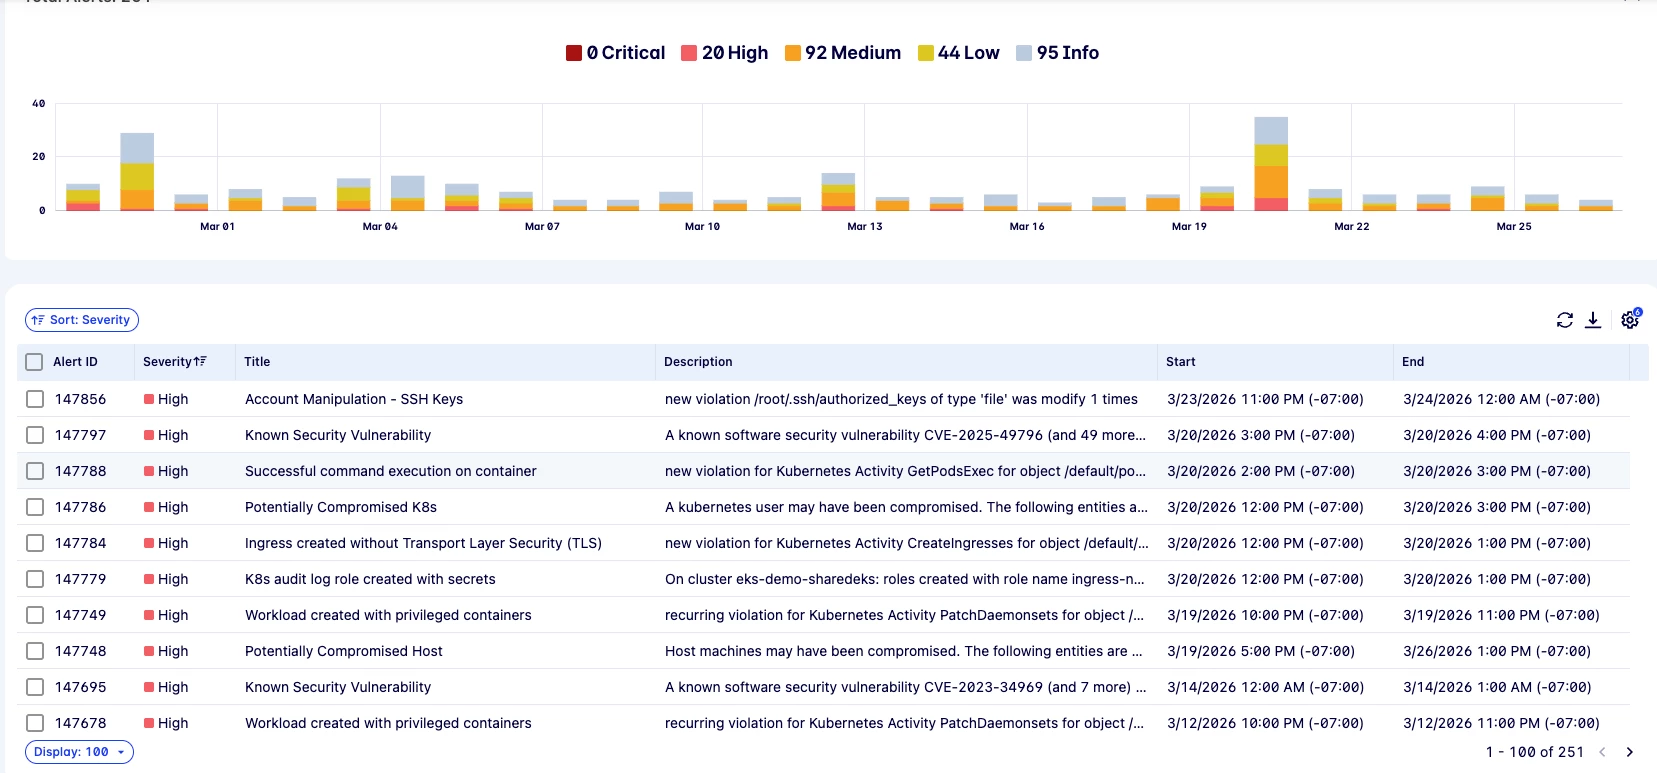
How AI Assist gets analysts to "What do I do next?" faster
The following updates span the full triage arc: from the moment an analyst opens an alert through investigation, remediation planning, and handoff. Every newly available AI enabled workflow connects back to reducing the time, toil, and expertise required to move from signal to action.
Start investigating immediately, not five clicks later.
AI Assist now opens with direct action-oriented options — Incident Report and Remediate are available from the first interaction. Follow-up questions are surfaced as contextual suggestions so analysts don't have to guess what to type next. Conversations can be restarted cleanly when switching between investigations, preventing context bleed between alerts. A new Triage button delivers a high-signal assessment view — a quick read on severity, scope, and recommended first steps — without requiring a full summarization pass to immediately provide the focus on critical details first.
The former “Summarize” action has been renamed to Incident Report, because it encompasses and summarizes all the incident details into a comprehensive report, by retaining all important information. It’s not a paragraph-length recap. It’s a structured output with ranked findings, entity tables, timeline evidence, and confidence assessments — something an analyst can drop directly into a ticket, paste into a Slack thread, or hand off to the next shift.
The full AI Assist conversation exports as Markdown, and individual responses can be copied at the question level. The output is designed to leave the tool and stay useful.
Prioritized summaries replace manual toil of the past.
"Scroll and assemble,"a quite advanced and difficult task for the most hardened analysts, is now one click. AI Assist will correlate all available context for an alert — the who, what, where, when, and why — along with entities, events, and timeline data. If needed, AI Assist draws on comprehensive detection expertise from Fortinet’s security research and can instantly surface relevant product documentation. The AI Assist produces ranked, structured summaries: top findings first, then supporting evidence and event sequence, then explicit confidence levels, assumptions, and data gaps. Sophisticated Polygraph Anomaly models filter the noise and surface a low number of suspicious outbound connections. AI Assist works in tandem with this process so that analysts do not need to labor over understanding specific trigger conditions. Beyond describing what happened, AI Assist adds interpretive context: it surfaces the key entities (process, host, user, destination), highlights conflicting signals — say, a trusted process binary contacting a newly observed external IP — and lists the exact checks to confirm or rule out legitimacy.
Structured narrative with clear priority.
Utilize AI in tandem with Composite alerts to quickly and easily take action. The analytically powerful Composite alerts aggregate multiple detection types into a single incident. AI Assist transforms those detection groupings into three things: a clear narrative of what happened and in what order, a prioritized list of the most urgent items requiring attention, and key entities with supporting evidence mapped to each item. The analyst gets a story, not a spreadsheet.
Remediation that's specific to the alert, not a static playbook.
AI Assist generates remediation grounded in the specific alert context and the entities involved — actions explicitly tied to what's in front of the analyst, like "rotate the access key for identity X that was used from anomalous IP Y to call Z API" rather than "rotate credentials." Recommendations reference actual hostnames, identities, cloud resources, and observed behaviors. The difference between "consider network isolation" and "isolate host ip-10-123-45-67 from subnet 10.123.45.0/24 pending forensic review of the reverse shell observed at 13:01 UTC" is the difference between guidance and action. The AI Assist will also help identify where in your cloud service provider to make the change directly.
Triage-first guidance that works across skill levels.
Every AI Assist response follows a consistent incident response flow:
- Verify and scope the situation
- Contain if necessary
- Eradicate the root cause
- Recover operations
- Harden against recurrence.
Critically, each response includes an "if you can only do one thing" step — the single highest-leverage action to take for that specific alert and moment. AI Assist is also deliberate about not recommending disruptive actions when compromise hasn't been confirmed. For ambiguous alerts — say, a trusted process contacts a newly seen external IP — AI Assist starts with ownership verification and scoping. It recommends containment only if validation suggests genuine risk, and it explicitly calls out potential business impact of each action so the analyst can make an informed call.
Confidence reasoning and "could this be legitimate?" checks are built in, not bolted on. Every AI Assist response distinguishes confirmed facts from hypotheses, and states the reasoning behind its confidence level. Data gaps are called out explicitly — if a log source was not available or an entity has incomplete telemetry about it, the response says so. And for every finding, AI Assist has explicit benign and false-positive frameworks that will provide specific validation steps. This isn't about hedging, it's about giving the analyst the complete decision surface: here's what we know, here's what we don't, here's how to check, and here's what changes depending on the answer.
Case Study: RiskWatch
To ground this in something concrete: these AI Assist capabilities are already operating on live signals from RiskWatch, FortiCNAPP’s runtime vulnerability detection capability. RiskWatch identifies when containerized workloads are actively executing vulnerable code — not just whether a CVE exists in an image scan, but whether the vulnerable library is loaded and running in production.
The proof point is straightforward: A customer reached out asking how to deploy agents in their cloud workloads specifically to receive RiskWatch signals. RiskWatch-based composite alerts identified and helped remediate two production applications running vulnerable code within hours of the first probes going live. A security analyst caught both while monitoring alerts in production.
The pipeline is real, end-to-end, and already working: RiskWatch detects vulnerable code execution at runtime → FortiCNAPP correlates that signal with other observations into an alert → AI Assist helps the analyst understand the scope, assess the risk, and take specific remediation action in no time.
Case Study: Anomaly Alerts
The best way to understand what these updates deliver is to walk through a real session. The alert is "Outbound connection from vulnerable application to a domain" — a high-severity anomaly alert flagging a containerized Python application with a known CVE making outbound HTTPS connections to LaunchDarkly feature-flag domains from three Kubernetes clusters across different AWS regions. The analyst asks one question: "Summarize this alert with prioritized findings, what happened, and scope/impact."
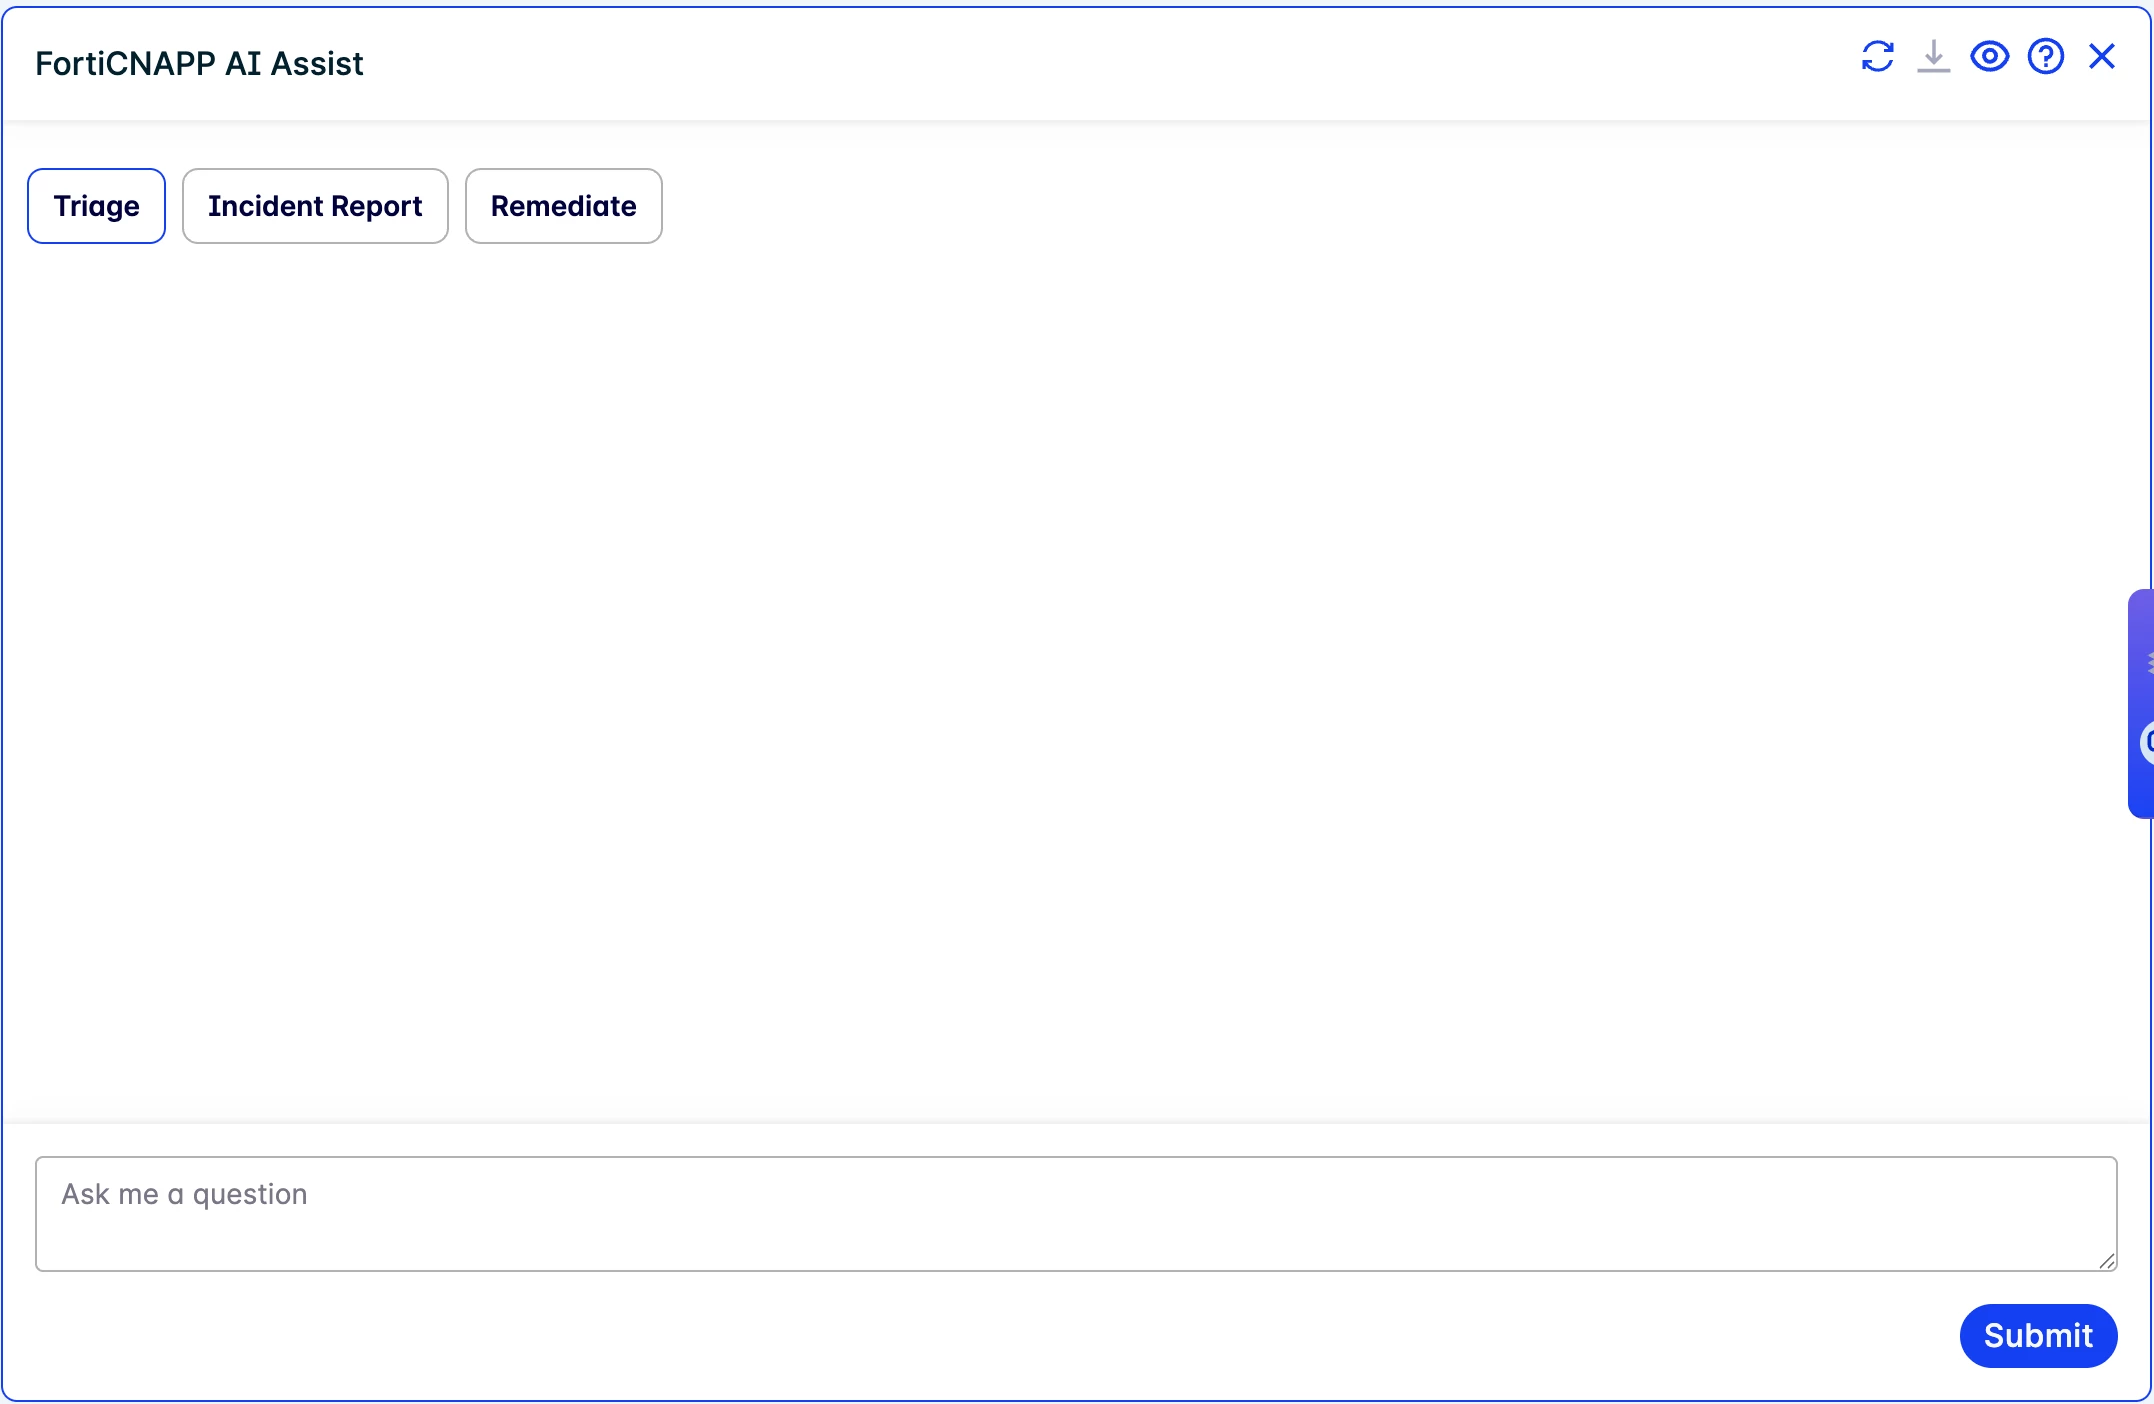
The AI Assist panel opens with three immediate action buttons — Triage, Incident Report, and Remediate — so the analyst can jump straight to the right starting point without configuring anything. No preamble, no setup. The free-text field is also available for custom questions from the start.
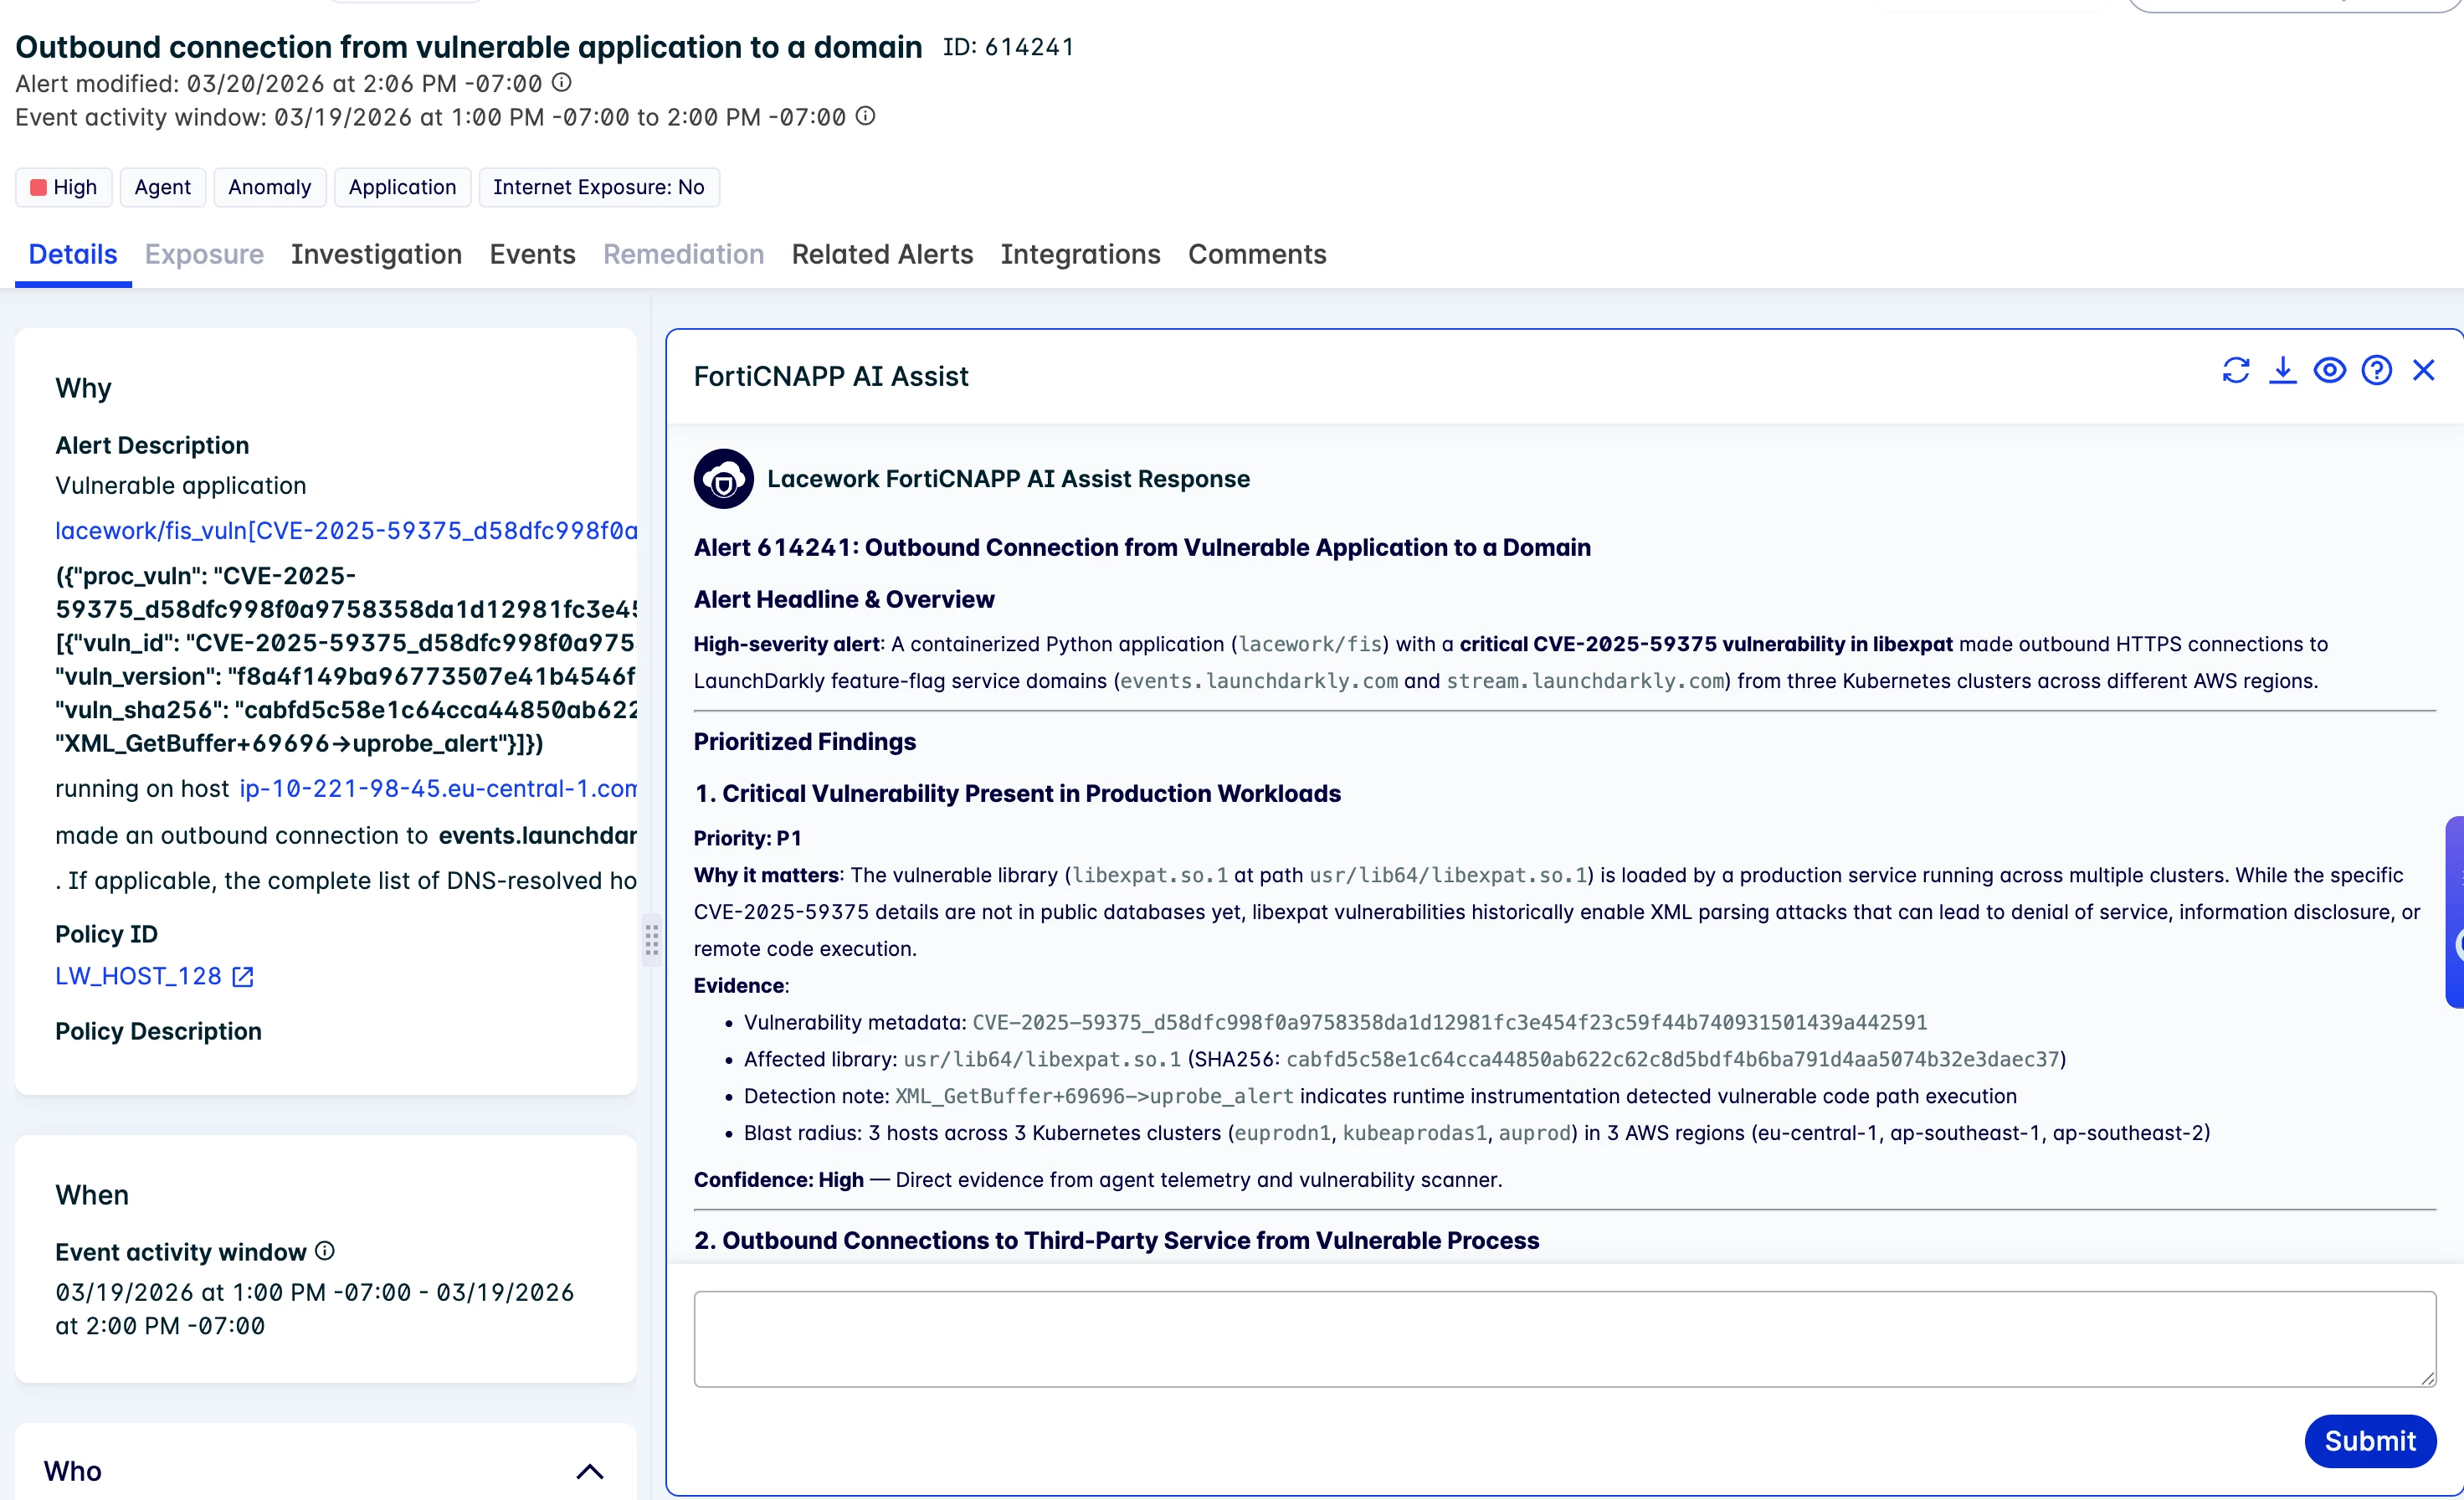
The response opens with a one-sentence alert headline that captures the full signal: a containerized Python application (lacework/fis) with a critical CVE-2025-59375 vulnerability in libexpat made outbound HTTPS connections to LaunchDarkly feature-flag domains from three Kubernetes clusters across different AWS regions. Below that, Prioritized Findings begin.
Finding 1 is marked P1: Critical Vulnerability Present in Production Workloads. It explains why it matters — the vulnerable libexpat.so.1 library is loaded by a production service running across multiple clusters, and libexpat vulnerabilities historically enable XML parsing attacks leading to denial of service, information disclosure, or remote code execution. Evidence is listed explicitly: vulnerability metadata including the full CVE ID, the affected library path and SHA256 hash, the runtime detection note showing vulnerable code path execution was confirmed, and the blast radius — 3 hosts across 3 Kubernetes clusters in 3 AWS regions. Confidence is stated as High, with the reasoning: direct evidence from agent telemetry and vulnerability scanner.
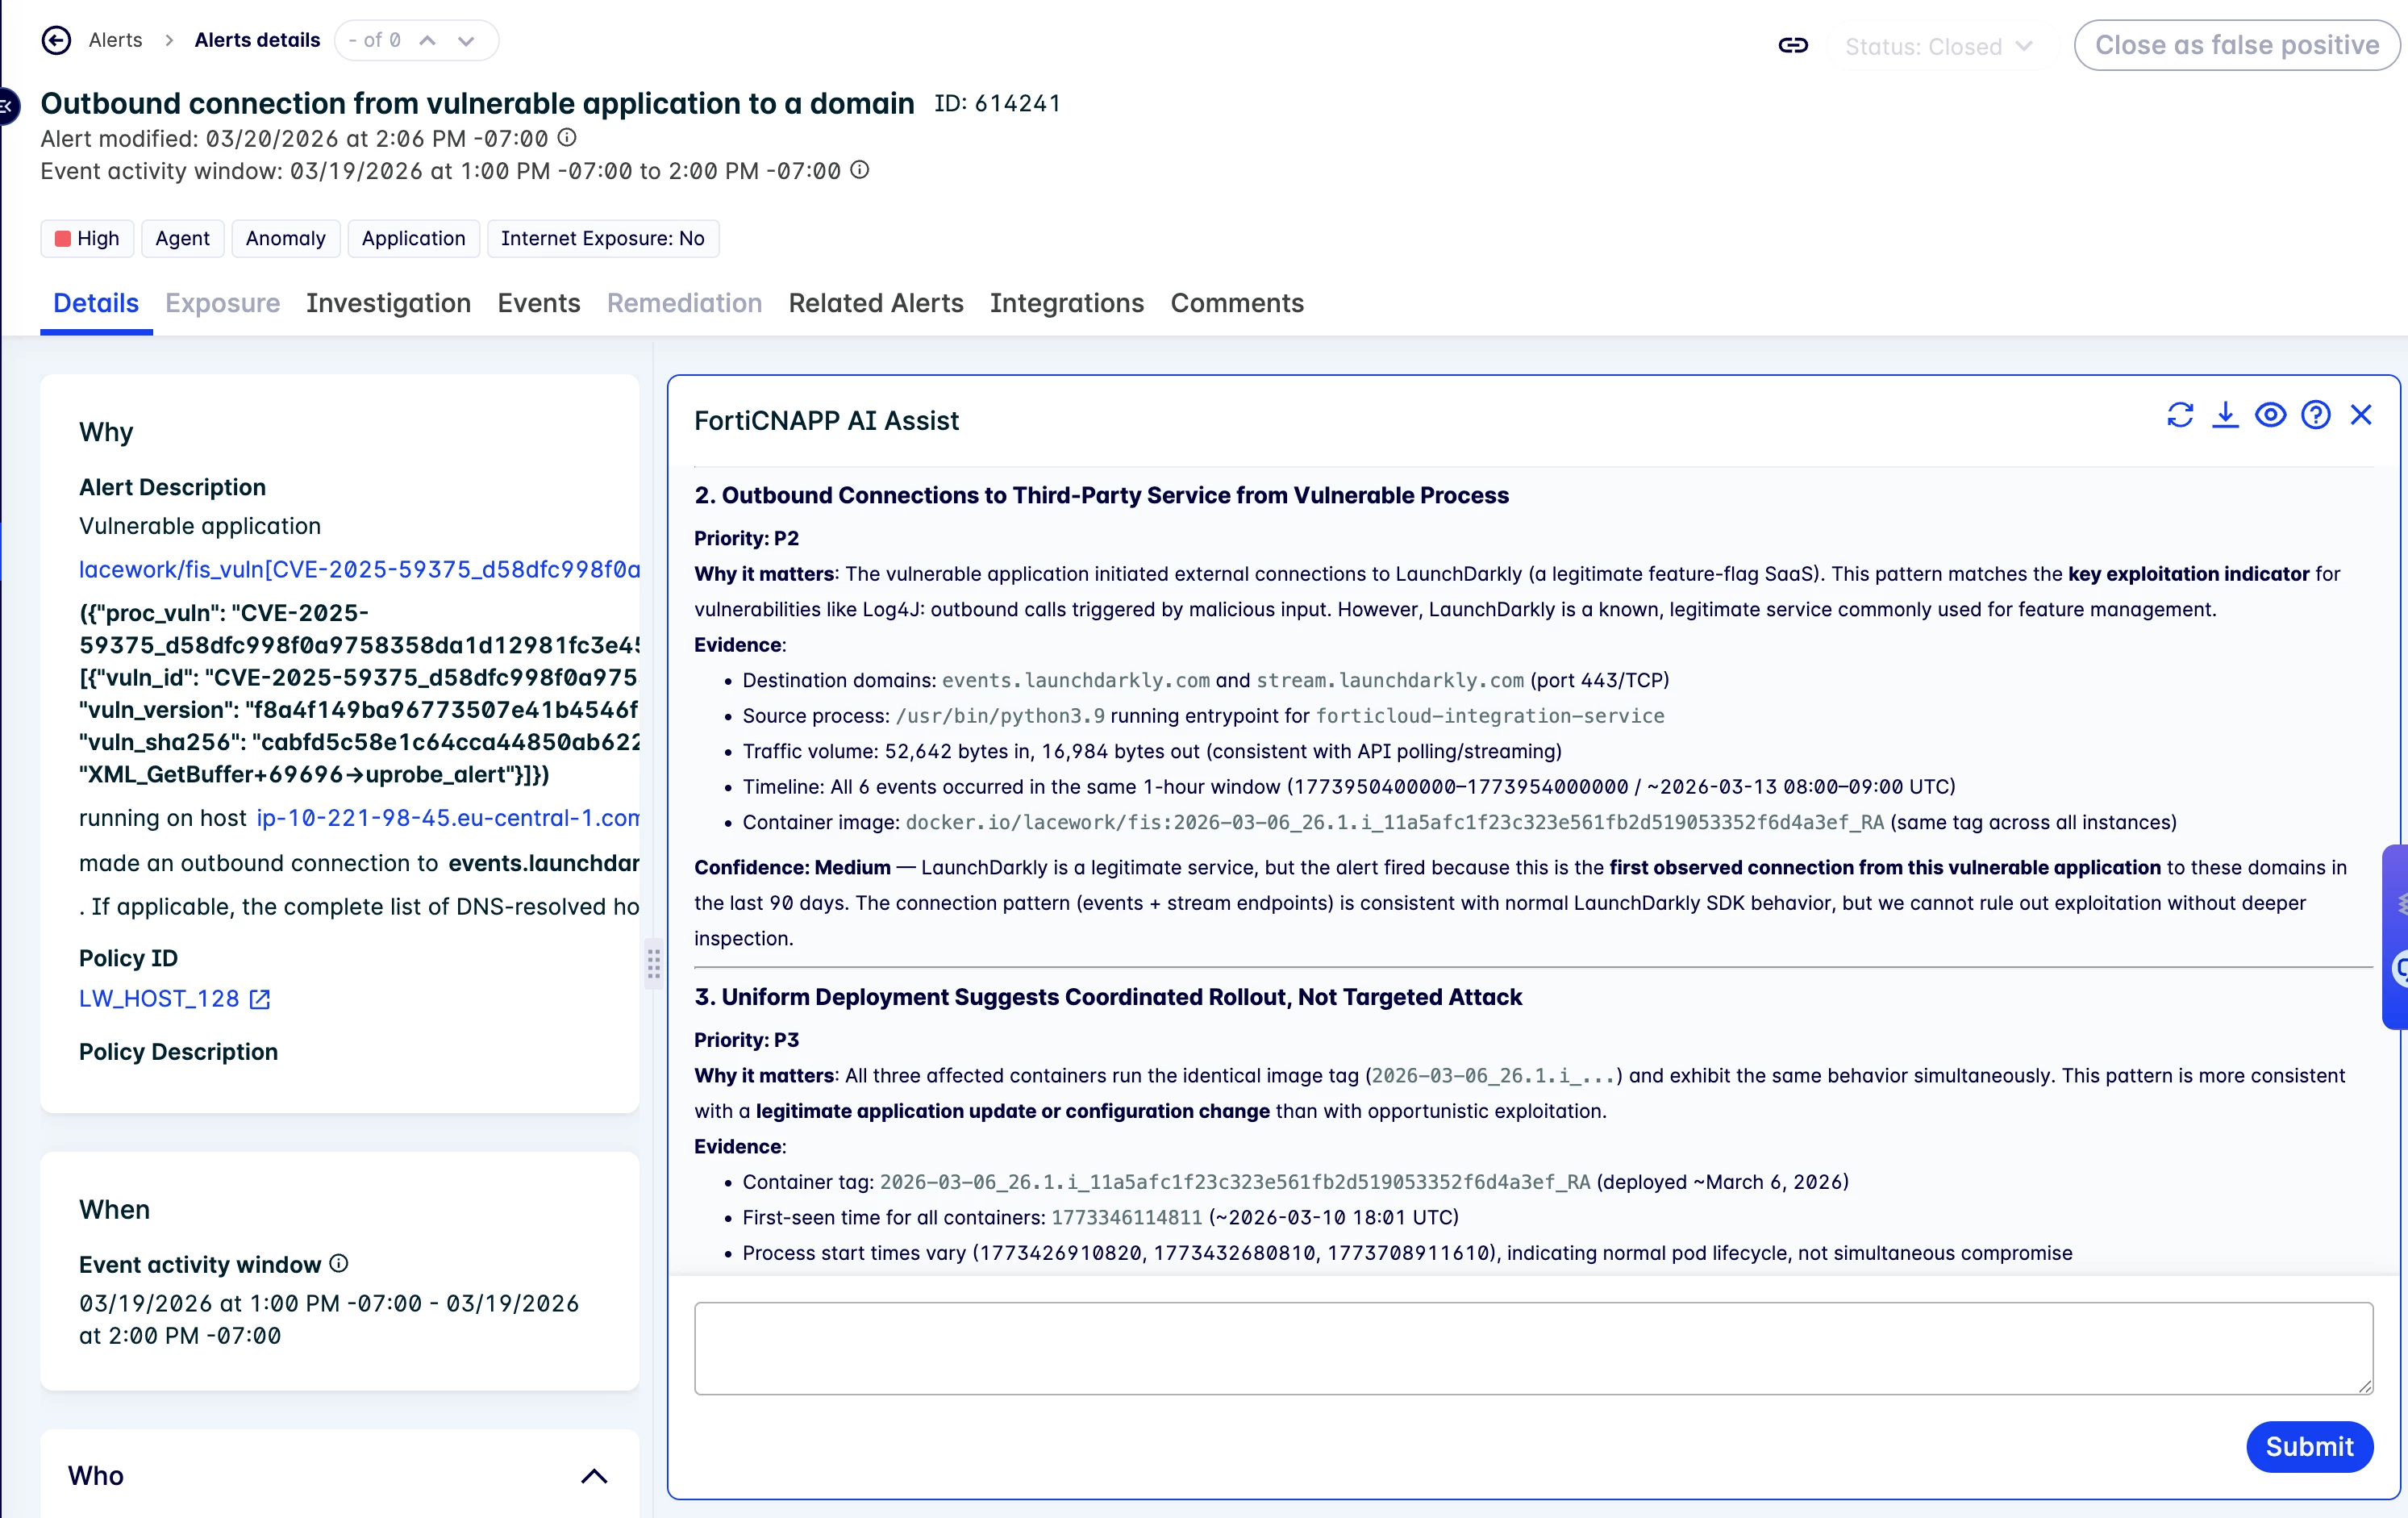
Finding 2 is P2: Outbound Connections to a Third-Party Service from a Vulnerable Process. AI Assist flags this as matching the key exploitation indicator pattern for vulnerabilities like Log4j — outbound calls triggered by malicious input — while simultaneously noting that LaunchDarkly is a known legitimate service commonly used for feature management. Evidence includes destination domains, source process, traffic volume (52,642 bytes in, 16,984 bytes out, consistent with API polling), and the timeline showing all six events occurred within the same one-hour window. Confidence is Medium, with the reasoning explicit: this is the first observed connection from this specific application to these domains in 90 days, which is what triggered the alert — not the connection itself.
Finding 3 is P3: Uniform Deployment Suggests Coordinated Rollout, Not Targeted Attack — all three affected containers run the identical image tag and exhibit the same behavior simultaneously, which is more consistent with a legitimate application update than with opportunistic exploitation. This is AI Assist doing the false-positive reasoning the analyst would otherwise have to do manually.
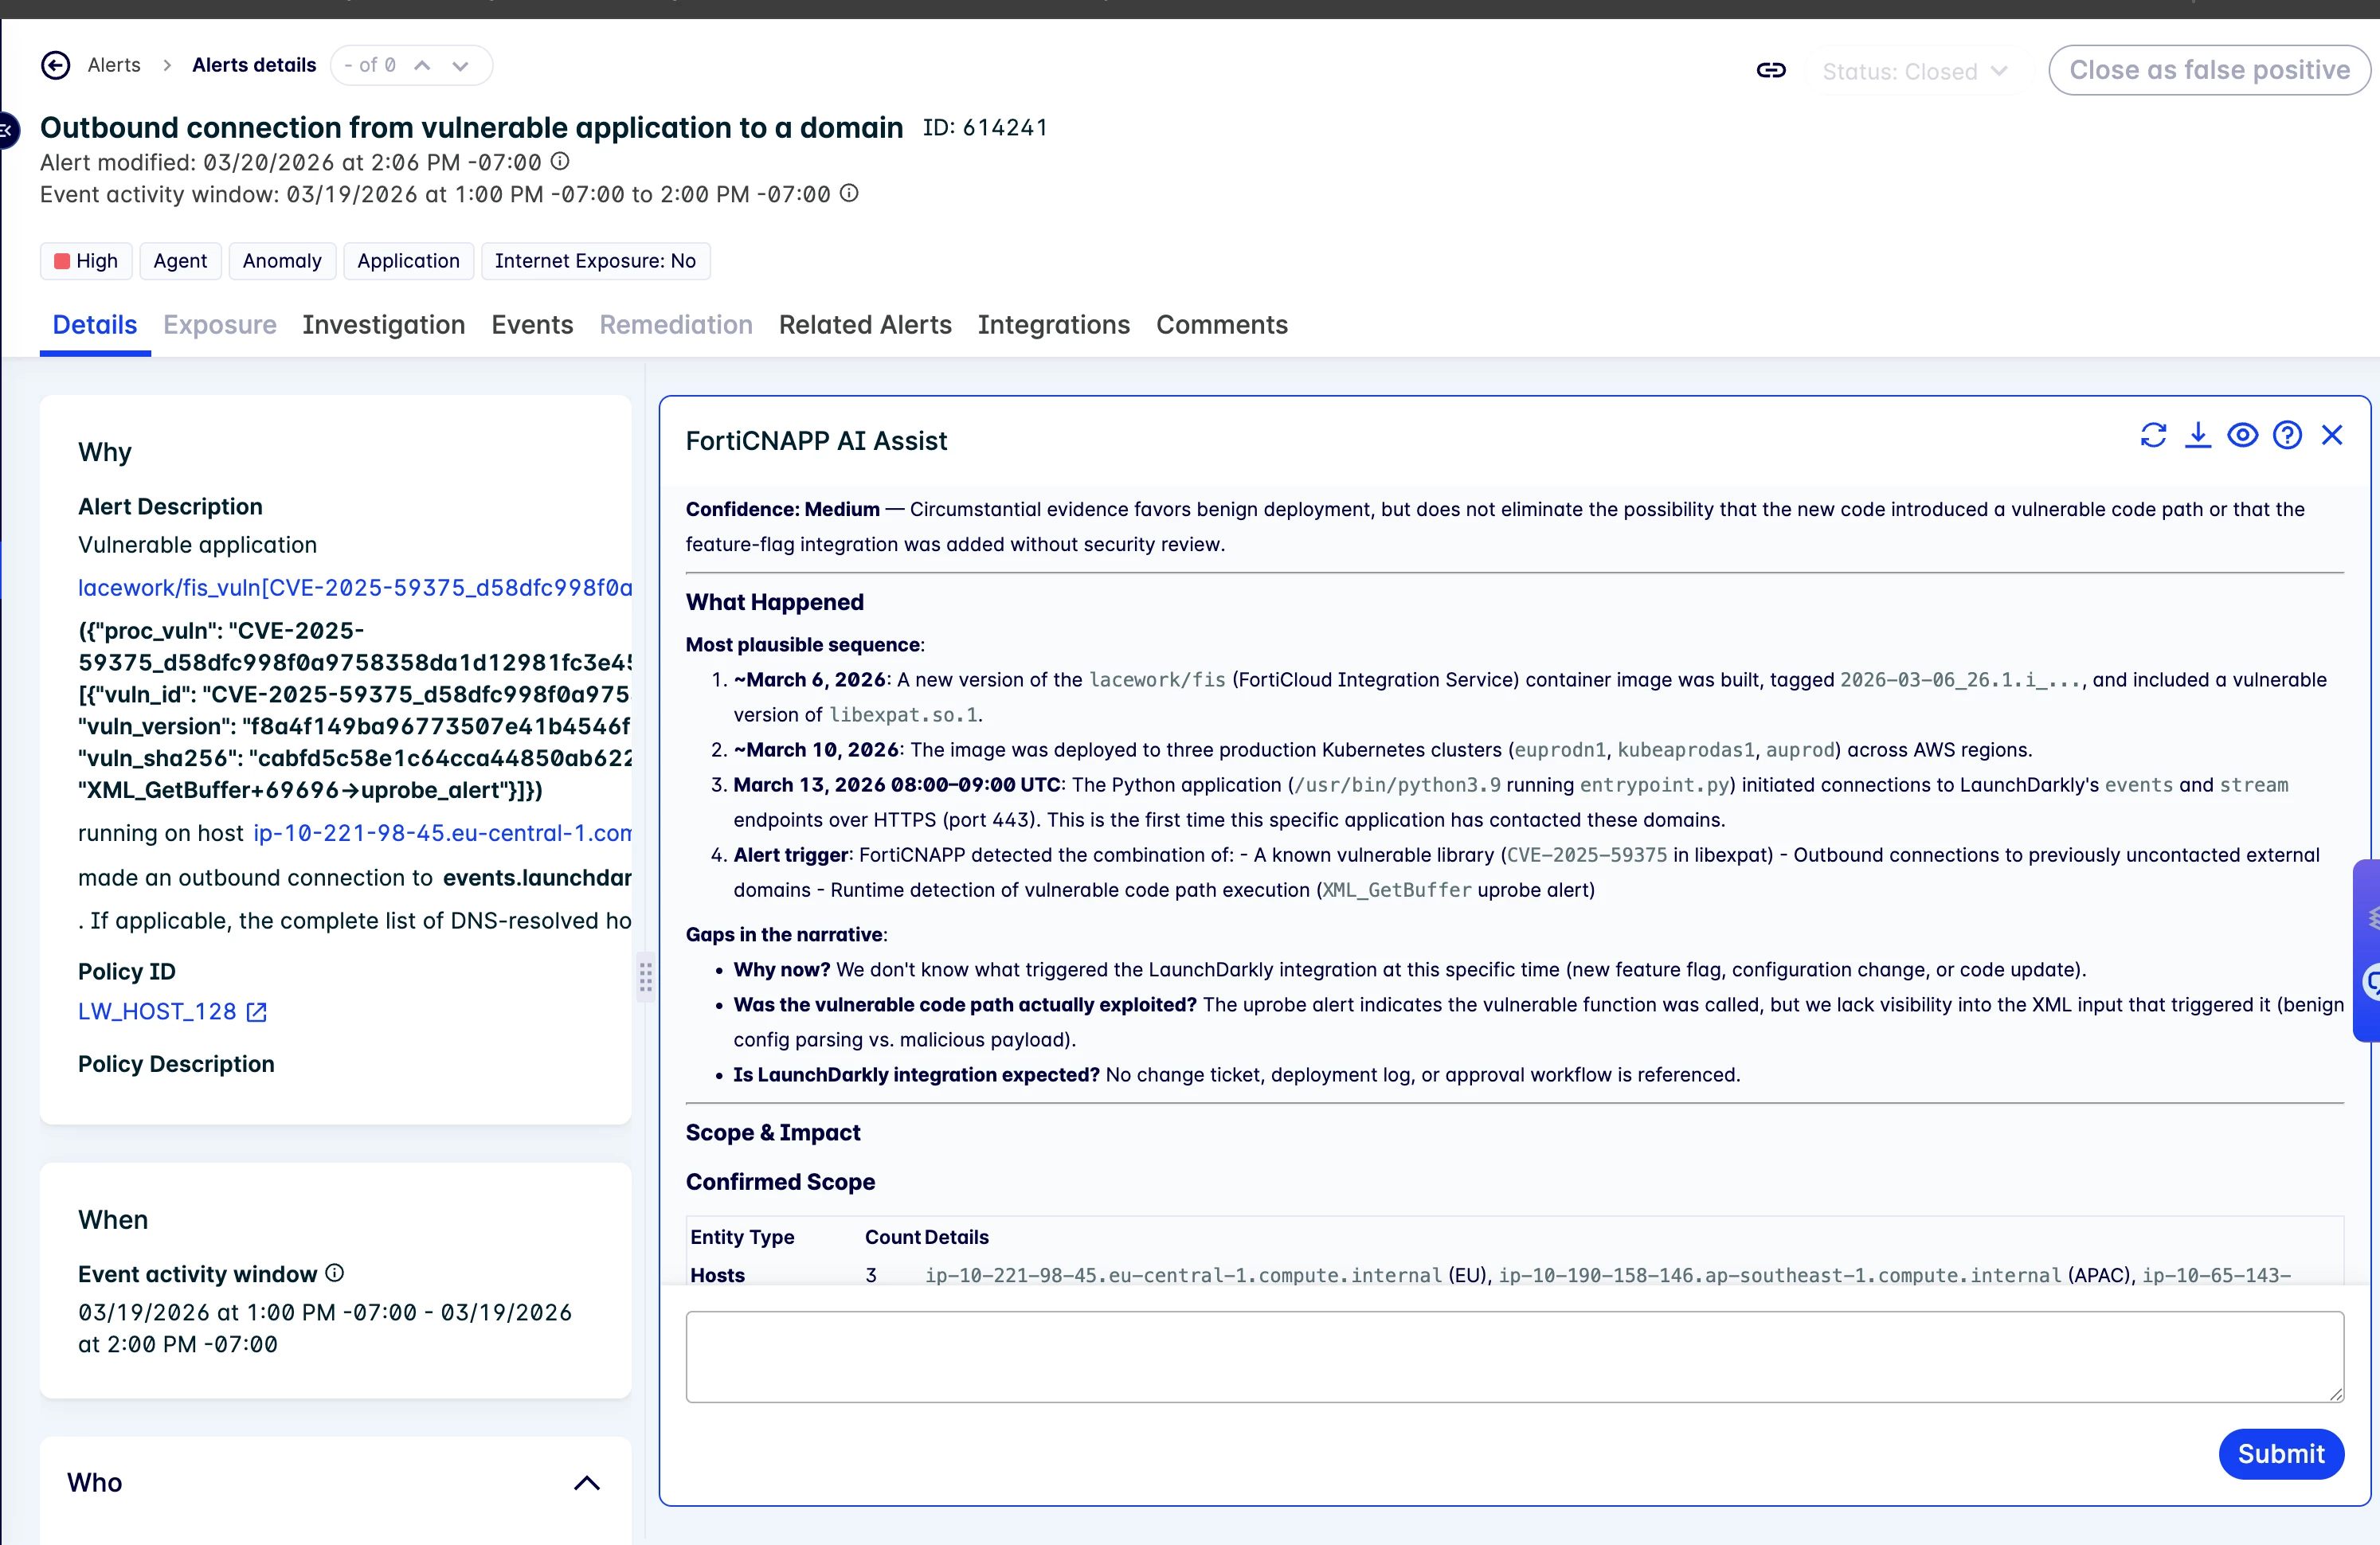
Timeline of events
The What Happened section reconstructs a four-step timeline: the lacework/fis container image included a vulnerable libexpat.so.1; it was deployed to three production Kubernetes clusters. Three days later, the Python application initiated connections to LaunchDarkly's events and stream endpoints; FortiCNAPP detected the combination of a known vulnerable library, outbound connections to previously uncontacted external domains, and runtime detection of vulnerable code path execution. Gaps in the narrative are listed directly beneath — why the LaunchDarkly integration was triggered at that specific time, whether the vulnerable code path was actually exploited (the uprobe alert shows the function was called but not what input triggered it), and whether the integration was an expected change. These aren't loose ends — they're the specific questions the analyst needs to answer next, handed to them in order.
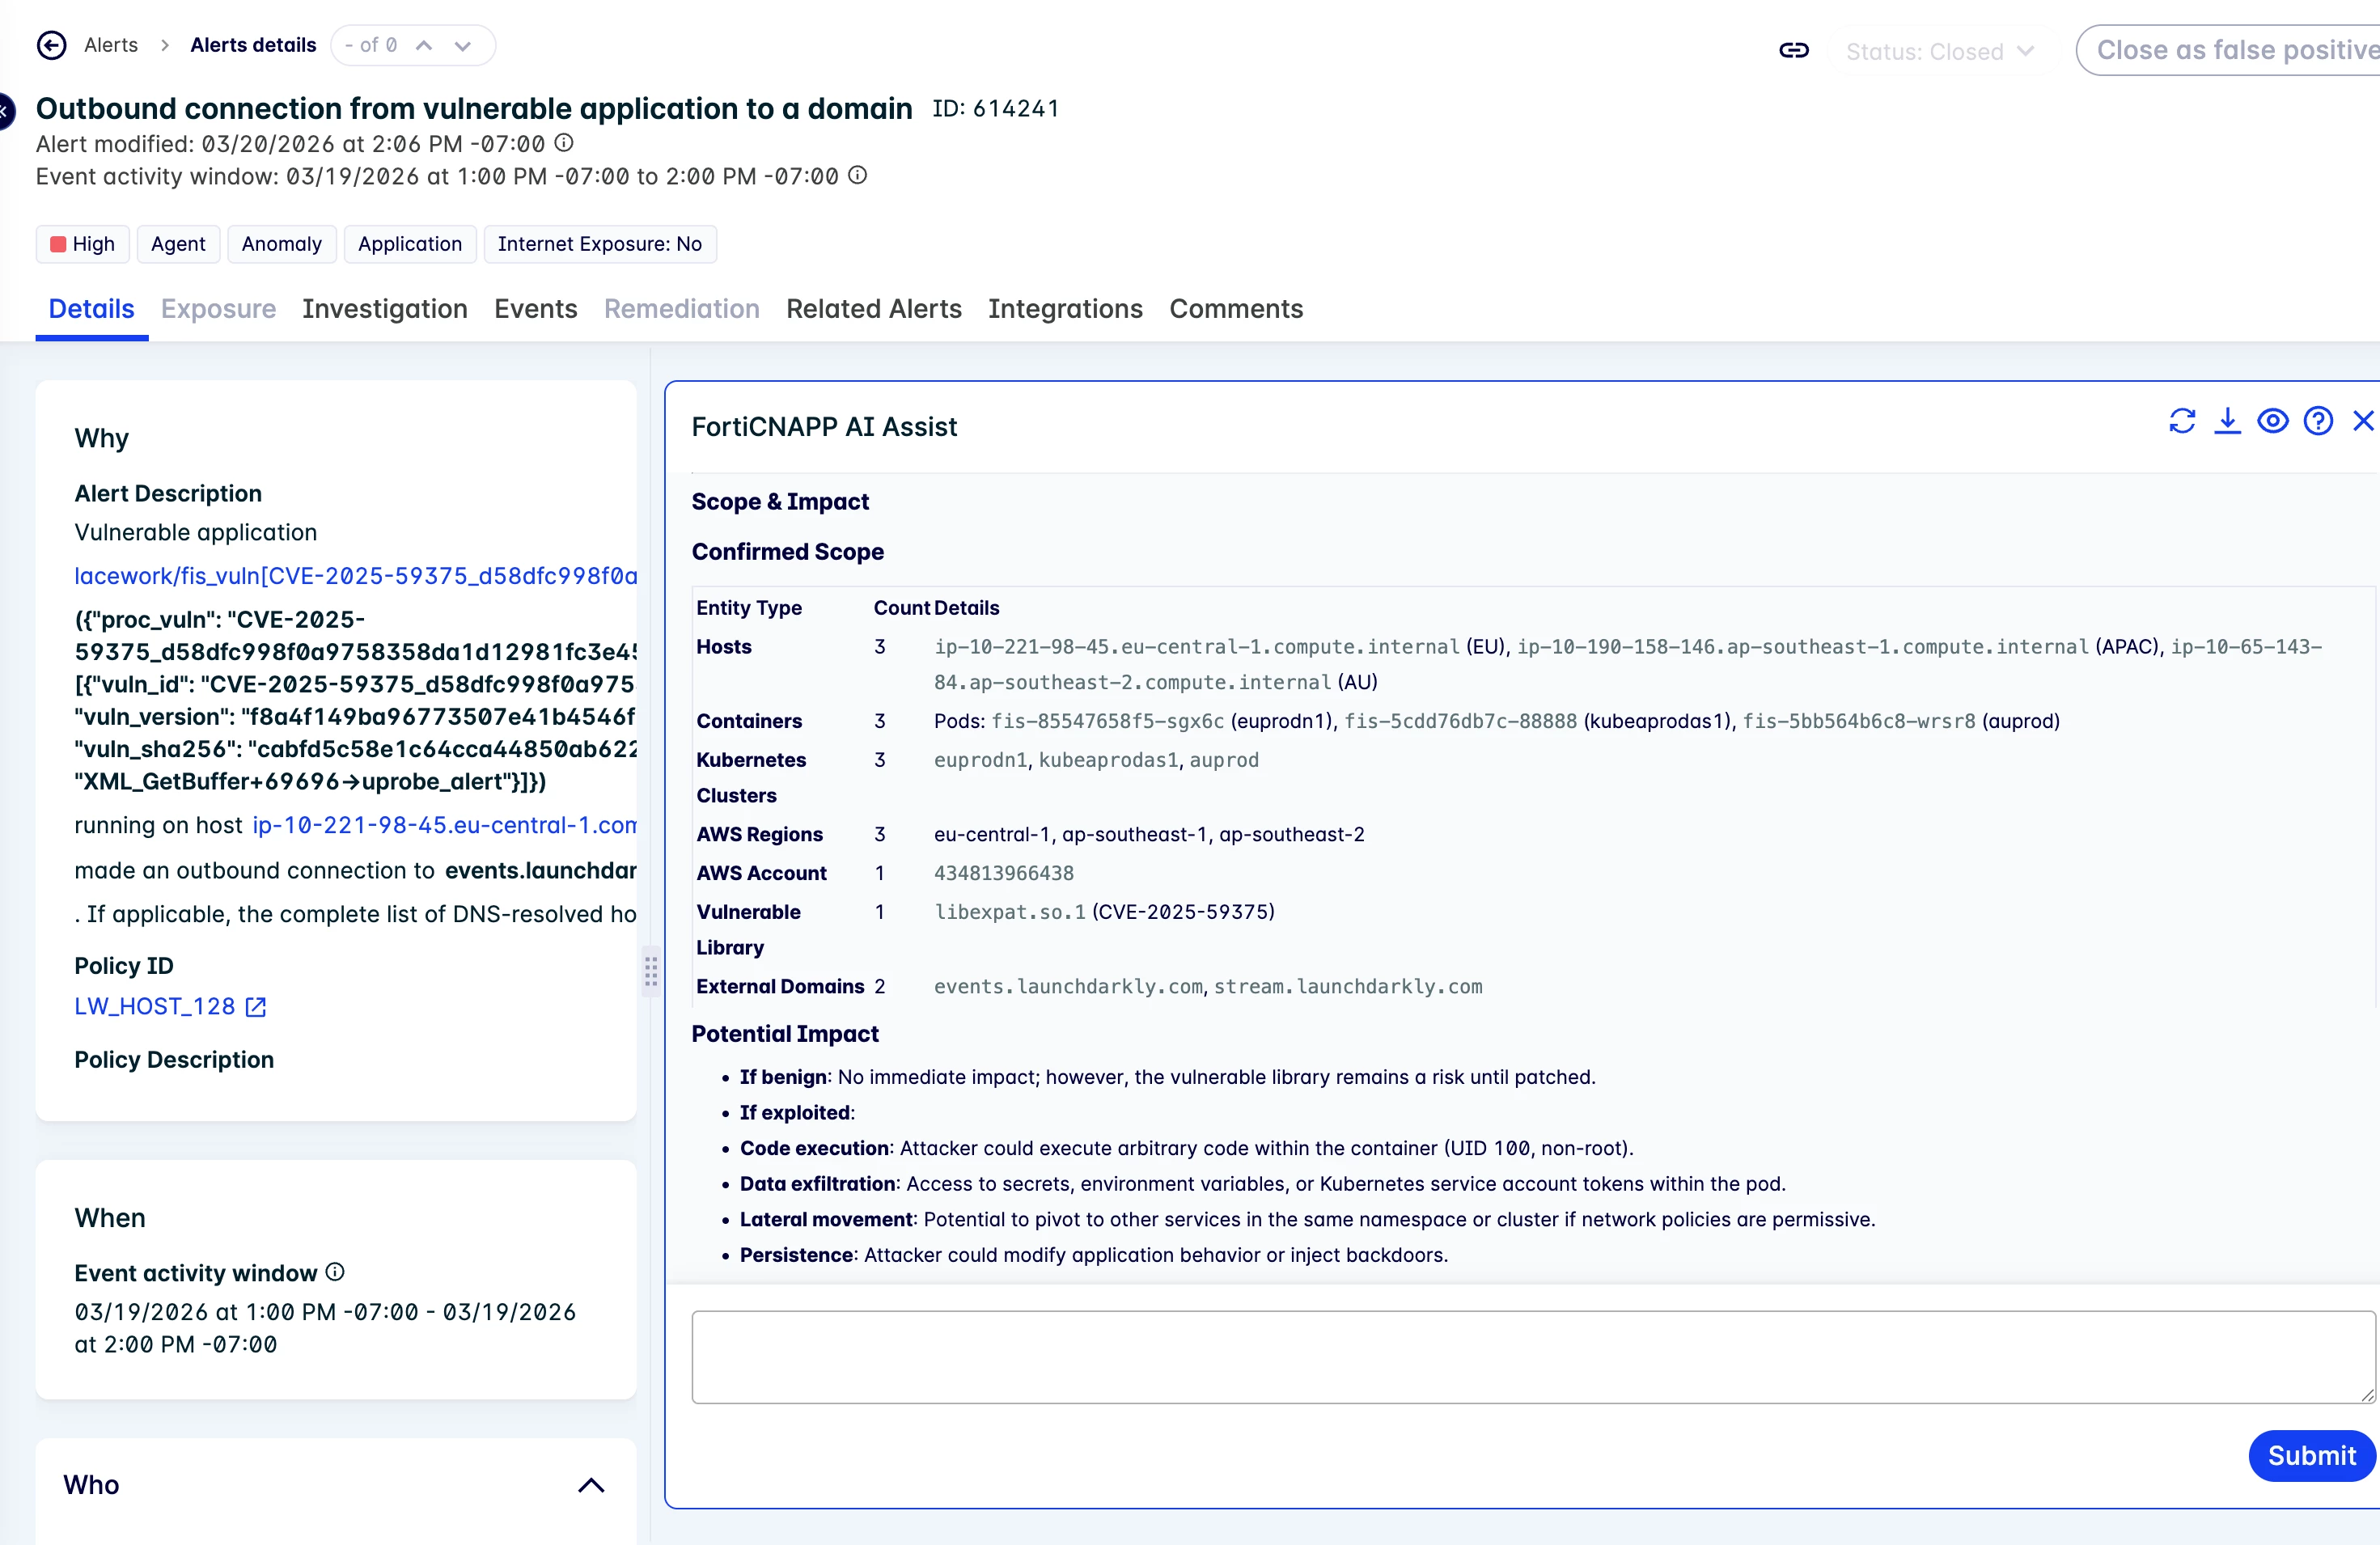
Risk and Impact Assessment
The Scope & Impact table enumerates the confirmed blast radius: 3 hosts by name and region (EU, APAC, AU), 3 container pod IDs, 3 Kubernetes cluster names, 3 AWS regions, 1 AWS account, 1 vulnerable library (libexpat.so.1, CVE-2025-59375), and 2 external domains — assembled automatically and surfaced as the first items in the given response.
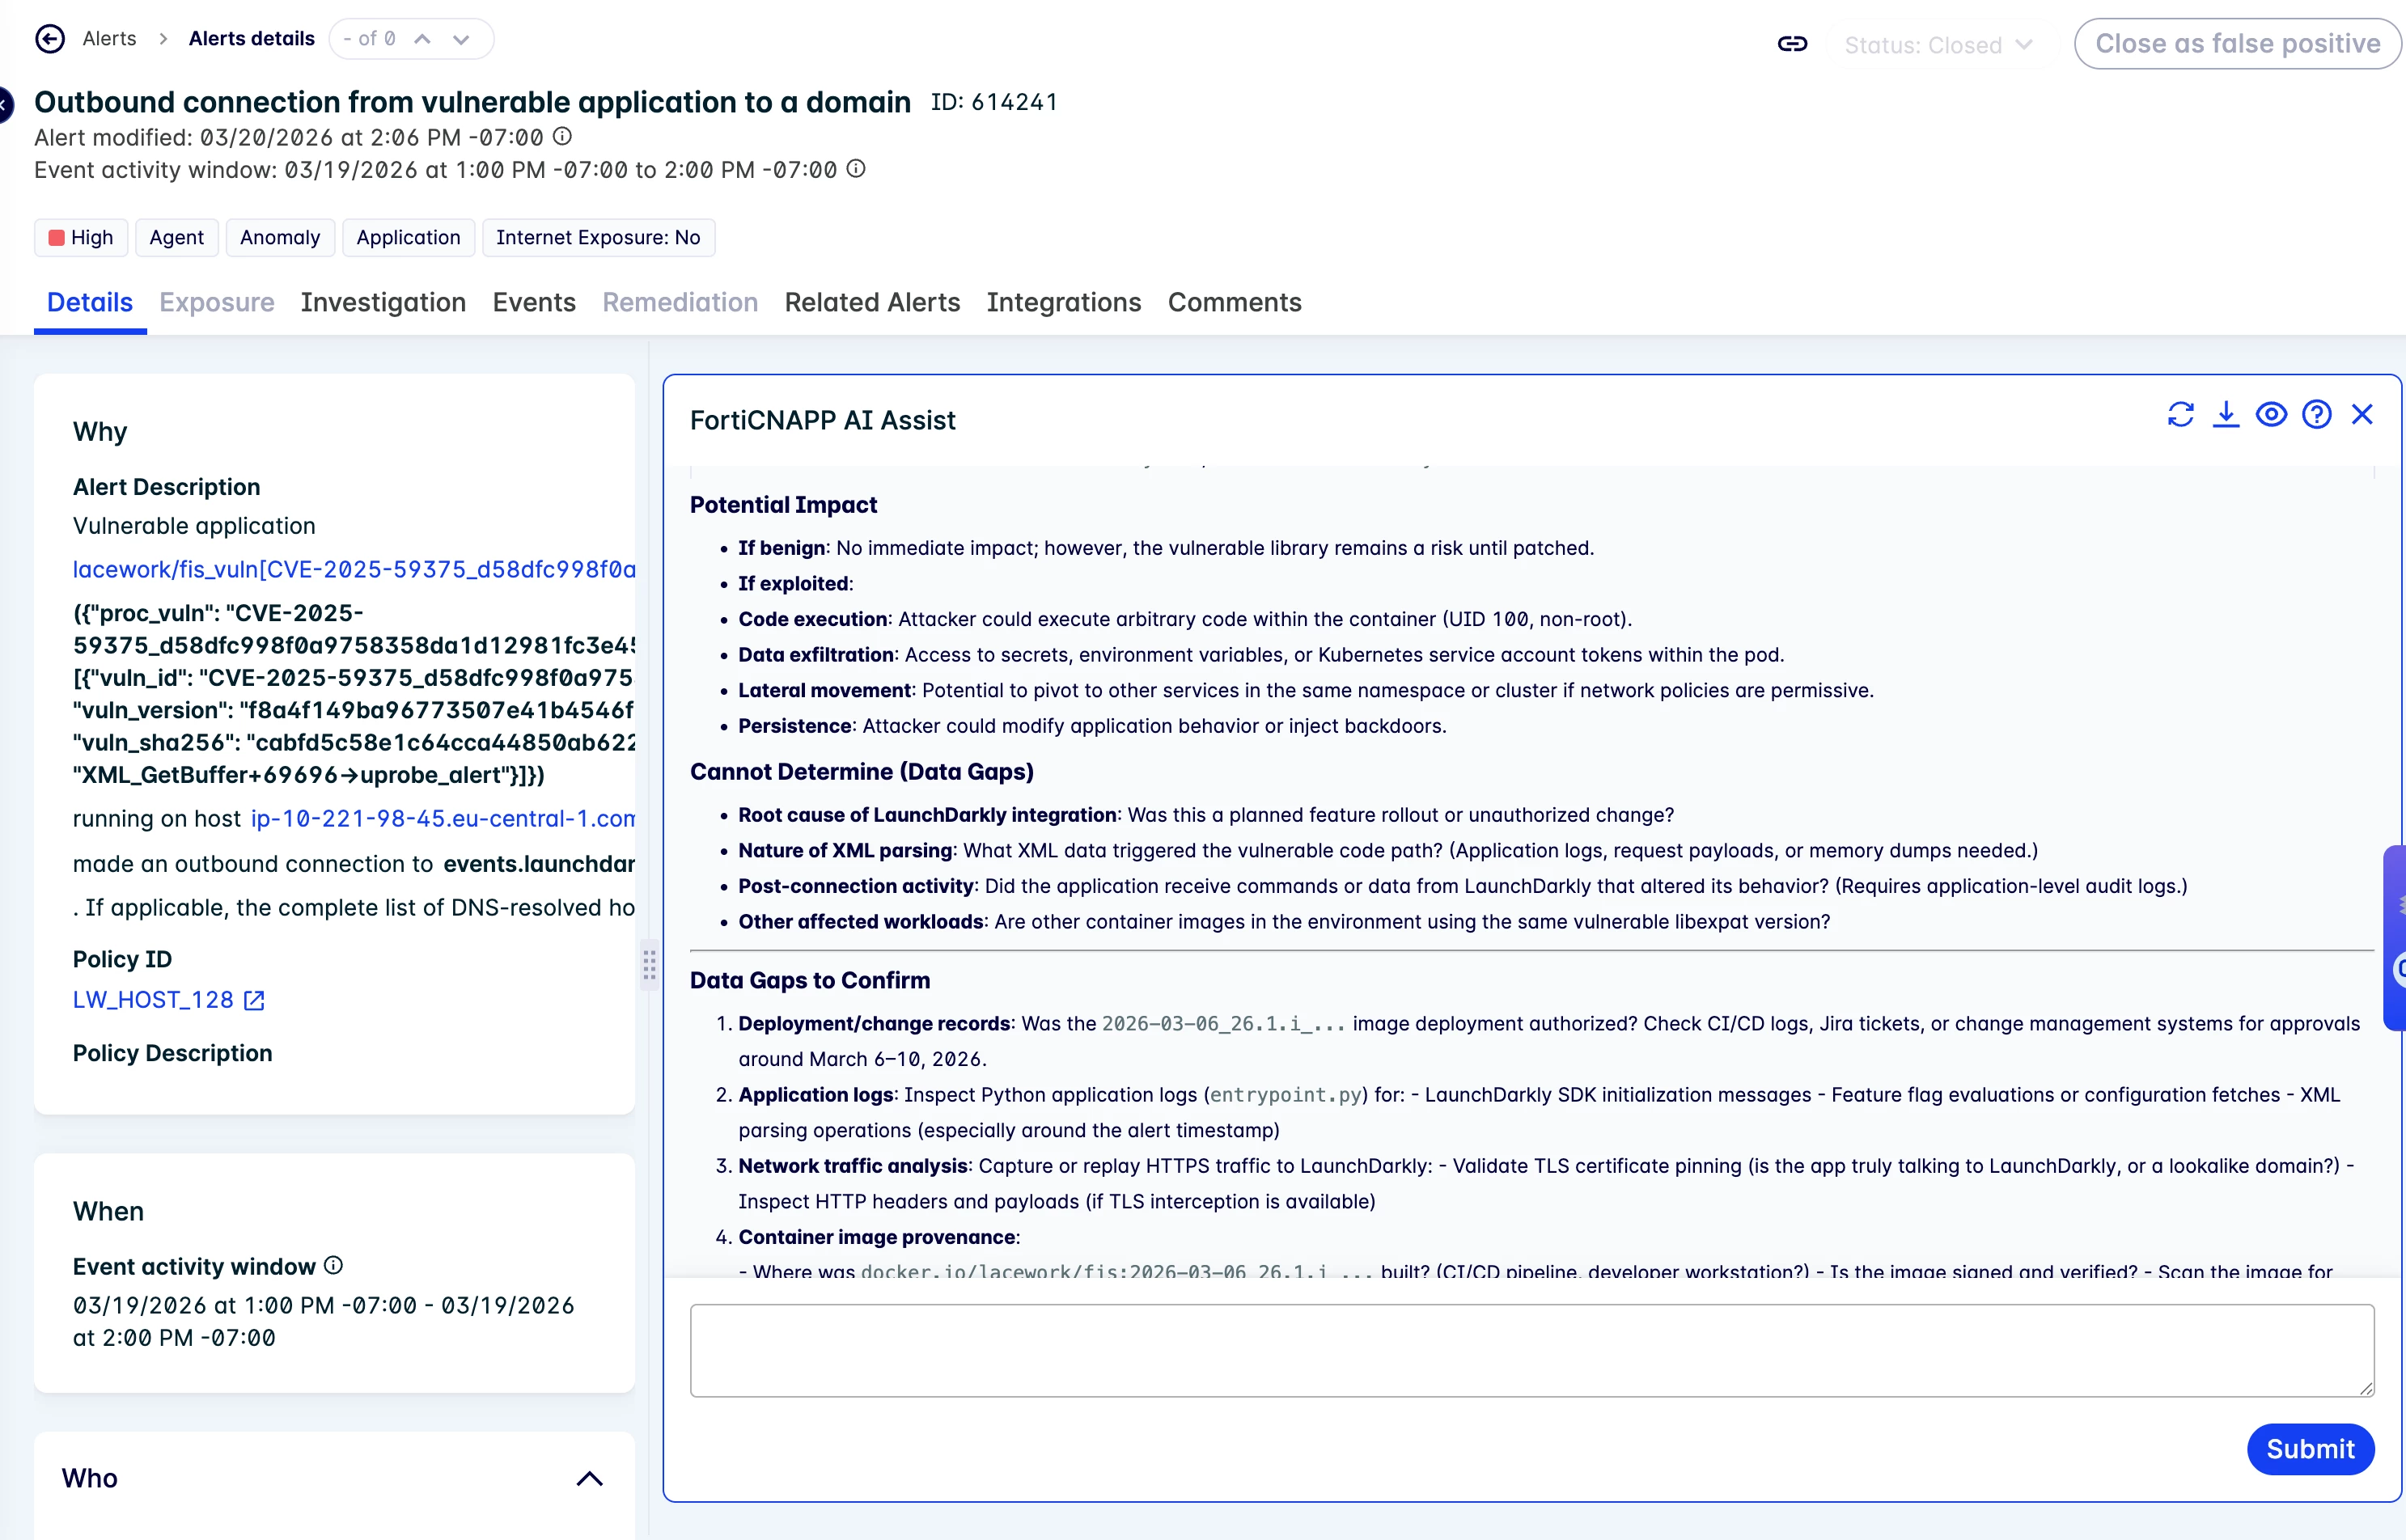
Highlighting Investigation Paths
Potential impact is split into two explicit paths:
- If benign: No immediate impact, but the vulnerable library remains a risk until patched.
- If exploited:
- Code execution within the container
- Data exfiltration of secrets and Kubernetes service account tokens
- Lateral movement to other services in the same namespace
- Persistence via application behavior modification or backdoor injection
The “Cannot Determine” section identifies what remains unknown:
- Root cause of the LaunchDarkly integration — was this a planned feature rollout or an unauthorized change?
- Nature of the XML parsing — what data triggered the vulnerable code path?
- Post-connection activity — did the application receive commands that altered its behavior?
- Wider exposure — do other container images in the environment use the same vulnerable libexpat version?
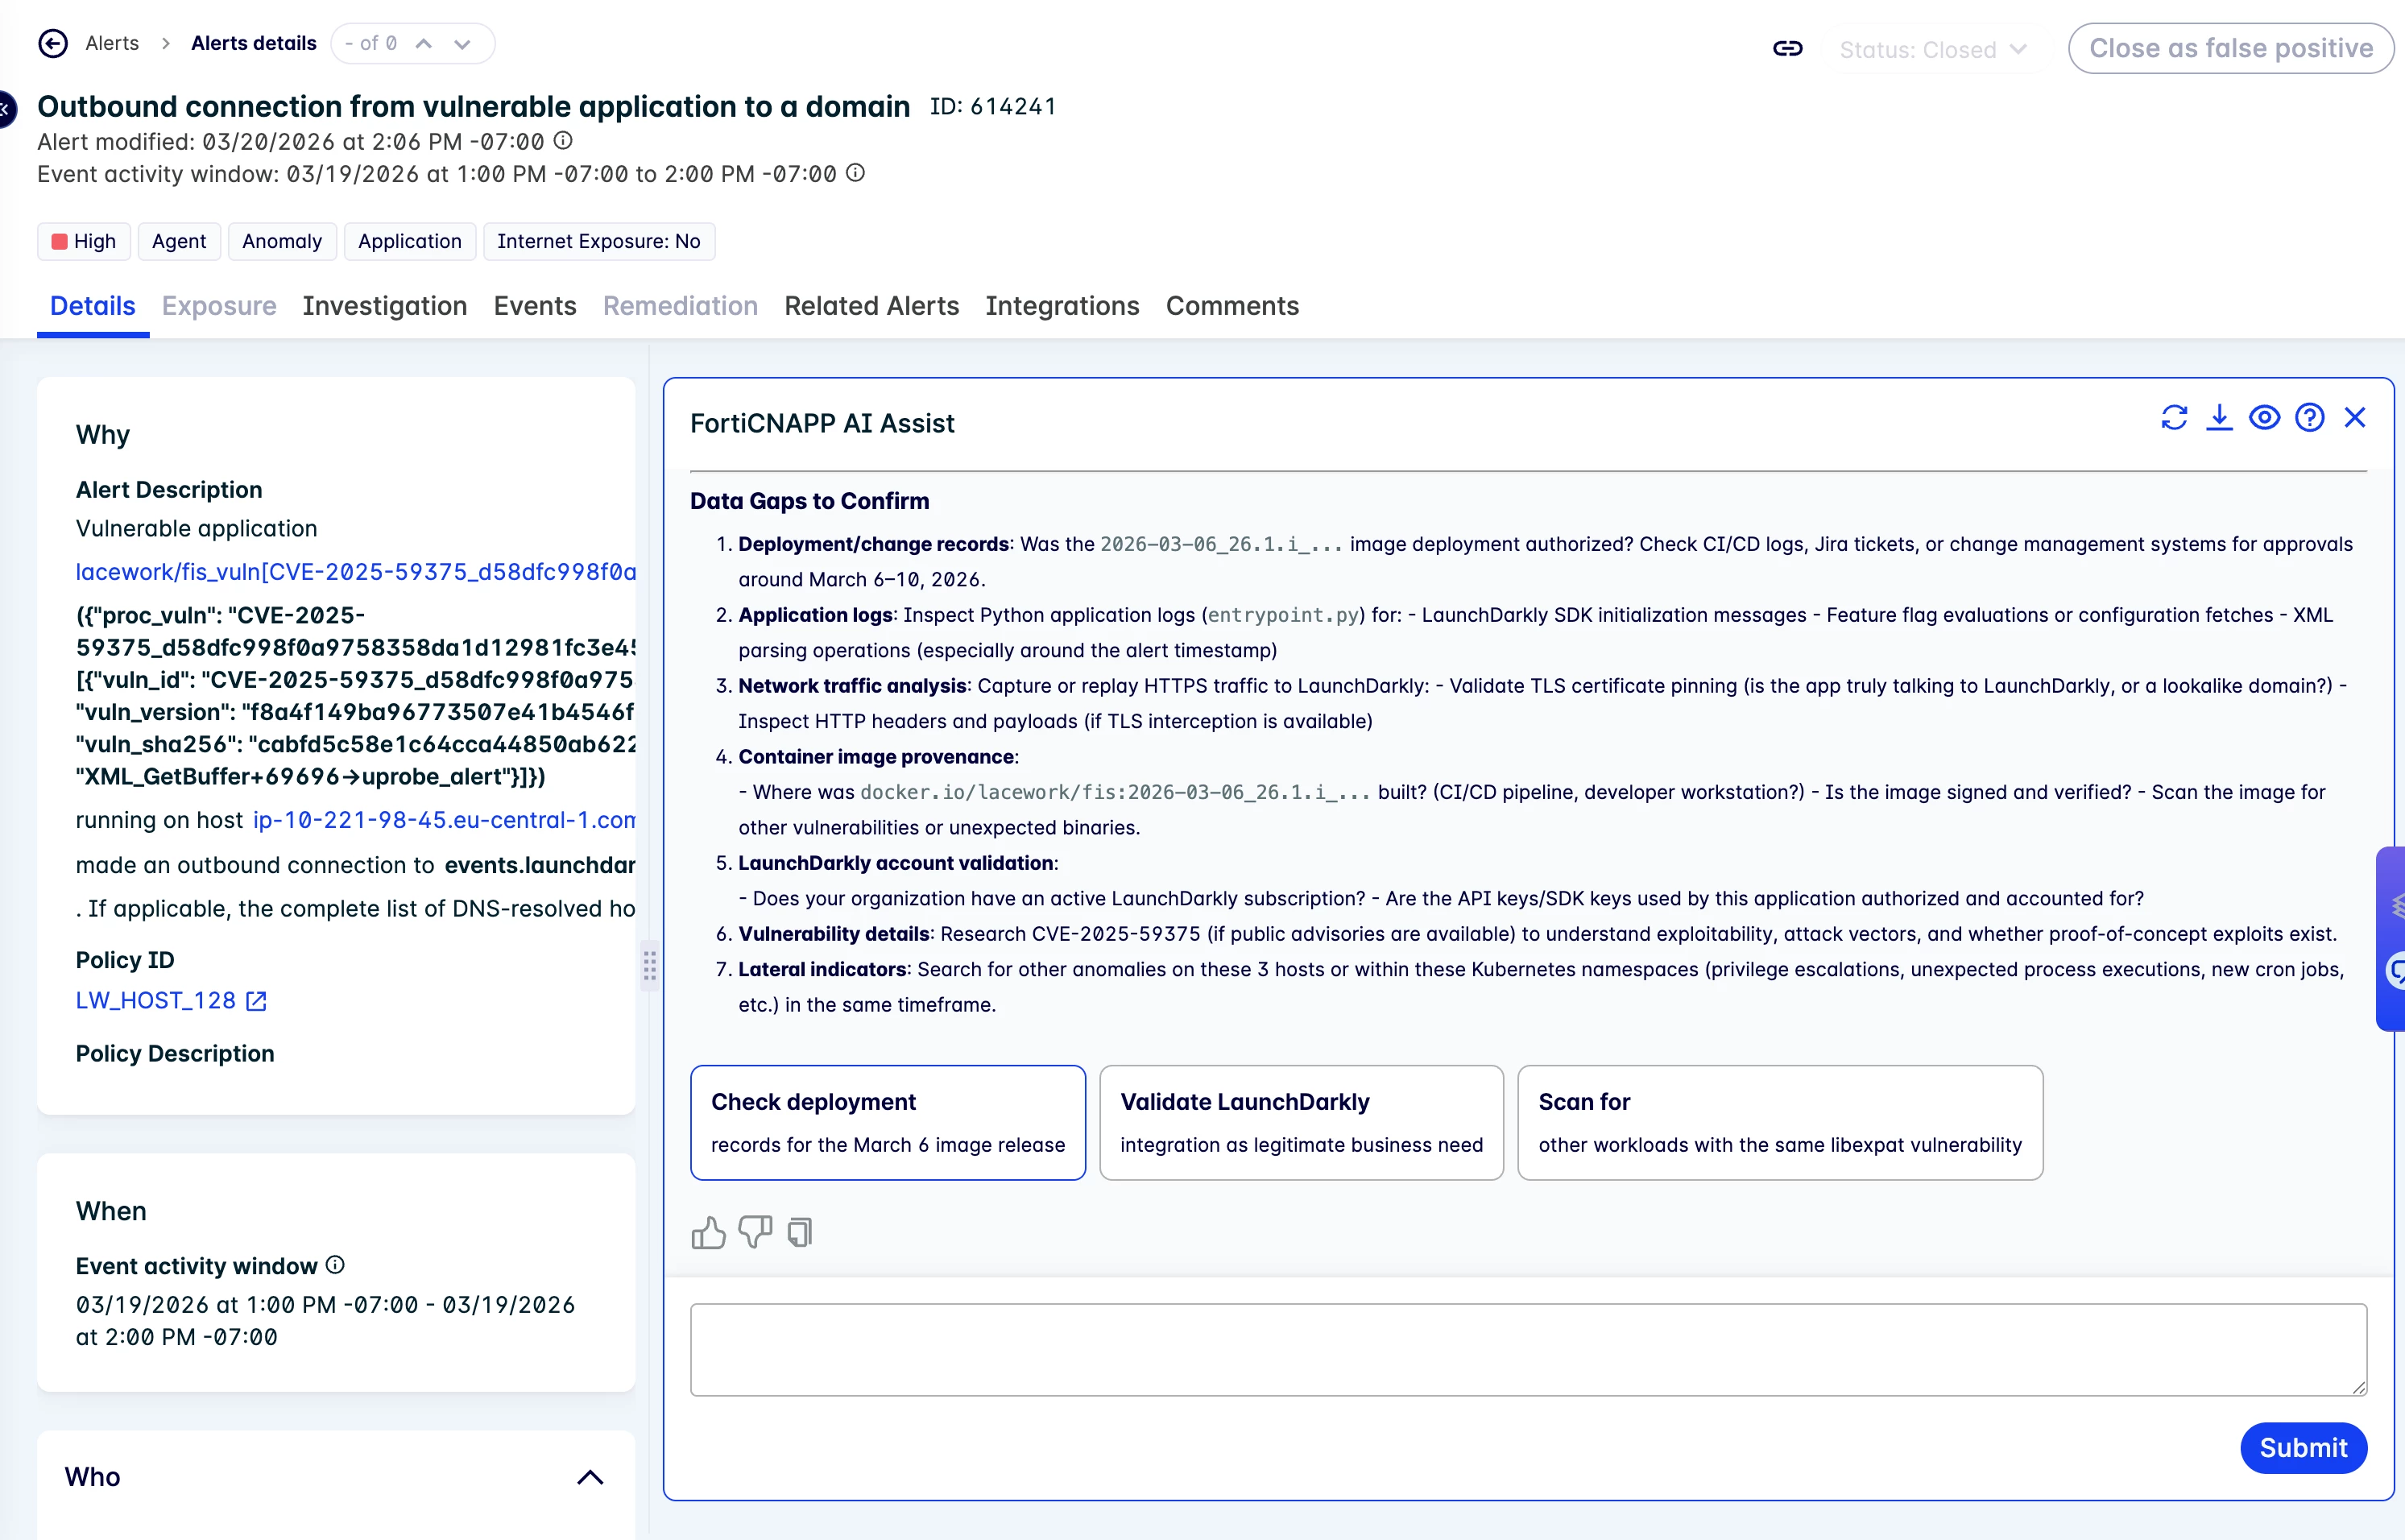
Enumerating Action Plan
Data Gaps to Confirm are numbered and specific — not generic "investigate further" placeholders. Check CI/CD logs and change management systems for the image deployment step. Inspect Python application logs for LaunchDarkly SDK initialization and XML parsing operations. Capture or replay HTTPS traffic to LaunchDarkly to validate TLS certificate pinning. Verify container image provenance. Check whether the organization has an active LaunchDarkly subscription with authorized API keys. Research CVE-2025-59375 exploitability and attack vectors. Search for lateral indicators on the same three hosts and within the same Kubernetes namespaces. The session closes with suggested action chips: Check deployment records for image release version, Validate LaunchDarkly integration as legitimate business need, Scan for other workloads with the same libexpat vulnerability. One click to continue without drafting a new prompt.
That is what one interaction with AI Assist produced — a headline, three prioritized findings with evidence and confidence levels, a reconstructed timeline, a confirmed scope table, a branching impact assessment, a list of what cannot yet be determined, and numbered data gaps with specific sources to check. The analyst knows exactly what happened, what they don't yet know, and what to do next. For a full walkthrough of the AI Assist remediation flow end-to-end, see the embedded demo below.
Where AI Assist goes from here
The newest AI features and capabilities close the most critical gap in cybersecurity — getting analysts from alert to action without requiring them to be detection engineers. The roadmap pushes further in three directions.
Dedicated AI Summary and AI Remediation tabs will become standard UI across all alert types, giving every alert a consistent entry point into AI-assisted triage regardless of detection source. Richer entity and timeline pivots will let analysts jump from an AI Assist finding directly into investigation workflows — clicking on a host, identity, or IP in the AI response will open the relevant investigation context without breaking flow.
The direction is clear: AI Assist isn’t a chatbot stapled onto an alert page. It’s becoming the primary investigation and response interface for FortiCNAPP — one that acknowledges that no analyst has the full security and vulnerability surface and can partner with the security and organizational nuances of each security team. The FortiCNAPP product respects the ambiguity inherent in real-world alerts and continues to get progressively more capable without burdening the analyst with picking up limitless security skills and learning attack topologies of each new attack surface.
Conclusion
The through-line across every update described here is the same: reduce the distance between signal and action. Alert UX improvements make the triage environment faster to navigate. AI Assist turns rich detection output into structured, prioritized narratives with explicit confidence reasoning. Context-aware remediation delivers specific, entity-grounded response steps at the moment they're needed. And the RiskWatch integration demonstrates the speed at which teams can move from detection to remediation when the pipeline is working end-to-end — two production applications running vulnerable code identified and resolved within hours of the first signals going live.
Strong detection is the foundation — without accurate signals, none of this is possible. These updates deliver vast improvements to speed, accessibility, and reliability in everything that comes after detection — for every analyst on the team.

