Mark a Best Answer
Fortinet Community
Recently active
What is CVE-2024-4577? CVE-2024-4577 is a severe security vulnerability found in PHP installations running in CGI mode. This flaw arises from inadequate input data handling, which can lead to attackers injecting and executing arbitrary PHP code on the server. The issue affects PHP versions prior to 8.1.29, 8.2.20, and 8.3.8. Due to its nature, the vulnerability poses a significant risk to many web applications, potentially allowing unauthorized users to compromise the server and execute malicious code. This can lead to various security breaches, including data theft, server control, or disruption of services. Users of affected PHP versions should prioritize upgrading to patched versions to mitigate this critical risk. The Significance of CVE-2024-4577 The exploitation of CVE-2024-4577 can lead to remote code execution (RCE), enabling attackers to perform a variety of malicious activities such as deploying malware and launching denial-of-service attacks. I
Exciting new updates have landed in FortiSOAR! As always, we’ve been working around the clock (and maybe over-caffeinated) to bring you the tools and integrations that make your cybersecurity life a whole lot easier—because fighting cyber threats shouldn’t feel like you're fighting a dragon without a sword - or the armor! Here’s what’s new: Integrate Bitbucket into your security operations and manage your repositories like a pro. Now, you can squash bugs in both your code and your network with one swoop. It’s like being a ninja, but with fewer flips. FortiSOAR now supports Cisco ESA (REST), making email security integrations smoother than Steve’s ‘reply all’ email faux pas in accounting. Stop email threats in their tracks before they get a chance to CC the entire company. Add and manage code snippets directly within FortiSOAR. Save yourself from the dreaded “where did I put that code?” scavenger hunt. Let’s face it, why reinvent the wheel when you can copy and past
What is the Critical D-Link NAS Vulnerabilities (CVE-2024-3272 and CVE-2024-3273)? Critical vulnerabilities CVE-2024-3272 and CVE-2024-3273 have been identified in multiple D-Link NAS (Network Attached Storage) devices. CVE-2024-3272 involves hard-coded credentials that could enable unauthorized remote access, while CVE-2024-3273 presents a command injection flaw that allows attackers to execute arbitrary commands on the devices. Both vulnerabilities are currently being exploited in the wild and pose severe security risks. Immediate action is required to protect affected systems. The Significance of CVE CVE-2024-3272 and CVE-2024-3273 are critical vulnerabilities identified in a widely used software component that poses a significant security risk. This vulnerability allows attackers to exploit a flaw in the software to execute arbitrary code remotely, without requiring any user interaction. The affected software, being prevalent in various applica
Exciting Updates for Our Top Cybersecurity Solutions! Hello FortiSOAR community! We're buzzing with excitement as we unveil the latest updates to our most popular Solution Packs and Connectors! These top-tier tools are designed to elevate your security operations to new heights. Imagine taking a stroll down the tech aisle, but instead of random gadgets, you're picking up powerful solutions to combat cyber threats like a seasoned superhero—cape optional, of course. Prepare to arm yourself with what's trending and effective in cybersecurity, so you can tackle incidents and manage alerts like a pro! Lacework FortiCNAPP Composite Alert Incident Response v1.0.0: Wave goodbye to being buried under alerts! This pack helps you manage and respond to incidents with all the grace of a Jedi swatting away pesky droids. Outbreak Response - Russian Cyber Espionage Attack v1.0.0: Strengthen your defenses against those stealthy cyber espionage strikes. It's like having a secret age
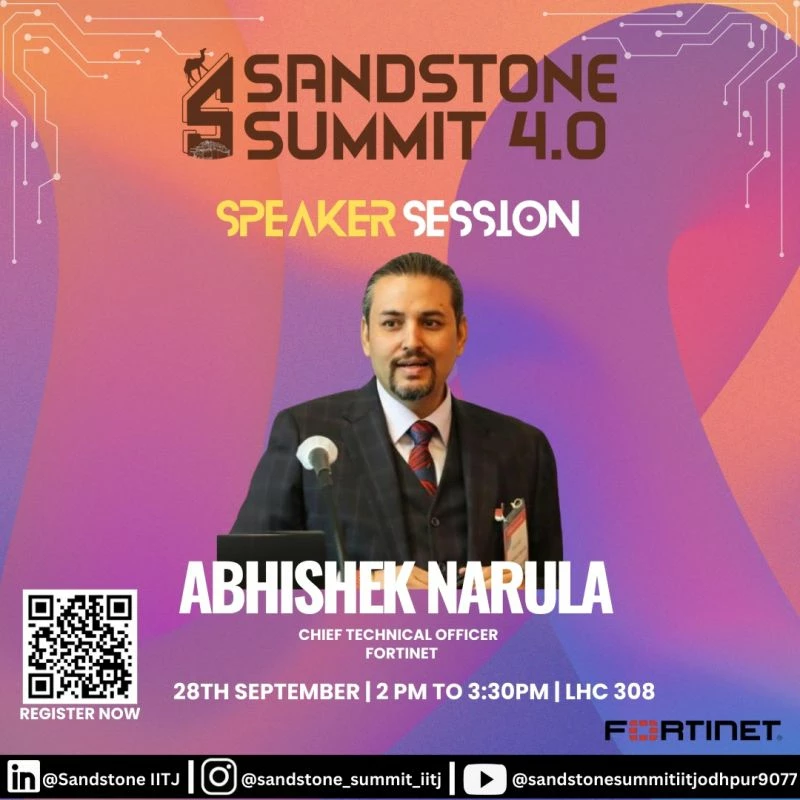
Abhishek Narula, CTO (SOAR Business), would be talking about "Building Career in Cybersecurity & AI" at IIT Jodhpur Sandstone Summit 4.0 https://www.linkedin.com/feed/update/urn:li:activity:7244574804937195521/
I am a BIG supporter of Central NAT. I believe it is in-line with the present day firewall platforms. Even if you use Policy NAT (the original way on FortiOS) or Central NAT you normally want bidirectional NAT'ng, that is SNAT and DNAT. DNAT / VIP There is a feature on the CLI of the VIP which makes the VIP bi-directional. That command is set nat-source-vip enable. This is NOT enabled by default. You can get to the VIP settings by right-clicking the VIP and choosing edit in cli Once you are in the cli you can type set ? and it will show you all of the set options available to you. You can also give the show full to see all the options, default and or custom. The other option you can type is tree which gives you the entire command structure for that section. Once you shell out to the cli FortiOS will show you the basic configuration for that VIP config firewall vip edit "OBSER" set uuid 169ccfa6-a
We're pleased to announce the release of FortiSOAR 7.6.0. This release includes many new enhancements, including: A new cost effective starter edition license for SME environments with less than 10,000 actions per day A High Availability (HA) node license for cost effective HA clustering Trial license updated to 1,000 actions per day Upgrade process improvements A range of user interface enhancements, including code editing improvements Many solution pack, connector, and widget enhancements and more... Check the 7.6.0 release notes for full details:https://docs.fortinet.com/document/fortisoar/7.6.0/release-notes/269885/new-features-and-enhancements
A customer-facing FAQ is available in the FortiSASE Admin Guide for existing FortiClient EMS customers interested in shifting from FortiClient EMS to FortiSASE for endpoint management:https://docs.fortinet.com/document/fortisase/latest/administration-guide/90443/shifting-from-forticlient-ems-to-fortisase This FAQ provides guidance about licensing and FortiSASE configuration for endpoint management for these cases: 1. Existing FortiClient EMS on-premise deployments2. Existing FortiClient Cloud deployments As part of this shift to a FortiSASE deployment, new configuration of endpoint management features must be performed in FortiSASE: Existing FortiClient EMS or FortiClient Cloud configuration is not preserved because FortiSASE uses its own EMS instance. FortiSASE does not support some FortiClient EMS features. To assist customers with new deployments requiring endpoint management features, see the 4-D FortiSASE endpoint management deployment guide:https://docs.fortinet.c
In today's fast-paced digital landscape, the network edge has become a critical battleground for businesses. It's where users connect, data flows, and opportunities arise. But managing this dynamic environment can be a complex and time-consuming task, especially for organizations with distributed networks. That's where FortiEdge Cloud comes in, offering a powerful and intuitive cloud-based management platform that simplifies network operations and empowers businesses to thrive at the edge. Single Pane of Glass Management FortiEdge Cloud provides a centralized platform for managing your entire LAN and WAN edge infrastructure, including FortiSwitch, FortiAP, and FortiExtender devices. With its intuitive interface and powerful tools, you can easily configure, monitor, and troubleshoot your network from anywhere, at any time. The platform's single pane of glass view eliminates the need to juggle multiple management consoles, streamlining operations and saving valuable time and resou
What is CVE-2024-28147? CVE-2024-28147 is a critical security vulnerability that has been identified in the edu-sharing software. The edu-sharing is an open-source e-learning integration solution. The core of the system is a repository for the cooperative creation, management, and usage of objects such as files, links, instances of integrated tools and courses of connected learning management systems such as Moodle. This flaw impacts versions of the software prior to 8.0.8-RC2, 8.1.4-RC0, and 9.0.0-RC19. The vulnerability arises from the software's handling of file uploads through the collection preview images feature, which permits authenticated users to upload arbitrary files. Specifically, this issue allows users to upload files such as HTML and SVG files that can contain malicious code. When these files are accessed directly via their URLs, they have the potential to execute malicious JavaScript code. This could lead to unauthorized actions being performed
The Impact of CVE-2024-3651 In the realm of web security, vulnerabilities can often lead to severe consequences if left unaddressed. One such critical issue is identified by CVE-2024-3651, a vulnerability that significantly impacts web applications by exposing them to potential denial-of-service (DoS) attacks and remote code execution (RCE). This essay explores the nature of CVE-2024-3651, its implications for web security, and the importance of addressing such vulnerabilities to maintain robust and secure web applications. CVE-2024-3651 is categorized as a critical vulnerability primarily due to its origin in the improper validation of URL, header, and argument lengths within web applications. Web applications rely on numerous parameters passed through URLs, headers, and request bodies to function correctly. These inputs are crucial for processing requests, managing sessions, and delivering content. However, when an application fails to validate the size of t
New Connectors Alert: Your Security Arsenal Just Got Better! We've new connectors to boost your security toolkit. Whether you're all about the latest threat intel or just need a better way to scan those pesky QR codes (yes, really!), we've got you covered. Let's dive into what's new! LUMU v1.0.0: You asked, we delivered! LUMU is now integrated to help you continuously illuminate your security posture and detect threats in real-time. Your wish is our command! IBM Randori v1.0.0 Another community request making its debut! IBM Randori is here to provide you with attack surface management like never before. It's like having a friendly hacker who's on your side. Exchange v4.5.0 (Updated to Exchange lib 5.4.0) Because no one wants outdated libraries, right? We've polished up the Exchange connector, bringing it to v4.5.0, with an upgraded lib version to keep your email environment running smoother than ever. QR Code Tools v1.0.1 T
Solution overview The Landing Zone Accelerator on AWS (LZA) for Canadian Centre for Cyber Security (CCCS) Cloud Medium is a specialized deployment designed in collaboration with national security entities and government agencies. It facilitates compliance with strict security requirements, offering a comprehensive AWS cloud architecture for handling sensitive workloads. The CCCS Medium Reference Architecture addresses identity and access management, governance, data security, logging, and network design in alignment with various security frameworks, including NIST 800-53, ITSG-33, FEDRAMP Moderate, CCCS-Medium, IRAP, and other medium-level security profiles. Please refer to the CCCS Medium Reference Architecture document for the full detailed design. Note: This solution will not, by itself, make you compliant. It provides the foundational infrastructure from which additional complementary solutions can be integrated. Solution Detail This version of
Introduction D-Link, a global leader in networking solutions and is particularly renowned for its offerings tailored to small and medium-sized businesses (SMBs). Over the decades, D-Link has expanded its product portfolio and global reach, making it a key player in the networking industry. Today there are many device vulnerabilities that have been identified across various D-Link devices, posing significant security risks. CVE-2020-9376: The D-Link DIR-610 devices are affected by an information disclosure vulnerability that exposes sensitive information through inadequately secured getcfg.php endpoints. This issue is particularly problematic because it impacts devices that are no longer supported by D-Link, meaning there are no official updates or patches available to address the vulnerability. CVE-2022-28956: The getcfg.php component in D-Link DIR816L routers with firmware version FW206b01 has a critical vulnerability that allows attackers to gain una
What is Check Point CVE-2024-24919? CVE-2024-24919 is an information disclosure vulnerability that could enable an attacker to access sensitive information on internet-connected Gateways configured with IPSec VPN, remote access VPN, or mobile access software blades. Check Point's advisory notes that this vulnerability has been exploited in the wild, with attacks primarily targeting devices set up with local accounts that use password-only authentication. Using password-only authentication is discouraged due to the risk of brute-force attacks, which can exploit weak passwords. Check Point recommends against using local accounts where possible and recommends implementing added layers of authentication if they are necessary. A hotfix is available to address this issue. Significance of CVE-2024-24919 On May 28, 2024, Check Point issued a zero-day advisory for CVE-2024-24919, which has a CVSS score of 8.6. According to the advisory, this vulnerability allows a
Unveiling some game-changing updates and enhancements for FortiSOAR that include FortiAI, Outbreak Response Framework, and Lacework FortiCNAPP integration — along with other widgets, connectors, and solution packs! Unlock the full potential of Generative AI with FortiAI solution pack! This groundbreaking tool answers your questions with contextual precision on security threats, response processes, work plans, Jinja expressions, and more. The real magic happens with its unique ability to craft customized playbook blocks based on your defined scenarios. Whether you're a seasoned pro or just starting out, FortiAI is your ultimate ally for designing streamlined, efficient playbooks that set you up for success. Stay ahead of the curve with our Outbreak Response Framework! This powerful tool provides essential insights into ongoing cybersecurity attacks that impact numerous organizations and industries. Powered with Fortinet FortiGuard Outbreaks, it is quick to install outbreak
Many of today’s most damaging security breaches result from compromised user accounts and passwords. To address this issue, businesses of all sizes are seeking alternatives to password-only authentication. Multifactor authentication (MFA), whether through traditional hardware tokens orr mobile software tokens, or increasingly popular passkeys for passwordless authentication, has become the standard. Previously, implementing and managing MFA deployments was complex. FortiToken Cloud simplifies this process by offering a secure, effective way to manage MFA through an intuitive interface accessible from anywhere. FortiToken Cloud includes tokens for our FortiToken Mobile App, which features PUSH notification and response technology, making the end user experience as simple as swiping or clicking to approve a login. With FortiToken Cloud we continue to develop new application security features that ensure access to sensitive data and systems is restricted to authorized users o
Why FortiToken Cloud? Many of today’s most damaging security breaches result from compromised user accounts and passwords. To address this issue, businesses of all sizes are seeking alternatives to password-only authentication. Multifactor authentication (MFA), whether through traditional hardware tokens or increasingly popular mobile software tokens, has become the standard. Previously, implementing and managing MFA deployments was complex. FortiToken Cloud simplifies this process by offering a secure, effective way to manage MFA through an intuitive interface accessible from anywhere. FortiToken Cloud includes tokens for our FortiToken Mobile App, which features PUSH notification and response technology, making the end user experience as simple as swiping or clicking to approve a login. With FortiToken Cloud we continue to develop new application security features ensures that access to sensitive data and systems is restricted to authorized users only, thereby reducing
The rapid growth of electric vehicles (EVs) and the corresponding need for extreme fast charging (XFC) infrastructure have highlighted the importance of robust cybersecurity measures. The NIST Cybersecurity Framework Profile for Electric Vehicle Extreme Fast Charging Infrastructure (NIST IR 8473) offers a detailed, risk-based approach to managing cybersecurity in this complex ecosystem. FortiSOAR, with its advanced capabilities, is ideally positioned to help organizations comply with this profile. Here's how FortiSOAR can enhance compliance across the various phases of the NIST framework: Introduction to NIST IR 8473 Electric vehicle (EV) charging stations are critical to the growth of the EV industry, much like gas stations are for traditional vehicles. Countries worldwide are setting ambitious targets to ensure widespread availability of these charging points. For instance, the EU aims for 3 million public charging points by 2030, and the US targets at least
If you haven't used the open source iperf tool before, there is a lot of info on it (see https://iperf.fr), and I will only say it allows us to generate UDP/TCP traffic between 2 hosts of any bandwidth we desire. Load testing is a sure way to pinpoint "weak links" in the network, be it equipment or cabling. So iperf is a software (Linux & Windows) you install on 2 hosts and it works as client and server - one host sends TCP or UDP traffic, and the second one (well, iperf on it) receives it measuring jitter, packet loss, bandwidth. We use iperf to indicate network problems but also to prove (to client or ourselves) capacity of a line - is the claimed throughput indeed as expected? It becomes a challenge when you don't have Windows/Linux on remote site to install iperf or you cannot allow network downtime to disconnect your Fortigate from the line and connect instead laptop/server. Luckily, starting with FortiOS 5.2.x version, all Fortigate firewalls come with
We are excited to announce that new connectors, widgets, and solution packs are now available on the Content Hub. We have also released new versions of existing content with enhanced features and improved performance. Our new connectors enable seamless integration with popular threat intel platforms like Microsoft Graph Mail, ServiceNow, version control systems like GitHub and GitLab, and 600 more! SOAR Framework with version 3.0.0 has been optimized; SLA Management and other utilities are now new solution packs in themselves, complete with playbooks and user flows. The following table summarizes the progress we have made since the last announcement. 1 Solution Pack Platform Utilities v1.0.0 [Doc] 2 Solution Pack SOC Utilities v1.1.0 [Doc] 3 Solution Pack SLA Management v1.0.0 [Doc] 4 Solution Pack SOAR Framework v3.0.0 [Doc] 5 Connector Fortinet FortiEDR v2.0.0 [Doc] 6 Connector Remote FortiSOAR v2.0.0 [Doc] 7 Connector Gitlab v2.0.1 [Doc] 8 Conne
In light of recent cybersecurity events, we would like to remind FortiEDR customers and partners about our software and content update release process, as well as our overarching release strategy. The following overview will detail our various release types, our systematic release process, and the measures we take to mitigate associated risks. Release types: We classify FortiEDR releases into three categories: Major, Minor, and Patch. Major and Minor releases undergo comprehensive QA cycles, followed by internal deployments where the system is tested in our own production environment for several months. Patch releases address a limited set of bugs and are considered less risky. These releases go through QA cycles that focus on the impact of the changed modules and include overall sanity checks. Similar to Major and Minor releases, Patch releases are tested internally for at least a few weeks before being deployed in production. Development and Q
What is CVE-2024-22024? CVE-2024-22024 represents a critical XML External Entity (XXE) vulnerability identified in the SAML (Security Assertion Markup Language) components of Ivanti Connect Secure and Ivanti Policy Secure platforms. This vulnerability impacts versions 9.x and 22.x of these platforms, exposing a significant security risk. An XXE vulnerability arises when an application improperly processes XML input from untrusted sources. In the context of CVE-2024-22024, attackers can exploit this flaw by crafting malicious XML documents designed to interact with external systems or access restricted resources without requiring legitimate authentication. This could potentially lead to unauthorized data disclosure, manipulation of sensitive information, or even complete compromise of affected systems. The implications of CVE-2024-22024 underscore the critical nature of XML processing security. By exploiting XXE vulnerabilities, attackers can bypass intended security c
Introduction With the latest updates to the Let's Encrypt CA certificate, our goal is to ensure minimal disruption to your operations. Let's Encrypt, a highly trusted Certificate Authority (CA) known for providing free SSL/TLS certificates, is set to introduce significant changes in 2024. These updates are designed to enhance security and performance, but they may also affect how certificates are issued and renewed. In this blog post, we will provide a comprehensive overview of the upcoming changes, detailing what you can expect and how they might impact your current setup. Additionally, we will explain how FortiWeb Cloud is equipped to facilitate a smooth transition. Our solutions are designed to seamlessly integrate with the new Let's Encrypt protocols, ensuring that your operations continue without interruption. We will also address any potential challenges that may arise with legacy devices, offering guidance and best practices to mitigate these issues effectively. 
What is CVE-2024-2879? CVE-2024-2879 is a critical security vulnerability identified in the LayerSlider plugin for WordPress, impacting versions 7.9.11 and 7.10.0. This vulnerability centers around an unauthenticated SQL injection exploit that occurs via the ls_get_popup_markup action. The issue stems from inadequate input sanitization and improper handling of SQL queries within the plugin's code. Exploiting CVE-2024-2879 allows attackers to manipulate SQL queries executed by the plugin, potentially enabling unauthorized access to sensitive information stored in the WordPress site's database. Since the vulnerability can be exploited without requiring authentication, malicious actors can craft specially crafted requests to extract confidential data, modify database content, or execute arbitrary commands. For websites running affected versions of the LayerSlider plugin, the risk posed by CVE-2024-2879 is significant. Unauthorized access to sensitive information could co
Already have an account? Login
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.