

Quass
Visitor III
April 15, 2024
Solved

ipv6 - internal lan interface cannot reach internet

  • April 15, 2024
  • 9 replies
  • 3500 views

Hi,

I've configured ipv6 for the first time on my Fortigate 50E with 6.2.16 firmware.

My ISP doesn't give me the option to delegate /56 or /60 subnet but only eight /64 subnets for internal use. So I've connected the wan1 port to the ISP bridge and using link local IPV6 address of the Fortigate WAN1 port I've I've delegated one of the /64 prefix to the Fortigate.

Then I've configured the WAN1 port via CLI in dhcp as follows:


config system interface edit "wan1" config ipv6     set ip6-mode dhcp     set ip6-allowaccess ping       set dhcp6-prefix-delegation enable     end   next end


Next I've configured my lan interface:


config system interface   edit "lan"     config ipv6       set ip6-mode static       set ip6-address xxxx:xxx:xxxx:f2f1::1/64 //the subnet is the same of the one delegated by the ISP       set ip6-allowaccess ping https ssh       set ip6-send-adv enable       set ip6-other-flag enable       config ip6-delegated-prefix-list         edit 1           set upstream-interface "wan1"           set autonomous-flag enable           set onlink-flag enable           set subnet ::/64           set rdnss-service default         next       end     end   next end


And then I've configured the dhcp server


config system dhcp6 server     edit 1         set rapid-commit enable         set subnet ::/64         set interface "lan"         set upstream-interface "wan1"         set ip-mode delegated     next end


With this configuration i can reach google ipv6 address, from cli via wan1 (that exit to the net with the same ipv6 address of the lan interface):
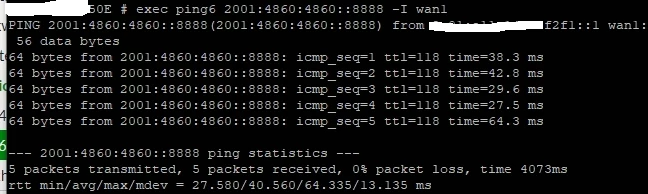
Immagine 2024-04-15 1634333.png

But is unreachable from the lan interface:
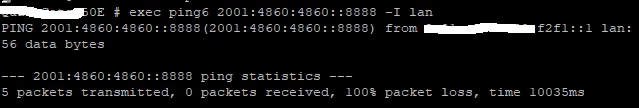
Immagine 2024-04-15 164056.png

I've also created ad IPV6 policy from lan to wan1 that allow the traffic from any source to any destination always scheduled and for all service, NAT disabled. And I've created a static IPV6 route to all destionation (::/0) to wan1.

I've tried with gateway :: or the link local address of the ISP bridge and the google site is reachable via wan1 only.

Where am I wrong with this configuration?

thanks in advance

Best answer by AlexC-FTNT

and ultimately, check that the ipv6 IP that is sourced in the debug flow is part of the subnet defined on the lan, and it matches the subnet defined in the policy "source"

9 replies

AlexC-FTNT
Staff
Staff
April 16, 2024
Quass
QuassAuthor
Visitor III
April 16, 2024

I've tried to sniff packets using google IPV6 as destination and that's the results. Did you have any other suggestion? Can I do something different?


Thanks in advance

diagnose sniffer packet lan 'host 2001:4860:4860::8888' interfaces=[lan] filters=[host 2001:4860:4860::8888] id=20085 trace_id=21 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9728->2001:4860:4860::8888:128) from local." id=20085 trace_id=21 func=resolve_ip6_tuple line=4663 msg="allocate a new session-000067ba" id=20085 trace_id=22 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9728->2001:4860:4860::8888:128) from local." id=20085 trace_id=22 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067ba, original direction" id=20085 trace_id=23 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9728->2001:4860:4860::8888:128) from local." id=20085 trace_id=23 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067ba, original direction" id=20085 trace_id=24 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9728->2001:4860:4860::8888:128) from local." id=20085 trace_id=24 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067ba, original direction" id=20085 trace_id=25 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9728->2001:4860:4860::8888:128) from local." id=20085 trace_id=25 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067ba, original direction" ^C 0 packets received by filter 0 packets dropped by kernel   diagnose sniffer packet wan1 'host 2001:4860:4860::8888' interfaces=[wan1] filters=[host 2001:4860:4860::8888] id=20085 trace_id=26 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9984->2001:4860:4860::8888:128) from local." id=20085 trace_id=26 func=resolve_ip6_tuple line=4663 msg="allocate a new session-000067c1" 4.905392 xxxx:xxx:xxxx:f2f1::1 -> 2001:4860:4860::8888: icmp6: echo request seq 1 4.932686 2001:4860:4860::8888 -> xxxx:xxx:xxxx:f2f1::1: icmp6: echo reply seq 1 id=20085 trace_id=27 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9984->2001:4860:4860::8888:128) from local." id=20085 trace_id=27 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067c1, original direction" 5.918478 xxxx:xxx:xxxx:f2f1::1 -> 2001:4860:4860::8888: icmp6: echo request seq 2 5.946118 2001:4860:4860::8888 -> xxxx:xxx:xxxx:f2f1::1: icmp6: echo reply seq 2 id=20085 trace_id=28 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9984->2001:4860:4860::8888:128) from local." id=20085 trace_id=28 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067c1, original direction" 6.938478 xxxx:xxx:xxxx:f2f1::1 -> 2001:4860:4860::8888: icmp6: echo request seq 3 6.965031 2001:4860:4860::8888 -> xxxx:xxx:xxxx:f2f1::1: icmp6: echo reply seq 3 id=20085 trace_id=29 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9984->2001:4860:4860::8888:128) from local." id=20085 trace_id=29 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067c1, original direction" 7.958474 xxxx:xxx:xxxx:f2f1::1 -> 2001:4860:4860::8888: icmp6: echo request seq 4 7.985291 2001:4860:4860::8888 -> xxxx:xxx:xxxx:f2f1::1: icmp6: echo reply seq 4 id=20085 trace_id=30 func=resolve_ip6_tuple_fast line=4529 msg="vd-root:0 received a packet(proto=58, xxxx:xxx:xxxx:f2f1::1:9984->2001:4860:4860::8888:128) from local." id=20085 trace_id=30 func=resolve_ip6_tuple_fast line=4567 msg="Find an existing session, id-000067c1, original direction" 8.978511 xxxx:xxx:xxxx:f2f1::1 -> 2001:4860:4860::8888: icmp6: echo request seq 5 9.006063 2001:4860:4860::8888 -> xxxx:xxx:xxxx:f2f1::1: icmp6: echo reply seq 5 ^C 10 packets received by filter 0 packets dropped by kernel
AlexC-FTNT
Staff
Staff
April 16, 2024

The outputs are a little mixed up. There is no need to add the "lan" or "wan" as interface filter in the sniffer. Use "any" and should cover both network segments. 

Debug flow shows that packets are sent out. It seems that the return packet is either not seen, or not captured by the debug flow. That could be the key to solving the problem. Could you run the debug flow with a wider filter (for example, only "filter proto icmp") with the sniffer on "any" interface?