Hi,
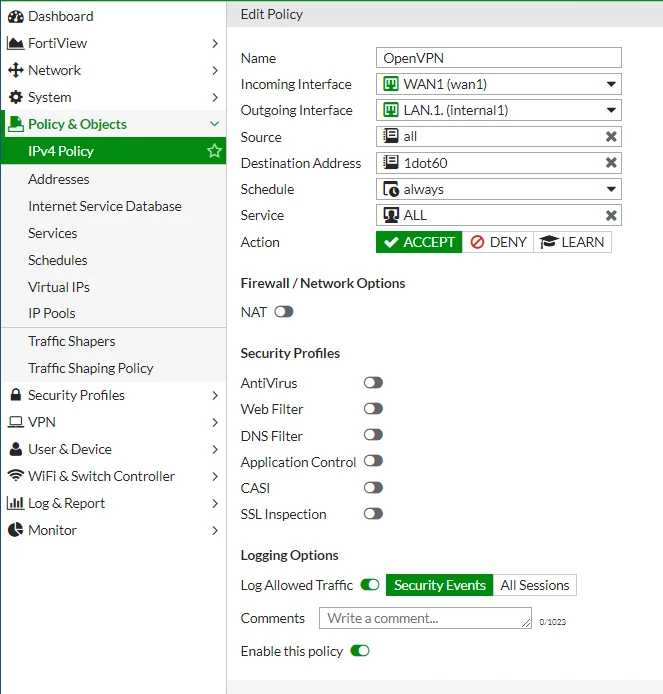
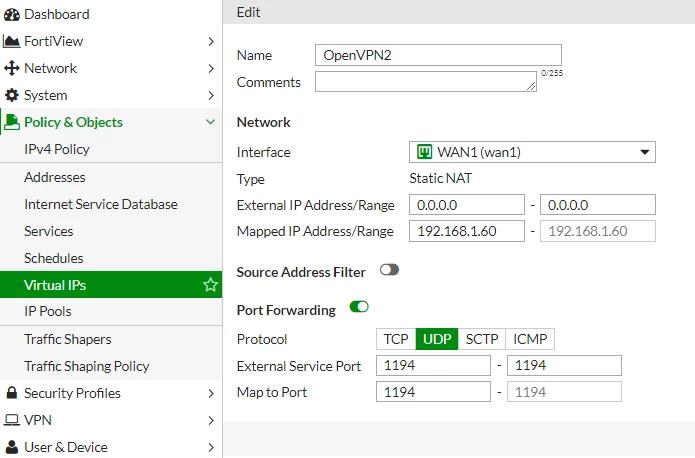
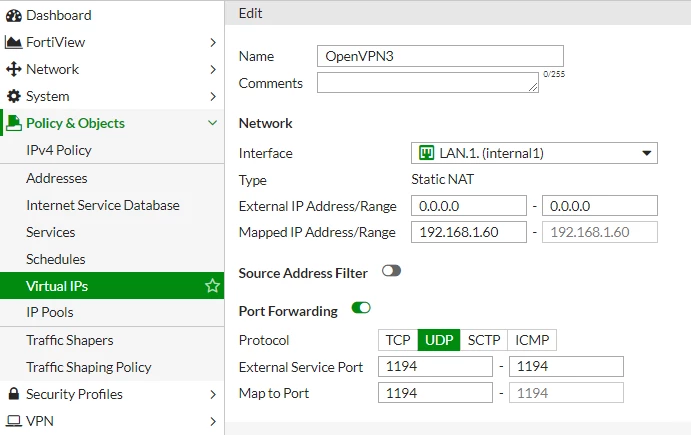
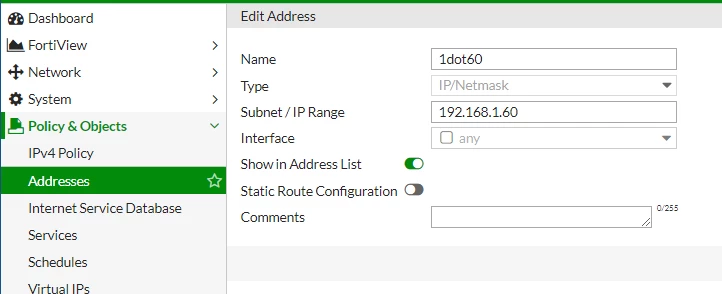
To answer your question about VIP and named addresses as destination. They have different roles, first one should be used when you are trying to grant access to a port fwd from the Internet to your server/services in LAN, the last is when you are need to create firewall rules between different interfaces locally, LAN1 > LAN2 , LAN1 > WAN, etc.
Is your WAN having a static IP or is it via PPPoE/DHCP ? I would recommend if it's a static IP to have in the VIP configuration of OpenVPN2, manually entering the public IP addr in the external address range.
Also, the firewall policy should look like, wan > lan , all > VIP .
I assume that the local subnet 192.168.1.0/24 is defined locally on internal1 interface and not on another one, right ?
You can run the following commands to see if the traffic on port UDP/1194 is reaching the firewall and if it's permitted.
diag debug en
diag debug flow filter saddr <pub ip of initiatior>
diag debug flow filter daddr <private ip of openvpn srv>
diag debug flow trace start 100
afterwards, you can stop it with
diag debug flow trace stop
diag debug disable