

luca1994
Explorer III
February 19, 2024
Solved

Info about user identification

  • February 19, 2024
  • 3 replies
  • 2116 views

Hello team,


I have the users of a branch office that to go out on the Internet they do this circuit

VLAN_Client --> FGT-200F --> MPLS Circuit --> FGT-400F

On the 400F firewall various browsing profiles are configured which according to the AD group they belong to are assigned a Lite,Full or Basic browsing profile.

Now looking at the logs on the 200F side (defult gateway VLAN_Client) I see correctly the IP address with the domain username
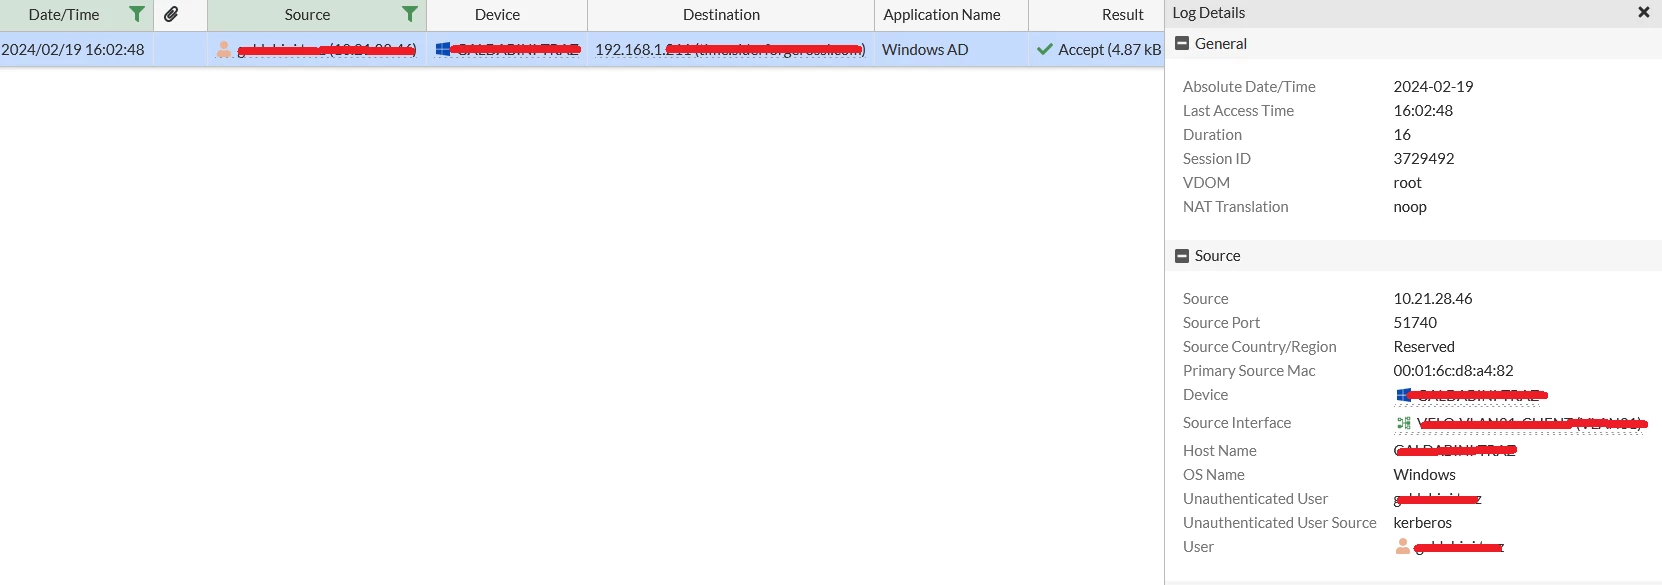
map_user_ip.png

While looking at the logs from the 400F side I see the local ip, the natted ip but not the domain user
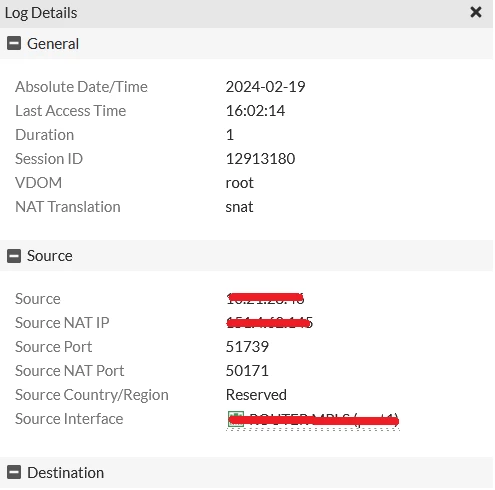
 

map_user.png

and as a result it never matches the policy for the browsing profile since there is an ad group as the source.

How do I see the ip-AD user mapping on the 400F as well? Any suggestions?


Thanks

BR


Best answer by AEK

Hi Luca

You man not need setup FSSO on both. If you just need on one FW, doing user filtering on both FWs may be waste of resources. It depends on your design.

Regarding FSSO setup, take time to read it well before setup because it can be a bit complicated.

We can then guide you with pleasure.

3 replies

AEK
SuperUser
SuperUser
February 19, 2024

Hi Luca

If I'm not wrong you are not using FSSO on 200F neither on 400F.

In that case the user id you see on 200F is collected from client's DHCP request or something similar, and you can't do any filtering based on that.

To be able to filter based on AD group you need setup FSSO.

https://docs.fortinet.com/document/fortigate/7.2.7/administration-guide/450337

Or if you need something simpler you can also use active portal if it is suitable for your case.

https://docs.fortinet.com/document/fortigate/7.2.7/administration-guide/934626

AEK
luca1994
luca1994Author
Explorer III
February 19, 2024

Hello @AEK ,


exactly, i'm not using FSSO. So, if i configure FSSO for both Fortigte (200F e 400F) can i filter by user id? I must install FSSO agent on Windows DCs and configure connector on both firewalls?


Thanks for the support Aek.

BR

AEK
SuperUser
AEKAnswer
SuperUser
February 19, 2024

Hi Luca

You man not need setup FSSO on both. If you just need on one FW, doing user filtering on both FWs may be waste of resources. It depends on your design.

Regarding FSSO setup, take time to read it well before setup because it can be a bit complicated.

We can then guide you with pleasure.

AEK