

Solved
geo blocking
Hello,
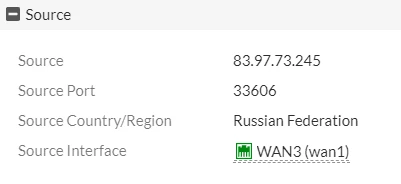
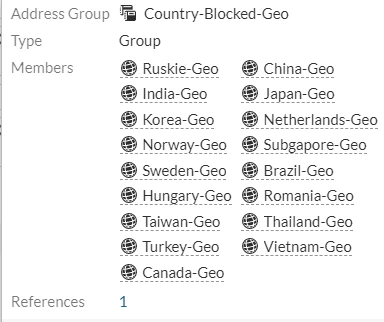
I would like to know what is wrong with this rule, it doesn't work at all, attacks are still coming from the countries that I have added to this rule. Thank you in advance for any suggestions.
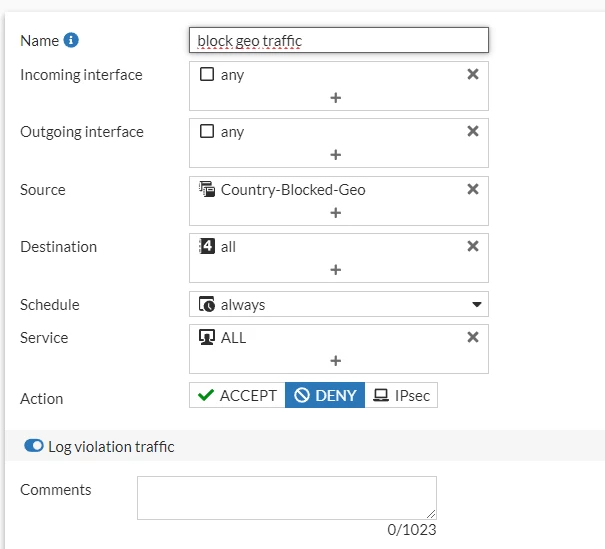

Hello,
I would like to know what is wrong with this rule, it doesn't work at all, attacks are still coming from the countries that I have added to this rule. Thank you in advance for any suggestions.
Hi
Are you blocking traffic passing through the Fortigate? Or are you blocking traffic destined to the Fortigate IP?
If you are blocking traffic passing through the Fortigate, Firewall Policy is effective.
However, if you need to block traffic destined to Fortigate IP, you need to configure Local-in-Policy.
https://docs.fortinet.com/document/fortigate/7.4.4/administration-guide/363127/local-in-policy
Related documentation :
https://community.fortinet.com/t5/Support-Forum/Fortigate-Firewall-policy-vs-local-in-policy/td-p/317063
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.
