

Solved
Policy Ignored - Inter VLAN Routing
Hi,
I can't get a reverse rule to trigger for VLAN communication. VLAN 30 is able to ping VLAN 100, but 100 can't ping 30.
- VLAN 30 Laptop[10.0.30.2] can ping 10.0.100.200, and 10.0.100.1, and 10.0.30.1
- VLAN 100 Laptop[10.0.100.200] can't ping 10.0.30.2, but can ping 10.0.100.1 and 10.0.30.1
- FG and Laptops are connected to 8 ports switch. FG is trunk port. Laptops are VLAN Access Ports 30 and 100 respectively.
- 0 bytes go across 100 -> 30 rule, unless I do Policy Match, then its the 40bytes FG tests with
- I am going to re-start the FG after posting this...just in the event something rules wise effect its. I have about 50 rules, and nothing worked as expected, so I cut down to 3 rules and smaller test setup. The other rules not included are 30 -> Wan (working fine) and Implicit Deny.
Here are screen shots from the Firewall:
 Reset counts to Zero
 Both Laptops doing PING to each other
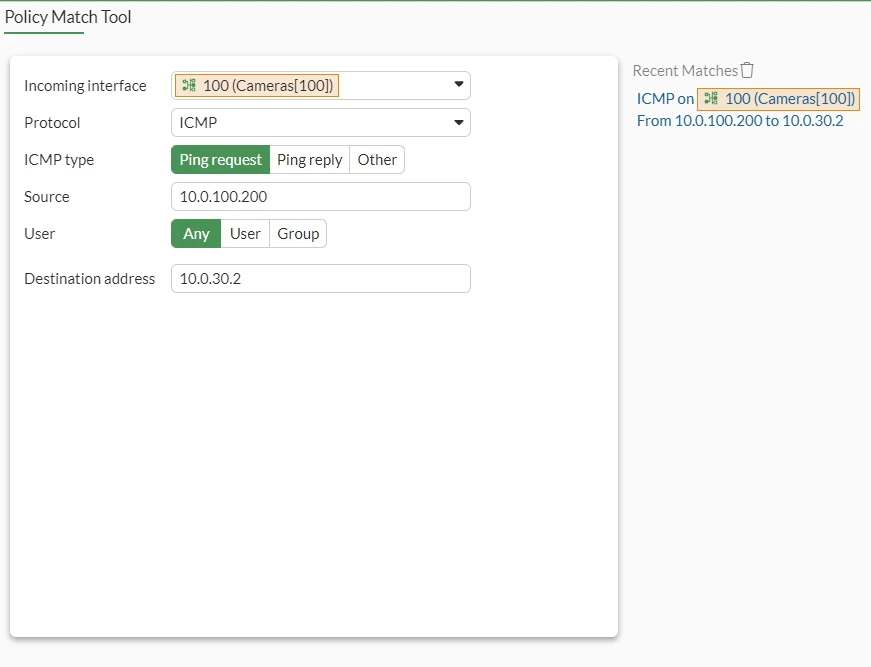 Policy Match
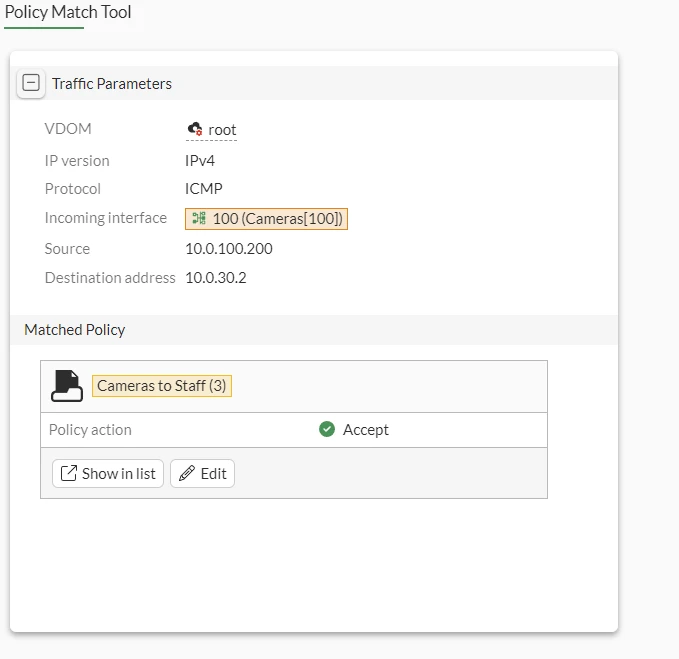 Policy Match Result
 Policy After Policy Match
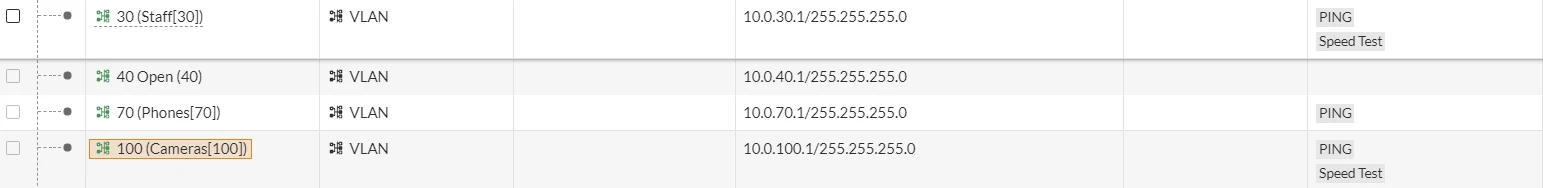 VLAN settings
