
psir
New Member
Apr 24, 2025 10:32 AM UTC
Solved

vpnipsec phase2


hello,

i have problem with my vpn ipsec 

i tried to connect to vpn but i have error during phase 2 


and on wireshark 

i'm stuck at here
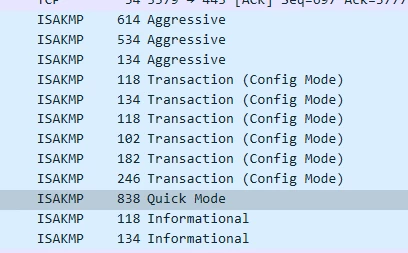
Wireshark_F6l4lemMPC.png


same on forticlient log,  i have no idea why


config :

same auth-encryption for vpn settings and client 

good selectors for phase 2 ( src and dest addresses  )


why quick mode failed ? 

i can share log from CLI 

thanks 

psir
psirAnswer
New Member
Apr 24, 2025 1:14 PM UTC

i know  like i said the error is during phase 2 

i tried at least 20 times new vpn aha 

okay thanks  i will test on other config maybe 


11 replies

funkylicious
SuperUser
SuperUser
Apr 24, 2025 11:59 AM UTC

hi,

some logs would help

"jack of all trades, master of none"
psir
psirAuthor
New Member
Apr 24, 2025 12:05 PM UTC

thanks for your repply @funkylicious 

see logs , i just hide some ip  :


ike V=root:0: comes x.x.x.x:500->xxxxxx:500,ifindex=17,vrf=0,len=572....
ike V=root:0: IKEv1 exchange=Aggressive id=ac4e19fe3023317d/0000000000000000 len=572 vrf=0
ike 0: in AC4E19FE3023317D000000000000000001100400000000000000023C04000064000000010000000100000058010100020300002801010000800B0001000C00040001518080010
007800E008080030001800200018004000E0000002802010000800B0001000C00040001518080010007800E010080030001800200048004000E0A0001045D953284DDC2E84FADC5A883C0F4
84961050A7F03EA46A882B94E94124A7554CF89766395F17B3FD5214236C5770751EF4C60DC2892AF00CE5C350F987EE7670ED03938414FF0192290331715A95CD4679F6650BDAF6E95F89F
4070CDFAB862176453B6894F714C0CD56D77938AE7C876006E3F0FAE8C0BD9EB3899958DF5861F68E5C4FAAF8A17134DF6C57C98D89ED268A92909101AB84A1D0E4D4941C4E5BE5CD06327F
0573DA00A4D95FF6F30B81B03C8F8D2B51258514CB7D2C2E229CBC052F9ECCE7A12F0146A1C5964AF2E333CD7AE14367C55BFAF98314D830E3239D4CF32E16C315BBAF92B6AAA80BF1D9DCA
2C8C7492B0E8C32F190DB6C3CB2685105000014E19BFED6FAC6C6DE47D0FF4AEC6749910D00000C010000009F54224B0D00001412F5F28C457168A9702D9FE274CC01000D0000144A131C81
070358455C5728F20E95452F0D000014CD60464335DF21F87CFDB2FC68B6A4480D00001490CB80913EBB696E086381B5EC427B1F0D00000C09002689DFD6B7120D000014AFCAD

funkylicious
SuperUser
SuperUser
Apr 24, 2025 12:09 PM UTC

i assume that you are using the VPN Only version of FortiClient and not one managed by a EMS.

if so, https://docs.fortinet.com/document/fortigate/7.6.1/administration-guide/710480 try disabling ems-sn-check, which is enabled by default starting with 7.6 


as for phase-2 selectors, i would leave the default ones for src and dst 0.0.0.0/0


L.E. https://community.fortinet.com/t5/FortiGate/Technical-Tip-IPsec-dial-up-full-tunnel-with-FortiClient/ta-p/189452#:~:text=Note%3A-,In%20v7.6%20and%20above%2C,-in%20the%20IPSEC

"jack of all trades, master of none"
psir
psirAuthorAnswer
New Member
Apr 24, 2025 1:14 PM UTC

i know  like i said the error is during phase 2 

i tried at least 20 times new vpn aha 

okay thanks  i will test on other config maybe 


funkylicious
SuperUser
SuperUser
Apr 24, 2025 4:05 PM UTC

how did you solve it ?

"jack of all trades, master of none"
Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT
