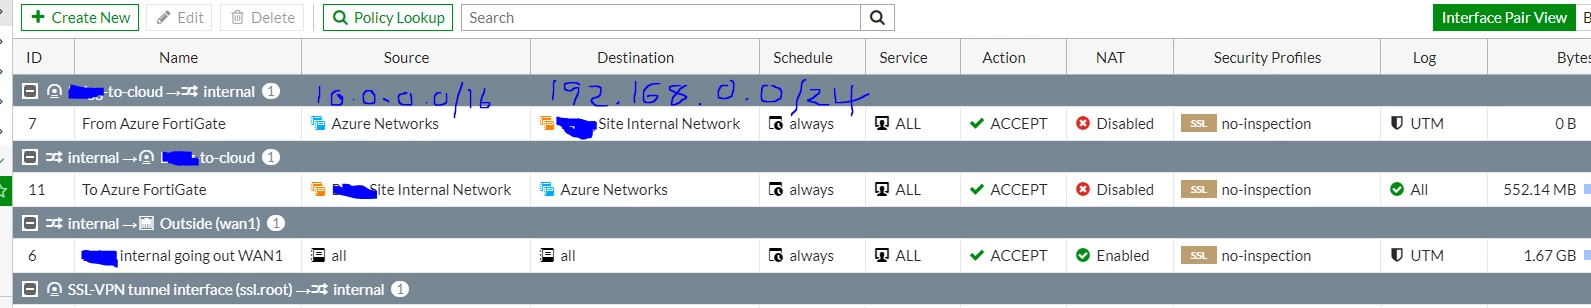
Traffic issue between tunnel interfaces
Sorry to bother people and its my first time on the forum, im hoping people could cast a light on where the issue lies as we are finding that when it comes to our site to site vpn between the Fortigate in the office and the fortigateVM in Azure
when at our branch office we can access our network on the azure portal through the fortigate on the 10.0.x.x range but can not talk to the other vpn tunnels for an example one customers vpn is on a 10.1.x.x range and another company is on a 10.2.x.x and another is 10.3.x.x the only way we can get traffic talking properly from the branch office to the different tunnels is if we use the forticlient vpn to connect into the fortigate azure then traffic has no problem traversing the tunnels
our branch office site that connect to the fortigate azure (cloud-to-br**)