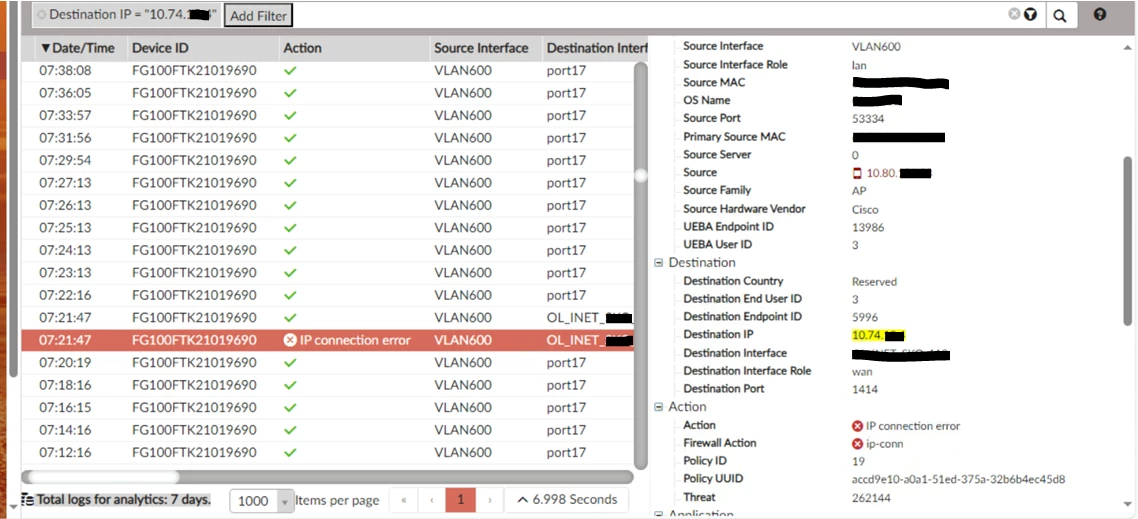
is traffic session
greetings,
here is the scenario:
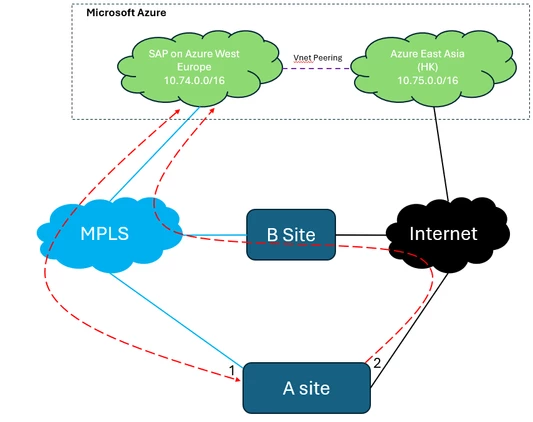
1. there are 2 interfaces on Fortigate at A site as the SD-WAN member interface to Azure, they are link 1(port 17) and 2(OL_INET) in the following picture.
2. normally, FortiGate uses link 1 as the outgoing interface for traffic from site to Azure (so as for the responding traffic from Azure to site), when link 1 fails its performance SLA (let's say, packet loss reached its high threshold), sd-wan will use link 2 for the traffic from site to Azure, but the responding traffic from Azure to site will persists with link 1, as of now, there is only one link (MPLS) from Azure to each site.
question: if there is an existing session established between site and Azure based on link 1, and then link 1 fails its SLA (let's say, packet loss reached its high threshold), which results in a link failover to link 2, what happened to the session? Is the session bundled with the interface which is used by the initial (SYN) packet of the session?
why I ask this is that when the link failover occurred, I see there is an ip connection error logged in traffic log.