Question
IPSec tunnel options - help!
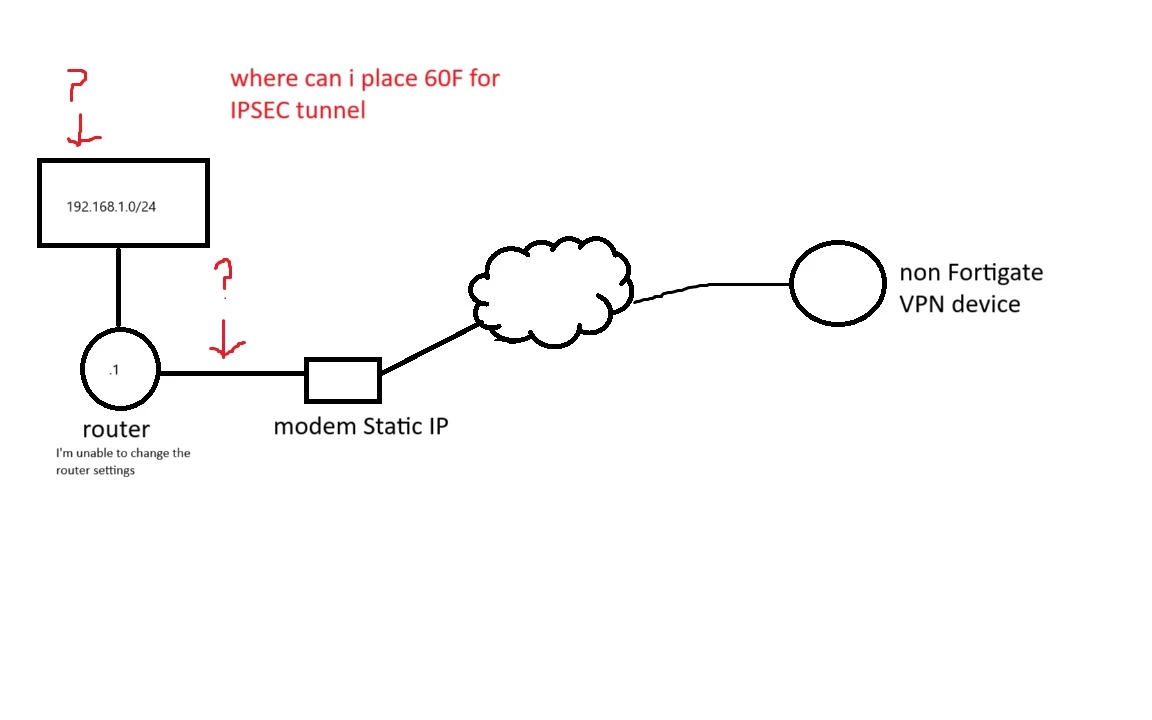
Hi, I have a Fortigate 60F and need to create an IPSEC tunnel to a non-Fortigate device. My problem though is that there is an existing router in my way. I'm unable to remove the router and I can't get into the settings of it. It's needed for the ISP's mesh wi-fi setup I am told.
1. Can i place the Fortigate on the internel network and have it negotiate the tunnel? I don't think it would get the traffic.
2. Put the Fortigate at the edge in transparent mode and establish the tunnel? It doesn't have any L3 addressing so not sure that's possible.
3. Double NAT? yikes