

Wessnitzer
New Member
November 1, 2023
Solved

IPS blocking my own server

  • November 1, 2023
  • 7 replies
  • 5576 views

Hello, it looks like I am doing something wrong and I was not able to find my answer on the internet, so please if someone could enlighten me :)

I have web server, behind nat. Rule set like this:
incoming: wan

Outgoing: lan

source: all

destination: virtual IP of the server

service: https

security profiles: ips high security (modified to quarantine most threats)
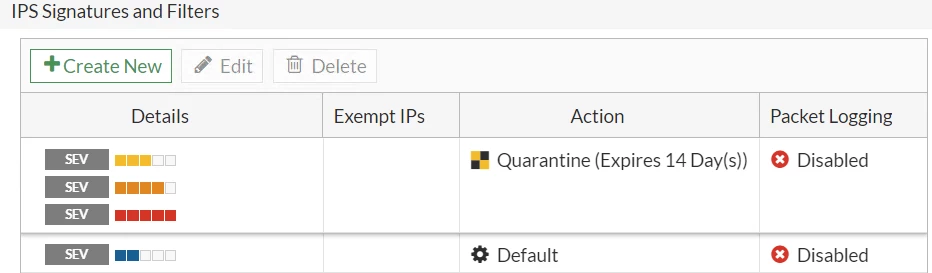


ips.png


 ssl inspection: specific "protecting ssl server" profile


From time to time when there is IPS attack blocked, the IPS puts into quarantine the internal IP of the web server (ie. 192.168.x.x , it is visible in quarantine monitor and can be removed there manually). See below ips log - i suppose the "source" should be blocked, and not "destination" :(
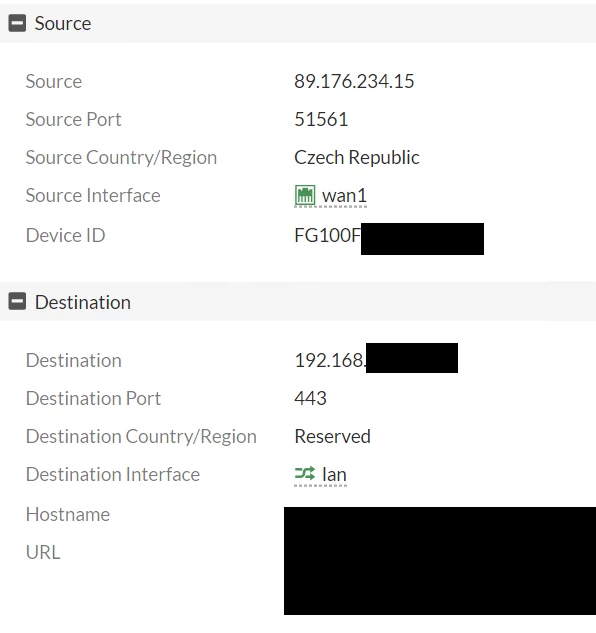
ips log.png


Do you please know what am I doing wrong?
Thank you
Regards
Martin

Best answer by ramadas


Check your IPS Filter :

To better understand the Filter: Please note that Fortinet are providing more than 7000 Signatures to help detect stop and
prevent threats. You need to build your own profile based on your infrastructure.

For severity : You can Choose between Crticial High Medium Low
Target : Client or Server
OS : Linux Windows BSD MacOS
Action : Monitor Block Quarantine

The Sensor is offering you all the possibilities from basic to advanced Filter options.

Thanks

7 replies

Hong_FTNT
Staff & Editor
Staff & Editor
November 1, 2023

Hi @Wessnitzer,


Please check the logs to see which IPS signature and which firewall policy was matched and triggered the quarantine. 


Regards, 

Wessnitzer
New Member
November 2, 2023

Hello, from the logs I see it was the inbound firewall rule to the server (not the outbound rule) with the "high_security" IPS profile, which is used in thus firewall rule.
What is confusing to me is that inbound rule put the destination server into quarantine, not the source attacker.
Regards

ramadas
New Member
November 1, 2023

True that the IPS is there to block attacks from Sources. But, what if the Destination becomes also a malicious ?

My Recommendations are : 

1) Go for a Deep Scan of your Web Server and check for vulnerabilities, specially Bot C&C. This may block your web SIte as Destination and be blacklisted.

2) Read the Logs : Find which Security Profile did block your IP. 

3) Check the Config of the IPS : Section Botnet C&C

Good LuckCapture.PNG

Wessnitzer
New Member
November 2, 2023

Hello,

1) ok i will do full scan

2) security profile "high_security" from the inbound rule from internet to the server. Profile settings screenshot is in original post.

3) scan outgoing connection to botnet is set to block - can this quarantine the server? In this regard block = quarantine?
Thanks
Regards

ramadas
ramadasAnswer
New Member
November 2, 2023


Check your IPS Filter :

To better understand the Filter: Please note that Fortinet are providing more than 7000 Signatures to help detect stop and
prevent threats. You need to build your own profile based on your infrastructure.

For severity : You can Choose between Crticial High Medium Low
Target : Client or Server
OS : Linux Windows BSD MacOS
Action : Monitor Block Quarantine

The Sensor is offering you all the possibilities from basic to advanced Filter options.

Thanks

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
