
didyfink
New Member
Aug 20, 2024 7:24 PM UTC
Question

ha active active deployment consideration

Hello,

i try to learn more from this type of scenario so any help would be appreciated. 

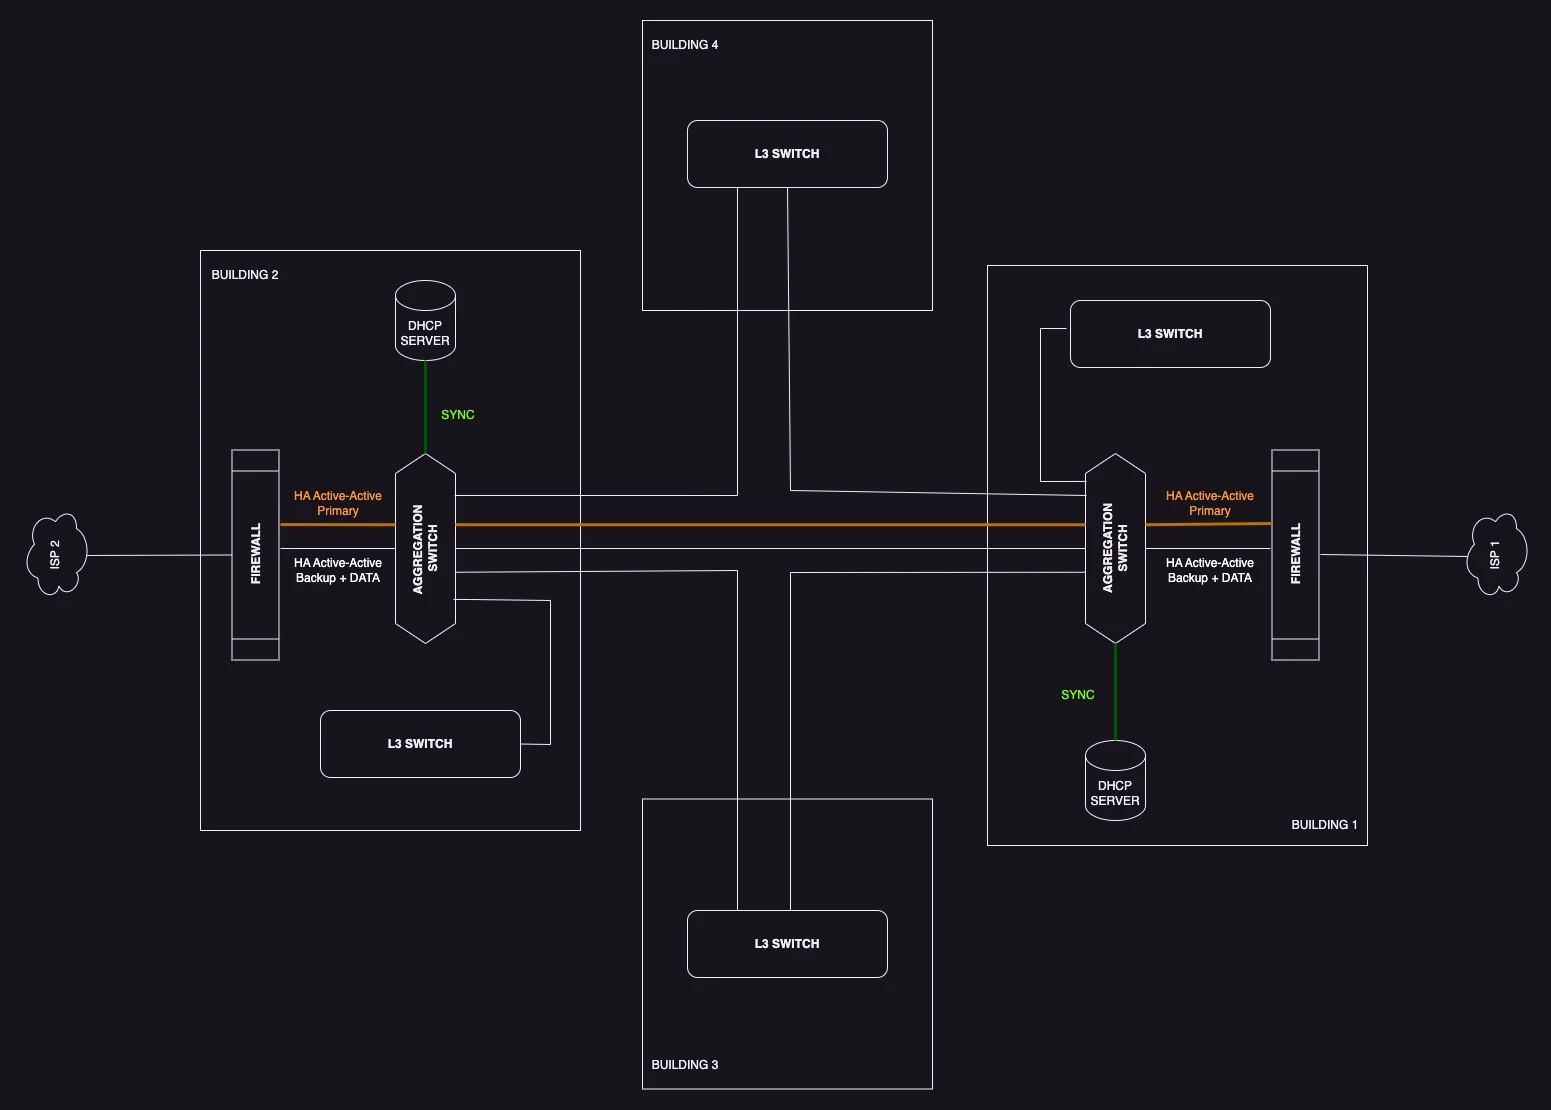
I want to provide internet connectivity for 4 adjacent buildings that can be connected together either by running fiber or over the air with antennas.

I was thinking of using two different ISP. One in each of the 2 main building selected.

The goal is to have building 1 serving building 3 and building 2 serving building 4 but in case of issue from one of the main building with an ISP connection, operation would continu provided by the other main building. (for example building 1 would serve building 4 in case of building 2 failure).

From my reading so far i try to implement an active active high availability scenario with policy based routing or i might be wrong ! should i got vrrp or ospf ? 

Can someone provide me guiding to achieve the best deployment possible in this type of scenario ? Thanks.

 

HA Active Active Deployment.jpg

7 replies

jintrah_FTNT
Staff
Staff
Aug 21, 2024 6:40 AM UTC

Hi,


In any mode HA, active-active or active-passive, the units must have identical setup. It is not advisable to keep ISP1 link connected to only device and ISP2 link connected to different device. Once you have identical setup made, then you may route traffic from one building through one ISP and fallback to second ISP if primary ISP failed and vice versa.


best regards,

Jin

didyfink
didyfinkAuthor
New Member
Aug 21, 2024 7:46 PM UTC

thanks for the reply ! 

so even in a distributed HA ? geographically separated firewall should have the same ISP link ? or keeping the same ISP do not matter ? also why can we not do active-active with pppoe ?

Staff
Aug 22, 2024 11:22 AM UTC

Hello,

It is also present in the documentation. Reference:
https://docs.fortinet.com/document/fortigate/7.6.0/administration-guide/357558/ha-active-active-cluster-setup
An A-A cluster supports interfaces in DHCP mode, but not interfaces in PPPoE mode. If an interface is in PPPoE mode, then the Active-Active option will not appear in the Mode selection.


Shashwati
Staff
Staff
Aug 30, 2024 8:54 PM UTC

Hello,


For Active -active you need the ISP link connection on both of your Firewall 

For multiple ISP link 

Please refer to the document 

https://docs.fortinet.com/document/fortigate/6.2.16/cookbook/23145/sd-wan-with-fgcp-ha

Toshi_Esumi
SuperUser
SuperUser
Aug 30, 2024 9:19 PM UTC

The reason is in a-a FGCP HA, every new session has to come though the primary unit, regardless where it's coming from, like ISP1, ISP2, and LAN side. Only after that some sessions can be delegated to the secondary units as depicted in the packet flow diagram below:

https://community.fortinet.com/t5/FortiGate/Technical-Tip-FortiGate-HA-A-A-cluster-3-way-TCP-handshake/ta-p/197467

Toshi

didyfink
didyfinkAuthor
New Member
Aug 31, 2024 1:34 AM UTC

so this type of scenario would have me more sens ?

HA Active Active Deployment V2.jpg

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT
