burakheyjobs
Visitor III
December 24, 2021
Solved

Fortigate Network Design

Hello everyone,

I have a design plan on my mind with one FortiGate 200F (or 100F) that will have the WAN from ISP Router. Then I will have 2  (can be 4 or more) FortiSwitch 248E. I am planning to buy these and make network infrastructure with. Our office has 300 employees, no VoIP phone (only Windows based VoIP). I don't want to chuck the firewall by using only Tier 2.
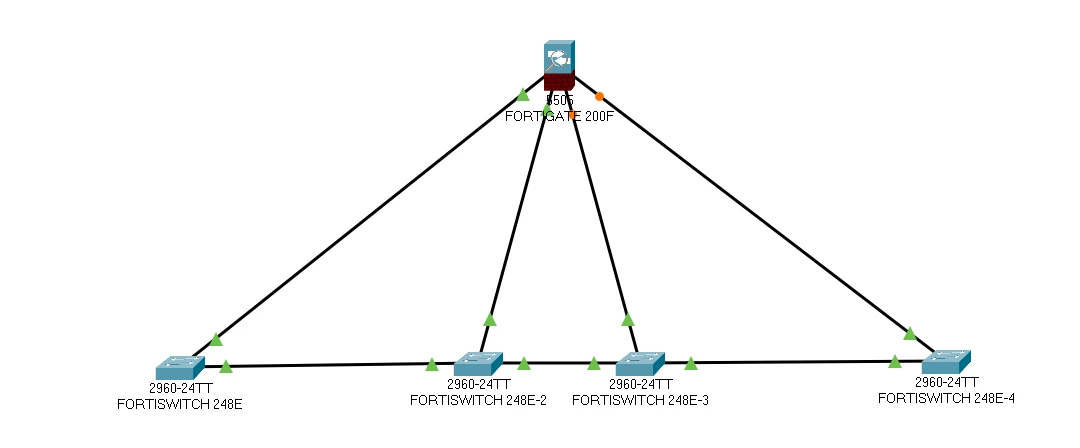
Fortigate will all the routing to internet and the clients \ APs will be connected to switches. Is it helpful to connect every switches to the fortigate's interfaces (nt1.png) or should I put two switches as Distribution LAyer between fortigate and access switches (other switches) (nt2.png)? n2.pngnt1.png
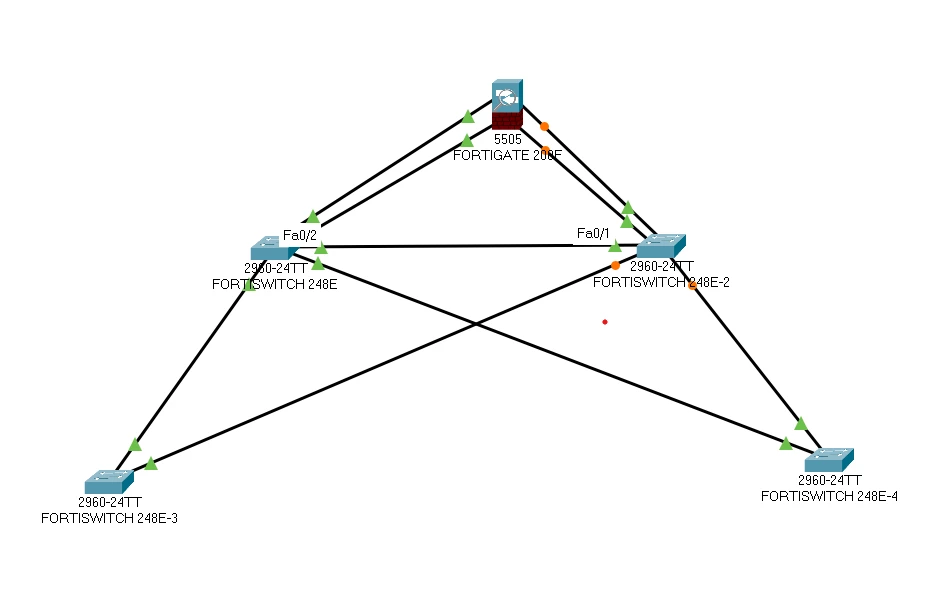


I tried to draw diagram on Cisco Packet Tracer just to draw. disregard the switch models 2960 :)

Every solution , suggestions will be much appreciated :)
Merry Christmas and stay nerdy

TheUsD
TheUsDAnswer
Visitor III
December 24, 2021

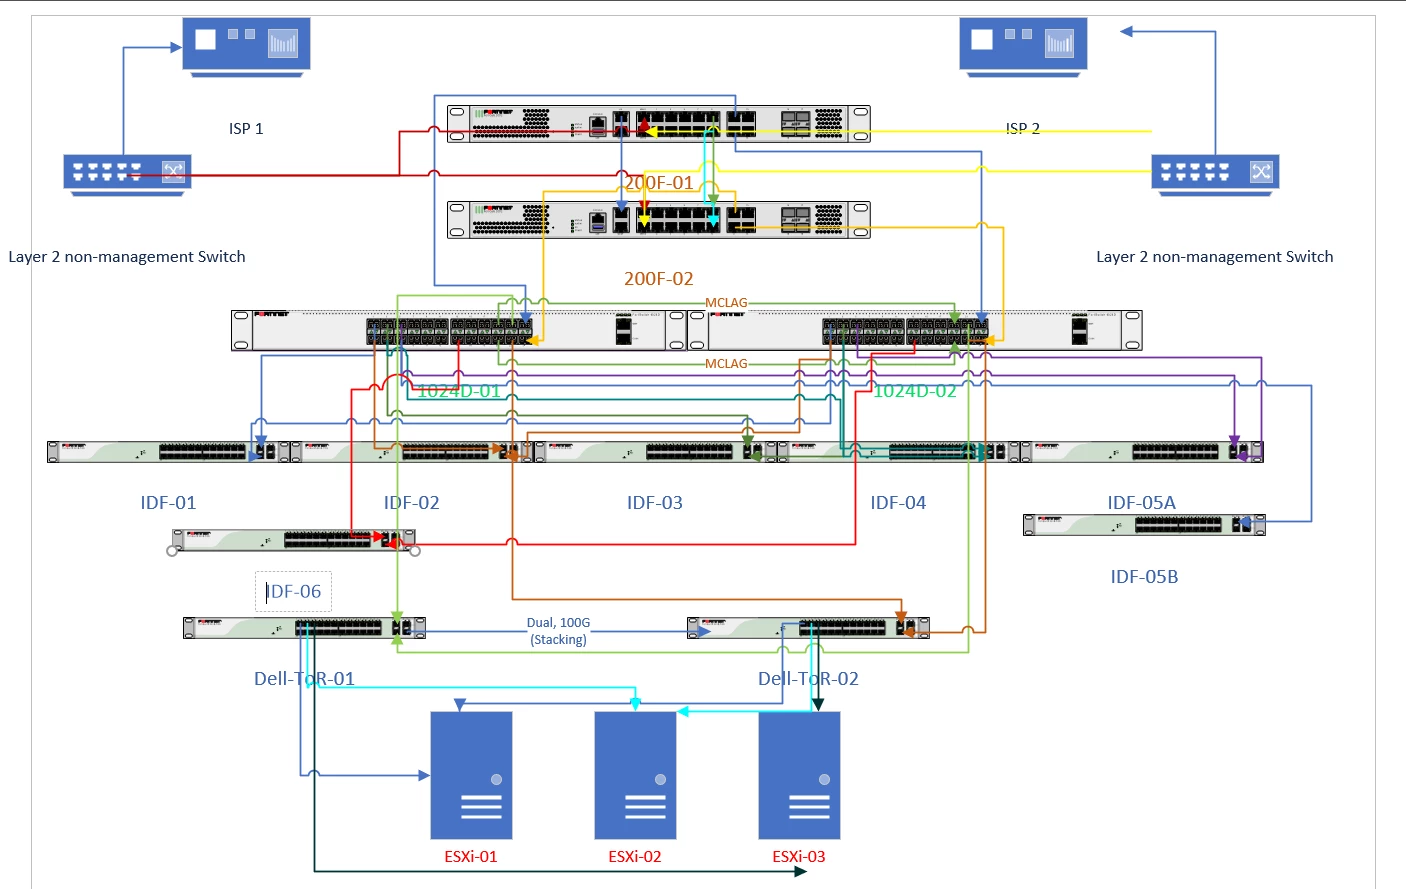
Here is a topology of one the companies I support. What I created was A-P HA Firewalls, redundancy of core switches and redundancy of uplinks for access switches. The only single point of failure is if a access switch at the IDF fails. This topology aligns very similar with your first diagram. 
In FortiWorld, you're looking to do is called MC-LAG and ICL (Inter Connection Link). The LLDP profile is called auto-isl (Inter Switch Link)

Use this link to help understand the lingo and configuration. Focus on the topic:
"Standalone FortiGate unit with dual-homed Fortiswitch access" 
Devices Managed by FortiOS | FortiSwitch 7.0.2 | Fortinet Documentation Library


Hope this helps.


TheUsD_0-1640383670657.png


2 replies

TheUsD
TheUsDAnswer
Visitor III
December 24, 2021

Here is a topology of one the companies I support. What I created was A-P HA Firewalls, redundancy of core switches and redundancy of uplinks for access switches. The only single point of failure is if a access switch at the IDF fails. This topology aligns very similar with your first diagram. 
In FortiWorld, you're looking to do is called MC-LAG and ICL (Inter Connection Link). The LLDP profile is called auto-isl (Inter Switch Link)

Use this link to help understand the lingo and configuration. Focus on the topic:
"Standalone FortiGate unit with dual-homed Fortiswitch access" 
Devices Managed by FortiOS | FortiSwitch 7.0.2 | Fortinet Documentation Library


Hope this helps.


TheUsD_0-1640383670657.png


burakheyjobs
Visitor III
December 25, 2021

Thank you so much for reply. That is really helpful :)

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT