
harsh_mittal
Explorer
May 23, 2025 5:20 PM UTC
Question

Fortigate Firewall 101F Interface config

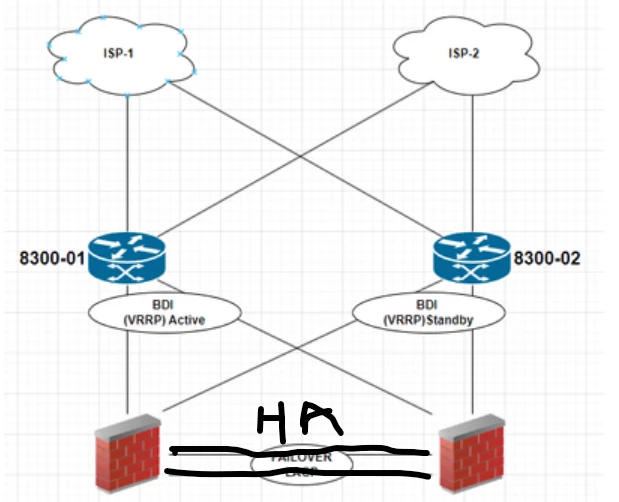
I have created the BDI interfaces on the Cisco SD-WAN routers with VRRP. Fortigate firewalls are working in active passive mode. We have connections to both routers from each firewall. Please suggest the config to follow here on FortiGate so that in case the link to SD-WAN router 1 goes down from FortiGate firewall 1, traffic should go out from SD-WAN router 2 from FortiGate firewall 1 link. Please suggest other options also 
 

dijix1990_0-1747971171768.png


2 replies

harsh_mittal
Explorer
May 26, 2025 3:24 AM UTC

Thanks for sharing the documentation.

In the snip, we connect to both routers from the active and passive firewall on the same VLAN. meaning, Physical interfaces on firewalls connecting to the router are in the same network. Is there any way, i can add fw ports in same vlan and so both ports become part of same network.


Translate
Risk and Resilience in the Age of AI. An OT Thought Leadership Summit for Houston's Critical Infrastructure Leaders. Date: Thursday, December 3, 2026. Time: 8:30 am - 1:30 pm (CT). Location: The Westin Houston, Memorial City | 945 Gessner Road, Houston, TX 77024
