

Solved
CheckPoint to FortiGate conversion
We are converting checkpoint configurations to fortigate (finally getting rid of it)
But I have seen the interface setting and here is something I am not used to it
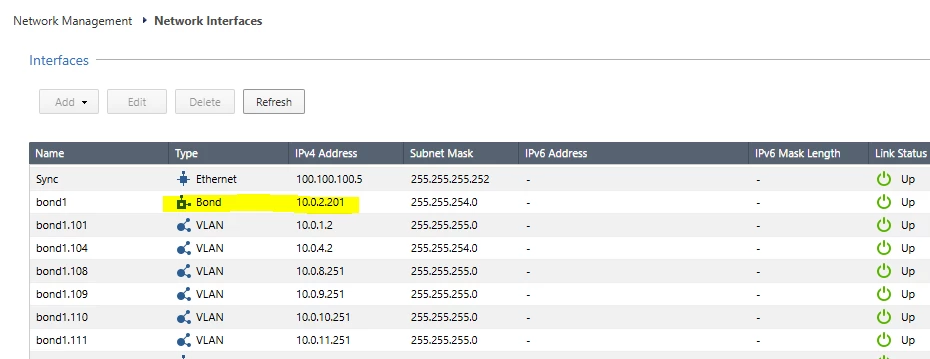
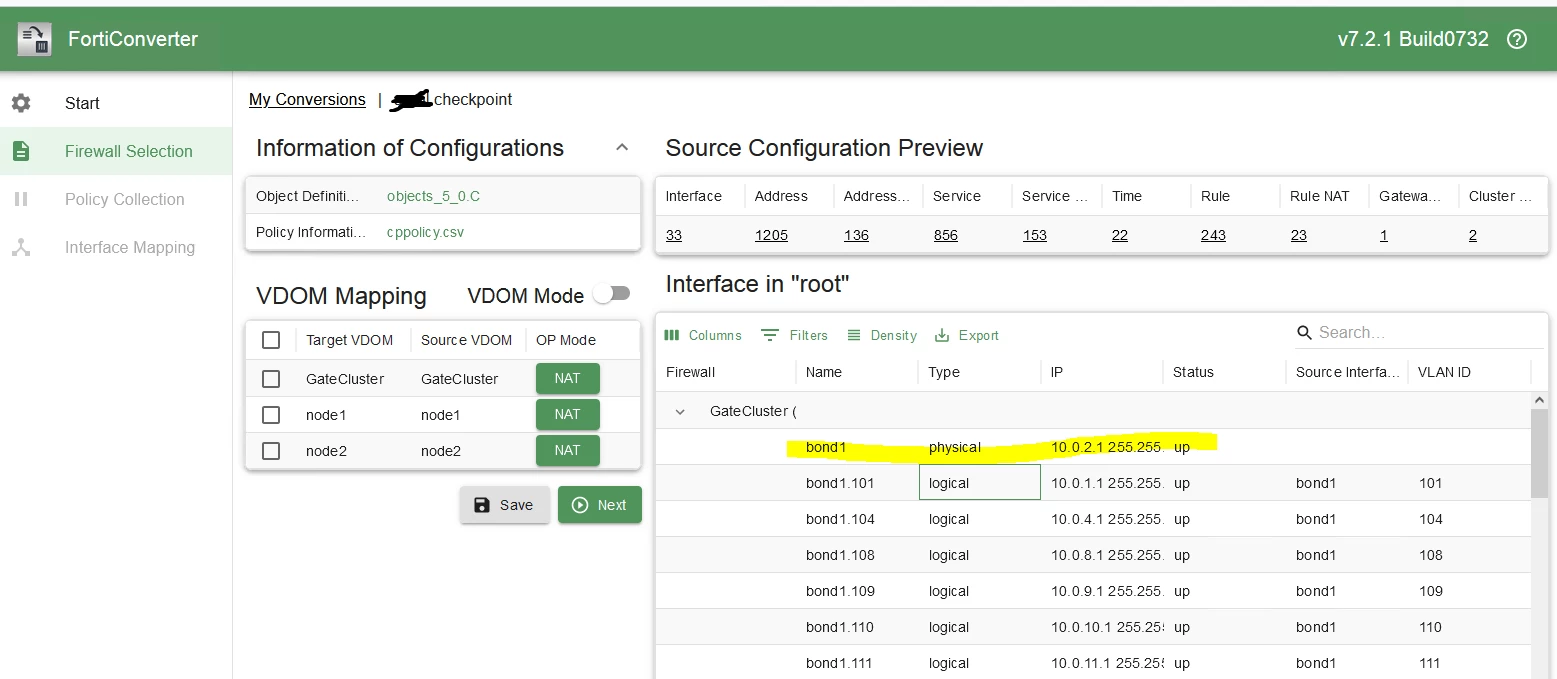
In Checkpoint the LAG interface itself (the physical) has a network without VLAN
the Forticonverter converter exactly the same settings. see screenshots bellow:
I am used to put all IP addresses and betworks to logical interfaces with VLANID
So my question is, will this work normally in fortigate? with VLAN ID 1 ? untagged ? can this interface (the physical) be assigned to policies later ?
Thanks


