
rbraha
Staff
Staff
May 26, 2026 8:10 AM UTC

Technical Tip: Comparing FSSO polling mode methods: NetAPI, Security Log, and WMI

Description

This article describes the differences between polling mode methods used in the collector agent.

Scope

FortiGate.

Solution

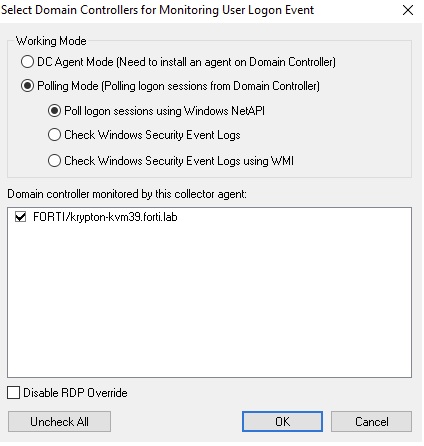
Fortinet Single Sign-On (FSSO) Polling Mode allows the Collector Agent to gather user login information without installing software on the Domain Controllers (DCs).

There are three primary methods available, each with different performance impacts and accuracy levels.

a202a05f.jpg


  1. Windows NetAPI.

This method utilizes the Microsoft NetSessionEnum API to query the DC for active sessions.

Mechanism: The Collector Agent uses the NetSessionEnum API to query the Domain Controller's active session table stored in volatile memory (RAM).

  • Polling Interval: Every 9 seconds.

  • Pros: The fastest and most lightweight method.

  • Cons: Higher risk of missing events if the server is under heavy load or if login events are extremely brief.


  1. Windows Security Event Logs (WinSec).

The Collector Agent reads the DC's security logs directly to identify specific authentication Event IDs.

  • Mechanism: Monitors Event IDs 672, 680, 4776, 4768, and 4769 (Logon/Kerberos). It also tracks IDs 528, 540, and 4624 (macOS) for resource access.

  • Polling Interval: Every 5 seconds.

  • Pros: It keeps a permanent record of every login by reading the official Windows security history for both modern (Kerberos) and older (NTLM) login types.

  • Cons: More resource-intensive than NetAPI as it parses log files.


  1. Windows Management Instrumentation (WMI).

  • Requirements: Requires opening Windows Firewall ports TCP 135 and 445 on the target machines.

  • Pros: WMI sends targeted queries for the desired Event IDs.

  • Cons: High overhead; slowest performance among the three options.


Note: WMI is also used for detecting workstation logoffs.


Recommended usage by environment.

  • Small/medium environments → WinSec.

  • Large/high-load DCs → NetAPI.

  • Environments requiring faster logoff detection → WinSec + workstation verify/WMI.


Common pitfalls.

  • Security log rollover is causing missed events.

  • WMI delays on slow workstations.

  • NetAPI is missing short-lived sessions.


Performance considerations.

  • WMI creates more load on the network and systems.

  • WinSec relies on Windows Security Event Logs being properly configured.

  • NetAPI depends on the current active sessions available in RAM.


Efficiency & recommendation ranking.

For the best balance of performance and accuracy, use the following hierarchy:

WinSec + Workstation WMI: The 'Best Standard' for accuracy, combining logon tracking with active logoff detection.

WinSec (Standard): Ideal for most environments needing reliable identity tracking without WMI overhead.

NetAPI: Best for very large, high-traffic environments where DC performance is the primary concern.


Note: Technical Tip: Windows event IDs used by FSSO in WinSec polling mode.


Related articles: 

Technical Tip: Comparison between DC-Agent mode and polling mode

Technical Tip: FortiGate FSSO Polling mode (Agentless) benefits and limitations

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT

