


Meru Technical Note: Tunnel Termination
Description
Scope
Solution
This article describes the Tunnel Termination Option in the Security Profile.
Scope
Controller 6.x, 7.x, 8.x.
Solution
Tunnel Termination is an option that can be set on the controller security profile with wpa2 with ccmp-aes RADIUS server authentication to terminate the outer tunnel at the controller; instead of the RAD server.
This option terminates the outer tunnel with certificate at the controller where 802.1x RAD IUS authentication will not use server cert; instead it will use controller certificate for authentication, even though the user credentials are available on the RAD server.
By Default, this option is set off. The option can be enabled in situations where you do not have a certificate on the RAD server and would prefer using the controller certification for RADIUS authentication with wpa2/ccmp-aes. Also, this option is available for two EAP types: PEAP and TTLS where both use server cert for authentication and you can set it according to according to the EAP type used on the supplicant.
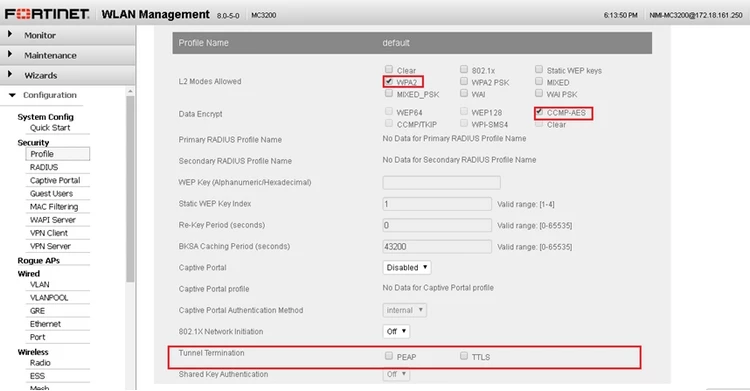
The following screen shot shows where we map controller certificate for Security applications. This means that the controller cert is used for RADIUS authentication; instead of actual RAD server cert; if tunnel termination is enabled.
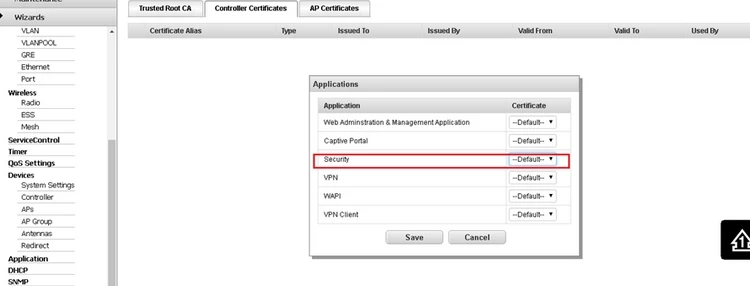
Certificate mapping is available on page: Configuration > Certificates > Controller Certificate tab where we click on the Applications button at the bottom to map the controller certificate for Security application.
This option terminates the outer tunnel with certificate at the controller where 802.1x RAD IUS authentication will not use server cert; instead it will use controller certificate for authentication, even though the user credentials are available on the RAD server.
By Default, this option is set off. The option can be enabled in situations where you do not have a certificate on the RAD server and would prefer using the controller certification for RADIUS authentication with wpa2/ccmp-aes. Also, this option is available for two EAP types: PEAP and TTLS where both use server cert for authentication and you can set it according to according to the EAP type used on the supplicant.
The following screen shot shows where we map controller certificate for Security applications. This means that the controller cert is used for RADIUS authentication; instead of actual RAD server cert; if tunnel termination is enabled.
Certificate mapping is available on page: Configuration > Certificates > Controller Certificate tab where we click on the Applications button at the bottom to map the controller certificate for Security application.
