


Technical Tip: Using a loopback interface as a local DNS server for SSL VPN
| Description | This article describes how to use a loopback interface as a local DNS server in an SSL VPN configuration. |
| Scope | FortiGate. |
| Solution | This configuration can be used when SSL VPN clients must use the DNS provided by the FortiGate. The DNS server service on the interface only works on the 1st ingress physical interface. To use FortiGate as the DNS server for SSL VPN clients, configure a loopback interface and use the loopback IP address as the DNS server for SSL VPN.
Configure the loopback interface.
config system interface
Configure the loopback interface as a DNS server.
config system dns-server
Configure the SSL VPN settings to assign the loopback IP address as the DNS server.
config vpn ssl settings
Create a firewall policy with the SSL VPN interface as the incoming interface and the loopback interface as the outgoing interface.
config firewall policy
To confirm that the DNS traffic is being processed by the newly created policy between ssl.root and loopback1, use the command below:
diagnose firewall iprope show 00100004 <policy-id>
Sample output:
diagnose firewall iprope show 00100004 1
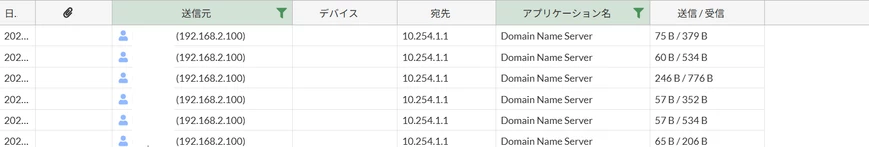
After the SSL VPN client connects, verify that the assigned DNS server is the loopback IP address and confirm that DNS traffic through the loopback interface works as expected.
 |

