


Technical Tip: User source detection for PKI based IPsec users
Description | This article describes the behavior of how the user source is detected and handled in PKI authentication when using IPsec VPN. |
Scope | FortiGate. |
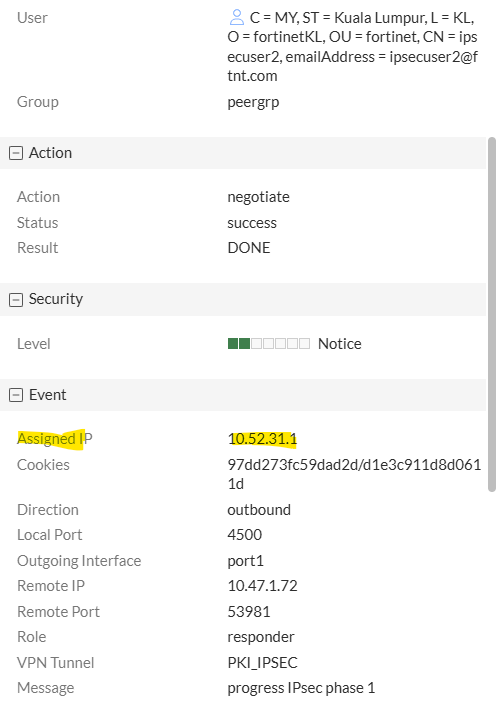
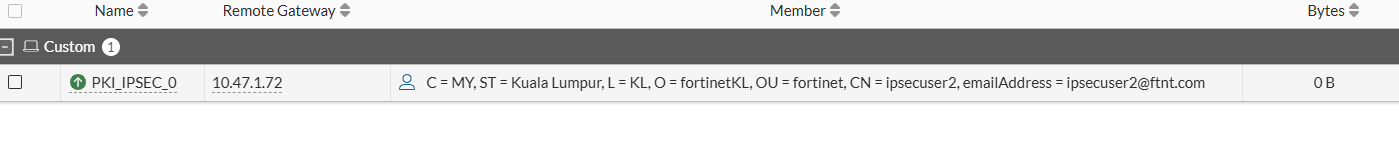
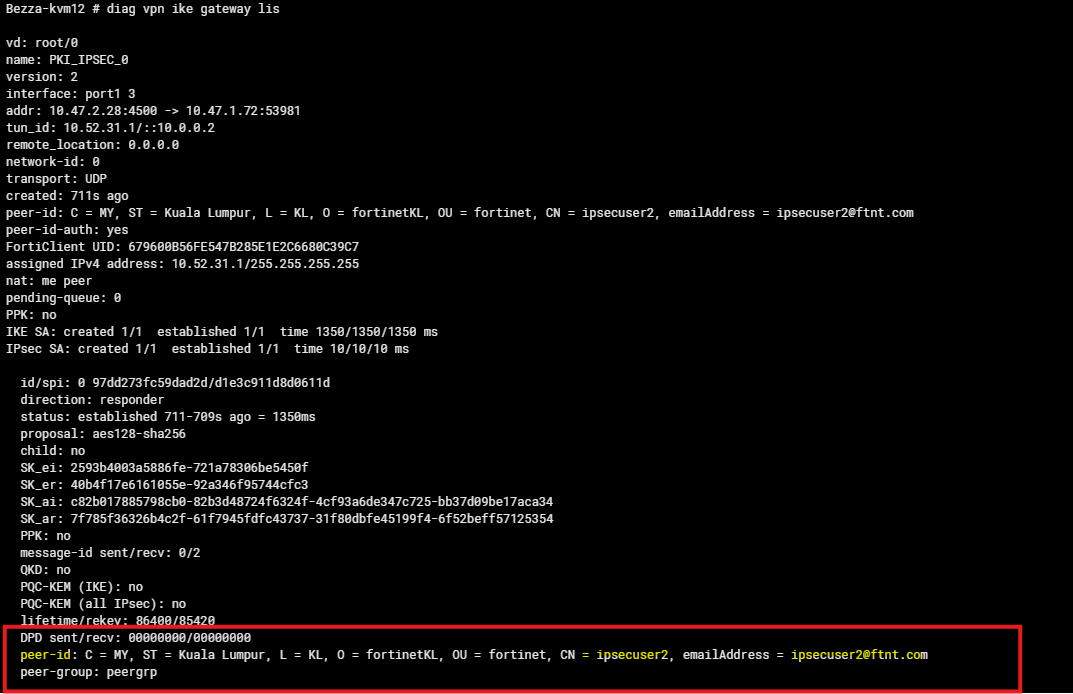
Solution | In SSL VPN, when a PKI user authenticates, the Forward traffic logs show the user source and the related certificate details, such as the 'cn', and this behavior is different in IPsec Vpn as explained below.
CN information: 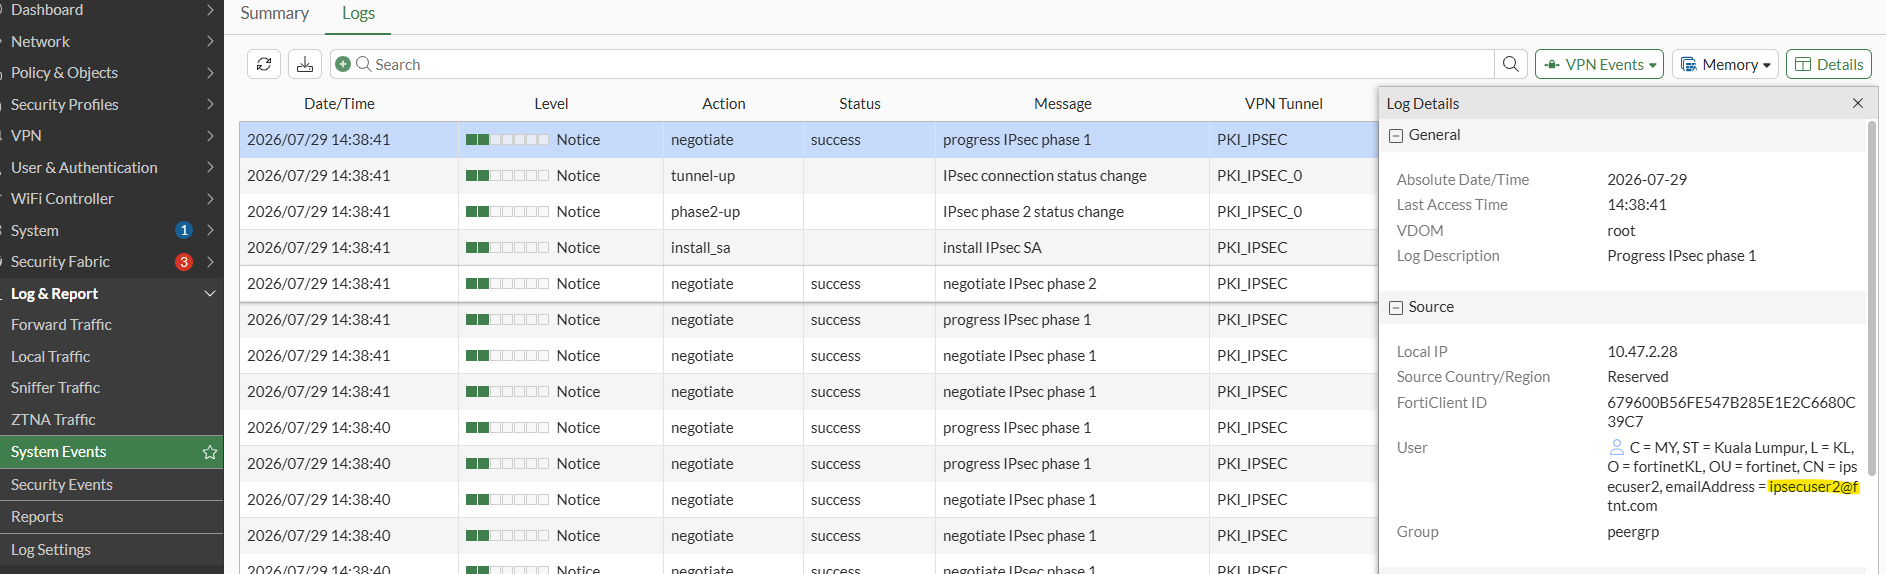
|

