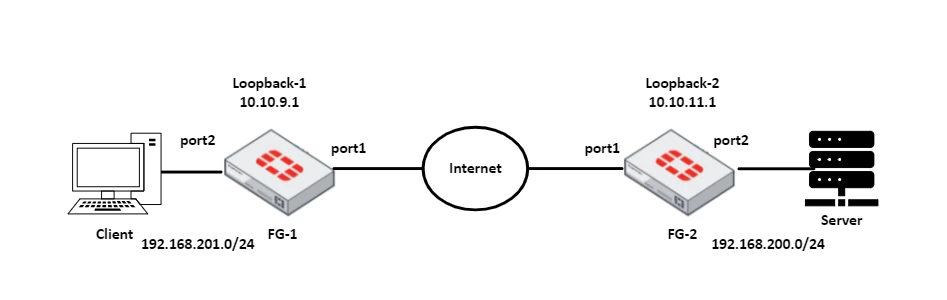
 FG-1 with loopback interface 10.10.9.1. FG-2 with loopback interface 10.10.11.1. The IPsec between both devices will be bound to the loopback interface. Port1 of every of the FortiGates is used for the internet connection. A previously established connectivity between both loopback interfaces must be guaranteed. (In this article, there is communication between 10.10.9.1 and 10.10.11.1 through the WAN network of port 1.) If this communication does not previously exist and port1 has public IPs in exchange for private addressing, the public IPs of both gateways must be associated on their respective public WAN interfaces (this scenario is explained at the end of this article).
Configuration: Firewall rules are needed on every FortiGate, allowing traffic to/from loopback/port1. Static route for the remote loopback IP on every FortiGate. Rules which allow the traffic to/from local/remote encryption domains. Static route for the remote encryption domain.
FG-1 Loopback interface: edit "loopback_FG1"
set vdom "root"
set ip 10.10.9.1 255.255.255.255
set allowaccess ping https http
set type loopback
set role lan
set snmp-index 16
set ip-managed-by-fortiipam disable
next
FG-1 static route for remote IPsec bound to loopback on FG-2: edit 1
set dst 10.10.11.1 255.255.255.255
set gateway 192.168.1.113
set device "port1"
next
FG-1 firewall rules allow the traffic from loopback loopback_FG1 to port1 and vice versa, only ESP (proto 50) and IKE (UDP 500) are allowed, if NAT-T is used then UDP 4500 needs to be added. edit 2
set name "Traffic_for_loopback_IPSEC"
set uuid f5a16342-7b79-51ef-6e44-02c65af6bb78
set srcintf "loopback_FG1" "port1"
set dstintf "loopback_FG1" "port1"
set action accept
set srcaddr "h-10.10.11.1-32" "h-10.10.9.1-32"
set dstaddr "h-10.10.9.1-32" "h-10.10.11.1-32"
set schedule "always"
set service "ESP" "IKE"
next
FG-1 IPsec phase-1 configuration : config vpn ipsec phase1-interface
edit "IPsec_to_FG2"
set interface "loopback_FG1"
set ike-version 2
set peertype any
set net-device disable
set proposal aes128-sha256
set remote-gw 10.10.11.1
set psksecret XXXX
next
end
FG-2 Loopback interface : edit "loopback_FG2"
set vdom "root"
set ip 10.10.11.1 255.255.255.255
set allowaccess ping https ssh snmp http fgfm ftm
set type loopback
set role lan
set snmp-index 16
set ip-managed-by-fortiipam disable
next
FG-2 static route for remote IPsec bound to loopback on FG-1: edit 1
set dst 10.10.9.1 255.255.255.255
set gateway 192.168.1.117
set device "port1"
next
10.10.9.1 is the Loopback interface in the FG-1
In this case, 192.168.1.117 is the port1 gateway associated with this FG-2.
FG-2 firewall rules allow the traffic from loopback loopback_FG2 to port1 and vice versa, only ESP (proto 50) and IKE (UDP 500) are allowed, if NAT-T is use,d then UDP 4500 needs to be added. edit 1
set name "Loopback_traffic"
set uuid f36aa980-7bce-51ef-b6ec-5fb2dd7121d3
set srcintf "loopback_FG2" "port1"
set dstintf "loopback_FG2" "port1"
set action accept
set srcaddr "h-10.10.9.1-32" "h-10.10.11.1-32"
set dstaddr "h-10.10.11.1-32" "h-10.10.9.1-32"
set schedule "always"
set service "ESP" "IKE"
next
FG-1 IPsec phase-1 configuration: config vpn ipsec phase1-interface
edit "IPsec_to_FG1"
set interface "loopback_FG2"
set ike-version 2
set peertype any
set net-device disable
set proposal aes128-sha256
set remote-gw 10.10.9.1
set psksecret ENC XXXX
next
end
Like every IPsec tunnel, there are also added Firewall rules from the local encryption domain towards the remote encryption domain and static routes. FG-1 Static route and firewall rule for the IPsec traffic: edit 2
set dst 192.168.200.0 255.255.255.0
set device "IPsec_to_FG2"
next
edit 3
set name "IPsec_rules"
set uuid ef3a8ed8-7b7a-51ef-3a3c-ef366951d68d
set srcintf "IPsec_to_FG2" "port2"
set dstintf "IPsec_to_FG2" "port2"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
next
FG-2 Static route and firewall rule for the IPsec traffic: edit 4
set dst 192.168.201.0 255.255.255.0
set device "IPsec_to_FG1"
next
edit 2
set name "IPsec_rule"
set uuid 72a34e28-7bcf-51ef-586b-9eecbe1fe9e8
set srcintf "port2" "IPsec_to_FG1"
set dstintf "IPsec_to_FG1" "port2"
set action accept
set srcaddr "h-192.168.200.0-24" "h-192.168.201.0-24"
set dstaddr "h-192.168.200.0-24" "h-192.168.201.0-24"
set schedule "always"
set service "ALL"
next
FG-1 phase-1/phase-2 status: vd: root/0
name: IPsec_to_FG2
version: 2
interface: 0
addr: 10.10.9.1:500 -> 10.10.11.1:500
tun_id: 10.10.11.1/::10.10.11.1
remote_location: 0.0.0.0
network-id: 0
transport: UDP
created: 51312s ago
peer-id: 10.10.11.1
peer-id-auth: no
pending-queue: 0
PPK: no
IKE SA: created 1/2 established 1/1 time 10/10/10 ms
IPsec SA: created 1/4 established 1/3 time 0/0/0 ms
id/spi: 66 ab6676e60cc712c8/95ca53fb7b92420d
direction: responder
status: established 51289-51289s ago = 10ms
proposal: aes128-sha256
child: no
SK_ei: d0551876481f6da6-a0ff7446a19964c2
SK_er: 254d54d4be17e084-a0b0aba1d3f710b5
SK_ai: f2a7df4e691d90c7-c5927297fadda91d-fd30a36b92b6ede4-d63b237f30193836
SK_ar: fafd6c0df23f6cdb-c3c674f6971dfad3-031950961ca2e44b-c7498d752ab6b3d3
PPK: no
message-id sent/recv: 3/6
QKD: no
lifetime/rekey: 86400/34840
DPD sent/recv: 00000000/00000000
peer-id: 10.10.11.1
name=IPsec_to_FG2 ver=2 serial=2 10.10.9.1:0->10.10.11.1:0 nexthop=192.168.1.113 tun_id=10.10.11.1 tun_id6=::10.10.11.1 status=up dst_mtu=1500 weight=1
bound_if=0 real_if=3 lgwy=static/1 tun=intf mode=auto/1 encap=none/552 options[0228]=npu frag-rfc run_state=0 role=primary accept_traffic=1 overlay_id=0
proxyid_num=1 child_num=0 refcnt=4 ilast=50234 olast=50234 ad=/0
stat: rxp=1000 txp=943 rxb=84000 txb=79212
dpd: mode=on-demand on=1 status=ok idle=20000ms retry=3 count=0 seqno=10
natt: mode=none draft=0 interval=0 remote_port=0
fec: egress=0 ingress=0
proxyid=IPsec_to_FG2 proto=0 sa=1 ref=2 serial=1 auto-negotiate
src: 0:0.0.0.0-255.255.255.255:0
dst: 0:0.0.0.0-255.255.255.255:0
SA: ref=3 options=38203 type=00 soft=0 mtu=1438 expire=34535/0B replaywin=2048
seqno=1 esn=0 replaywin_lastseq=00000000 qat=0 rekey=0 hash_search_len=1
life: type=01 bytes=0/0 timeout=42902/43200
dec: spi=6c2ea39b esp=aes key=16 a71f0120828076bf7de0255ab89056a5
ah=sha1 key=20 01f5764a2d5964102274ba633c4a1c7f47efbf6b
enc: spi=ea345265 esp=aes key=16 de9e1f65afb7122f1e7901a8569accd0
ah=sha1 key=20 0d5aa05d33a759dc4f98d5695c196864c9b9a849
dec:pkts/bytes=0/0, enc:pkts/bytes=0/0
npu_flag=00 npu_rgwy=10.10.11.1 npu_lgwy=10.10.9.1 npu_selid=0 dec_npuid=0 enc_npuid=0
FG-2 phase-1/phase-2 status: vd: root/0
name: IPsec_to_FG1
version: 2
interface: 0
addr: 10.10.11.1:500 -> 10.10.9.1:500
tun_id: 10.10.9.1/::10.10.9.1
remote_location: 0.0.0.0
network-id: 0
transport: UDP
created: 51370s ago
peer-id: 10.10.9.1
peer-id-auth: no
pending-queue: 0
PPK: no
IKE SA: created 1/1 established 1/1 time 10/10/10 ms
IPsec SA: created 1/3 established 1/3 time 0/3/10 ms
id/spi: 48 ab6676e60cc712c8/95ca53fb7b92420d
direction: initiator
status: established 51370-51370s ago = 10ms
proposal: aes128-sha256
child: no
SK_ei: d0551876481f6da6-a0ff7446a19964c2
SK_er: 254d54d4be17e084-a0b0aba1d3f710b5
SK_ai: f2a7df4e691d90c7-c5927297fadda91d-fd30a36b92b6ede4-d63b237f30193836
SK_ar: fafd6c0df23f6cdb-c3c674f6971dfad3-031950961ca2e44b-c7498d752ab6b3d3
PPK: no
message-id sent/recv: 6/3
QKD: no
lifetime/rekey: 86400/34729
DPD sent/recv: 00000003/00000003
peer-id: 10.10.9.1
name=IPsec_to_FG1 ver=2 serial=3 10.10.11.1:0->10.10.9.1:0 nexthop=192.168.1.117 tun_id=10.10.9.1 tun_id6=::10.10.9.1 status=up dst_mtu=1500 weight=1
bound_if=0 real_if=3 lgwy=static/1 tun=intf mode=auto/1 encap=none/552 options[0228]=npu frag-rfc run_state=0 role=primary accept_traffic=1 overlay_id=0
proxyid_num=1 child_num=0 refcnt=4 ilast=50347 olast=50347 ad=/0
stat: rxp=943 txp=1000 rxb=79212 txb=84000
dpd: mode=on-demand on=1 status=ok idle=20000ms retry=3 count=0 seqno=3
natt: mode=none draft=0 interval=0 remote_port=0
fec: egress=0 ingress=0
proxyid=IPsec_to_FG1 proto=0 sa=1 ref=2 serial=2 auto-negotiate
src: 0:0.0.0.0-255.255.255.255:0
dst: 0:0.0.0.0-255.255.255.255:0
SA: ref=3 options=38203 type=00 soft=0 mtu=1438 expire=34452/0B replaywin=2048
seqno=1 esn=0 replaywin_lastseq=00000000 qat=0 rekey=0 hash_search_len=1
life: type=01 bytes=0/0 timeout=42932/43200
dec: spi=ea345265 esp=aes key=16 de9e1f65afb7122f1e7901a8569accd0
ah=sha1 key=20 0d5aa05d33a759dc4f98d5695c196864c9b9a849
enc: spi=6c2ea39b esp=aes key=16 a71f0120828076bf7de0255ab89056a5
ah=sha1 key=20 01f5764a2d5964102274ba633c4a1c7f47efbf6b
dec:pkts/bytes=0/0, enc:pkts/bytes=0/0
npu_flag=00 npu_rgwy=10.10.9.1 npu_lgwy=10.10.11.1 npu_selid=3 dec_npuid=0 enc_npuid=0
If communication is not established between the private Loopback interface addresses, it is necessary to associate the WAN public addresses as follows:
FG-1 IPsec phase-1, phase-2 and static route alternative configuration:
config vpn ipsec phase1-interface
    edit "IPsec_to_FG2"
        set interface "port1"
        set ike-version 2
        set peertype any
        set net-device disable
        set proposal aes128-sha256 aes256-sha256
        set dpd on-idle
        set remote-gw 18.74.X.X
        set psksecret ENC XXXXXXXXXXXX
    next
end

config vpn ipsec phase2-interface
    edit "IPsec_to_FG2"
        set phase1name "IPsec_to_FG2"
        set proposal aes128-sha1 aes256-sha1
        set src-subnet 10.10.9.1 255.255.255.255
        set dst-subnet 10.10.11.1 255.255.255.255
    next

end
In the above:
config router static
    edit 2
        set dst 10.10.11.1 255.255.255.255 <- Remote Loopback interface of FG-2.
        set device "IPsec_to_FG2"
    next
end
FG-2 IPsec phase-1, phase-2 and static route alternative configuration:
config vpn ipsec phase2-interface
    edit "IPsec_to_FG1"
        set phase1name "IPsec_to_FG1"
        set proposal aes128-sha1 aes256-sha1
        set src-subnet 10.10.11.1 255.255.255.255 <- Local Loopback interface of FG-2.
        set dst-subnet 10.10.9.1 255.255.255.255 <- Remote Loopback interface of FG-1.
    next
end


config router static
    edit 4
        set dst 10.10.9.1 255.255.255.255 <- Remote Loopback interface of FG-1.
        set device "IPsec_to_FG1"
    next
end
Limitation: The scenario 'IPsec tunnel terminated behind a VIP (DNAT) with loopback' is not supported.
Valid workarounds: Use two VDOMs: One VDOM performs the DNAT (VIP for UDP 500/4500 on the WAN), the other VDOM terminates the IPsec tunnel (e.g., on a loopback interface), connected via an inter-vdom link. Configure the public IP as a secondary IP on the WAN interface and bind the phase1 to it (local-gw). Use a separate NAT device in front of the FortiGate.
Related article:
Technical Tip: Best practice when IPSec VPN is bound to loopback interface | 


