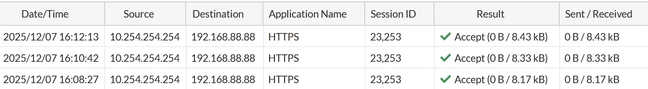
Technical Tip: FortiGate showing 0 sent packets/bytes for HTTPS Virtual Server
| Description | This article describes the issue of FortiGate showing 0 Sent Packets/Bytes for HTTPS Virtual Server in the traffic logs. |
| Scope | FortiGate. |
| Solution | When a Virtual Server of type 'HTTPS' is used, it can be observed that traffic logs in FortiGate or in FortiAnalyzer show 0 Sent Packets/Bytes for the Virtual Server IP. However, for the Virtual Server of Type 'SSL', the traffic logs show both Send/Receive bytes normally.
This behavior is by design and aligns with how HTTP/2 multiplexing is handled by FortiGate.
HTTPS virtual servers parse HTTP traffic (including HTTP/2), so the client port may not be reused, causing the counters to show 0 bytes in the sent direction. SSL virtual servers handle only the TCP/SSL layer without parsing HTTP, so the client port is reused, and the counters display normally.
To verify real traffic is flowing:
|