



Technical Tip: File Filter on WebFilter profile
Description
This article explains how to block file patterns on the Webfilter profile for inbound/outbound traffic.
Scope
FortiGate.
Solution
File Filter allows the Web Filter profile to block files passing through a FortiGate based on file type.
HTTP and FTP File Filtering is configurable in the Web Filter profile.
File Filtering in Web Filter profile is based on file type (file's meta data) only, and not on file size or file content.
Configure a DLP sensor to block files based on size or content, such as SSN numbers, credit card numbers, or regexp.
File filtering only works on proxy mode policies.
Configure the webfilter and enable the File Filter and select the file types are per the requirement and choose the correct protocol on which it is require to block, for which direction.
In the following example, three file filters are used in the Web Filter profile:
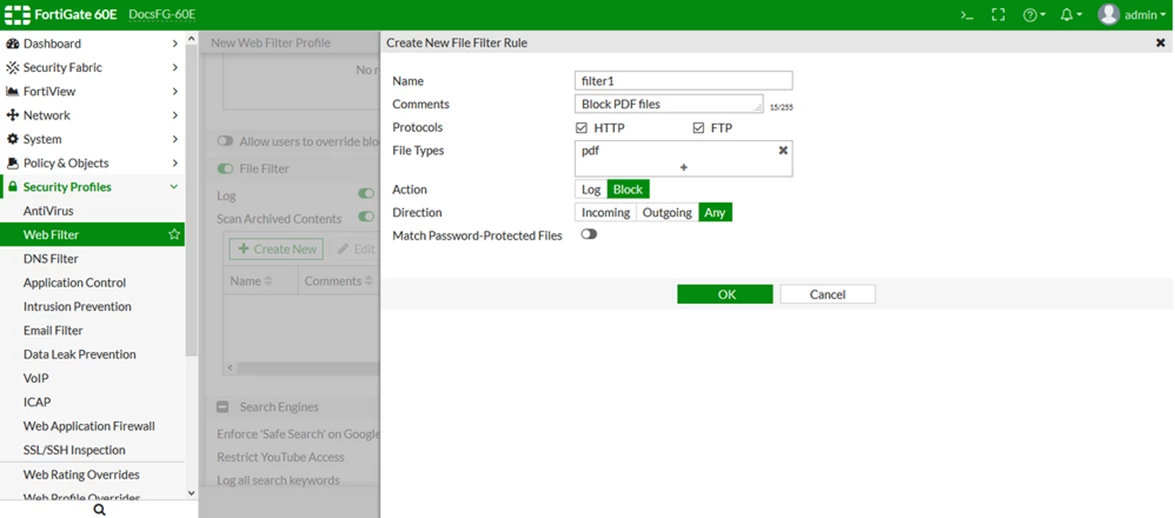
- Block PDFs from entering or leaving the network (filter1).
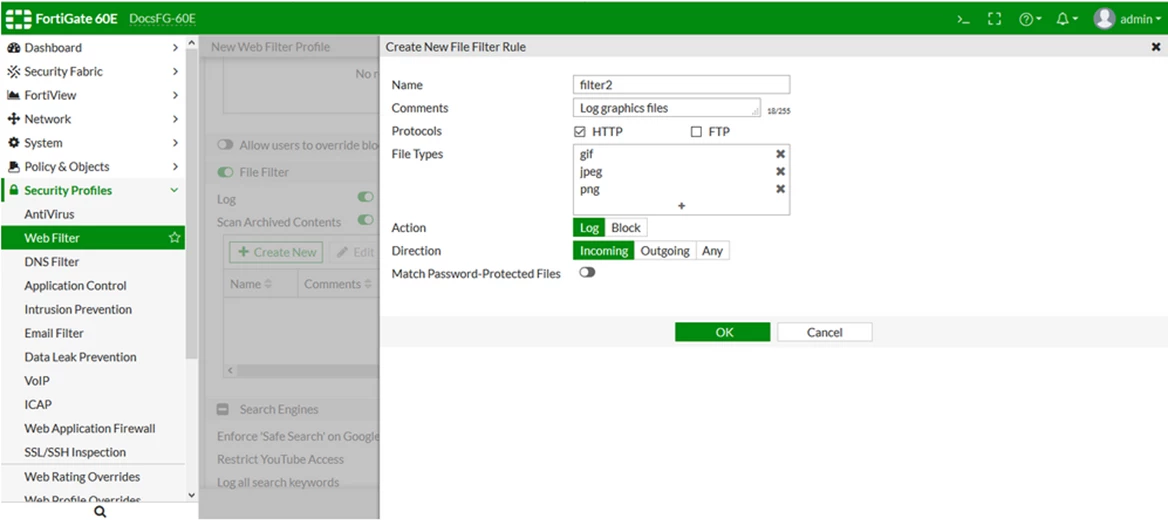
- Log the download of some graphics file-types via HTTP (filter2).
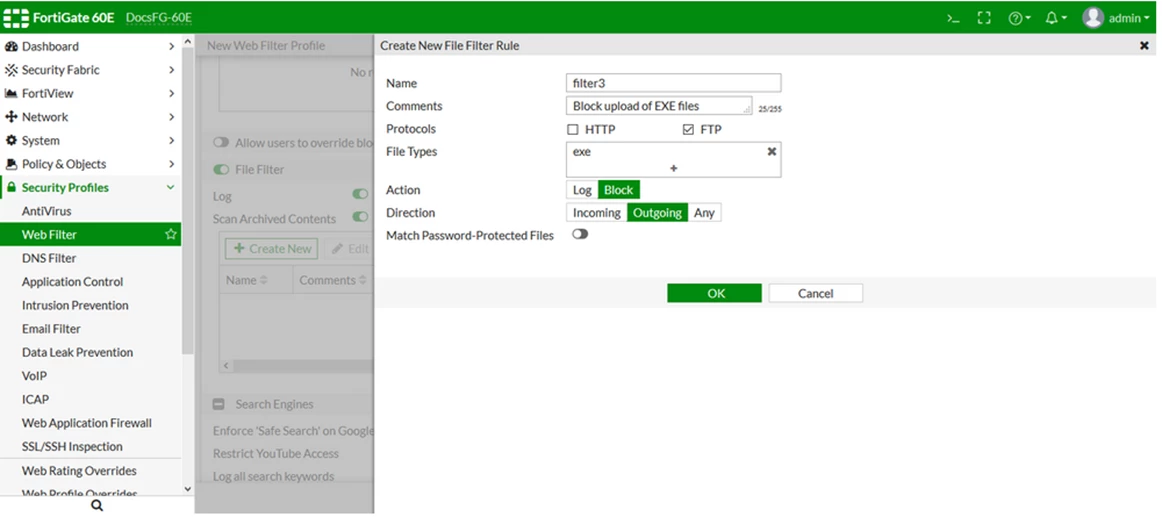
- Block EXE files from leaving to the network over FTP (filter3).
To configure a file-type-based web filter in the CLI:
config webfilter profile
edit "webfilter-file-filter"
config file-filter
set status enable
set log enable
set scan-archive-contents enable
config entries
edit "filter1"
set comment "Block PDF files"
set protocol http ftp
set action block
set direction any
set encryption any
set file-type "pdf"
next
edit "filter2"
set comment "Log graphics files"
set protocol http
set action log
set direction incoming
set encryption any
set file-type "jpeg" "png" "gif"
next
edit "filter3"
set comment "Block upload of EXE files"
set protocol ftp
set action block
set direction outgoing
set encryption any
set file-type "exe"
next
end
end
next
end
After configuring file filters in the Web Filter profile, apply it to a firewall policy using the following command:
config firewall policy
edit 1
set name "client-to-internet"
set srcintf "dmz"
set dstintf "wan1"
set srcaddr "all"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set utm-status enable
set utm-inspection-mode proxy
set logtraffic all
set webfilter profile "webfilter-filefilter"
set profile-protocol-options "protocol"
set ssl-ssh-profile "protocols"
set nat enable
next
end
To configure a file-type-based web filter in the GUI:
- Go to Security Profiles -> Web Filter
- Select 'Create New' or select an existing profile and select 'Edit'.
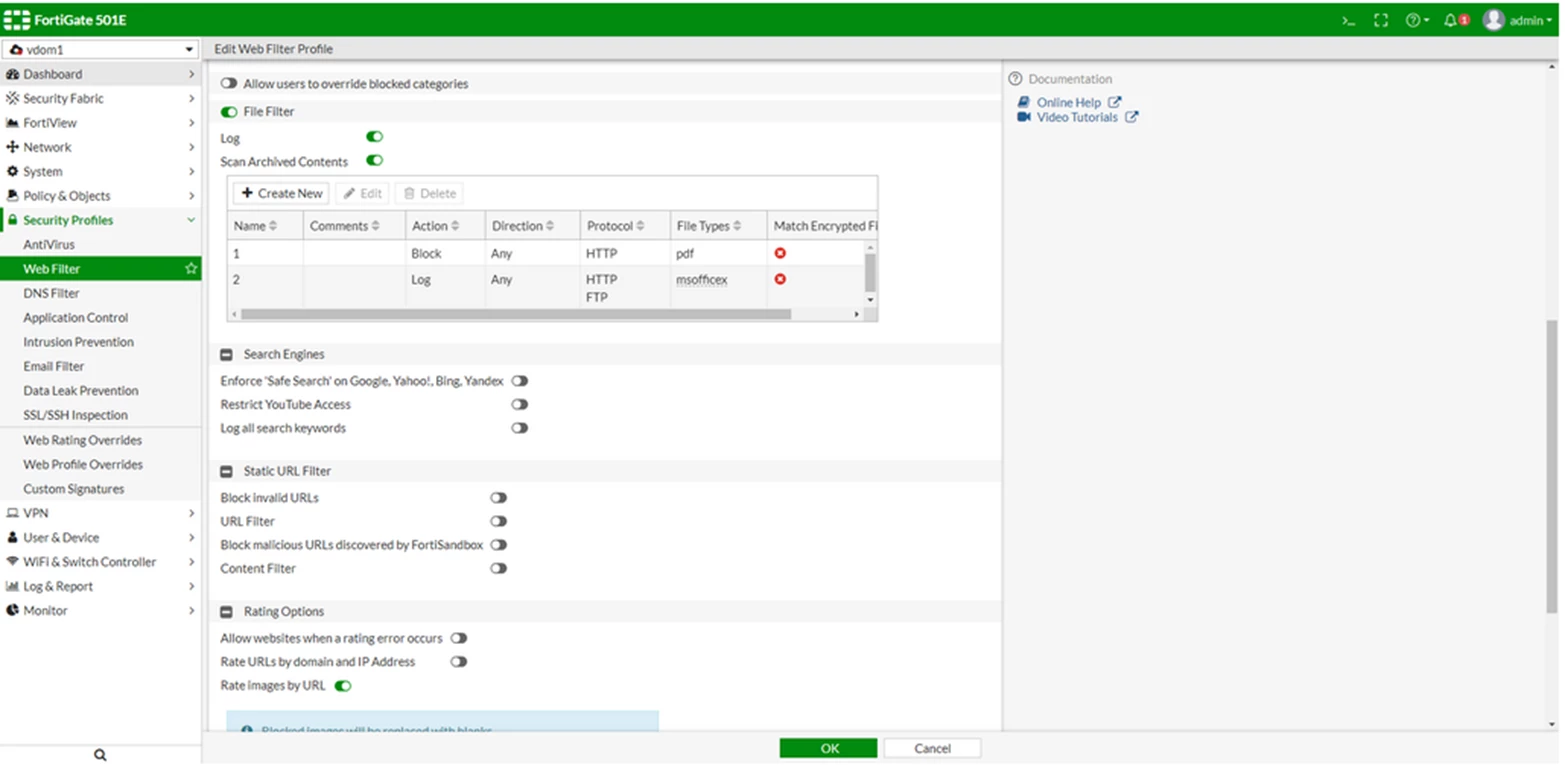
- Enable File Filter.
- Enable Log and Scan Archived Contents.
- In the File Filter table, click Create New.
- Configure the filters:
filter1 blocks PDFs from entering or leaving the network.
Add the new web filter profile to a firewall policy.
Log examples.
File filter block action:
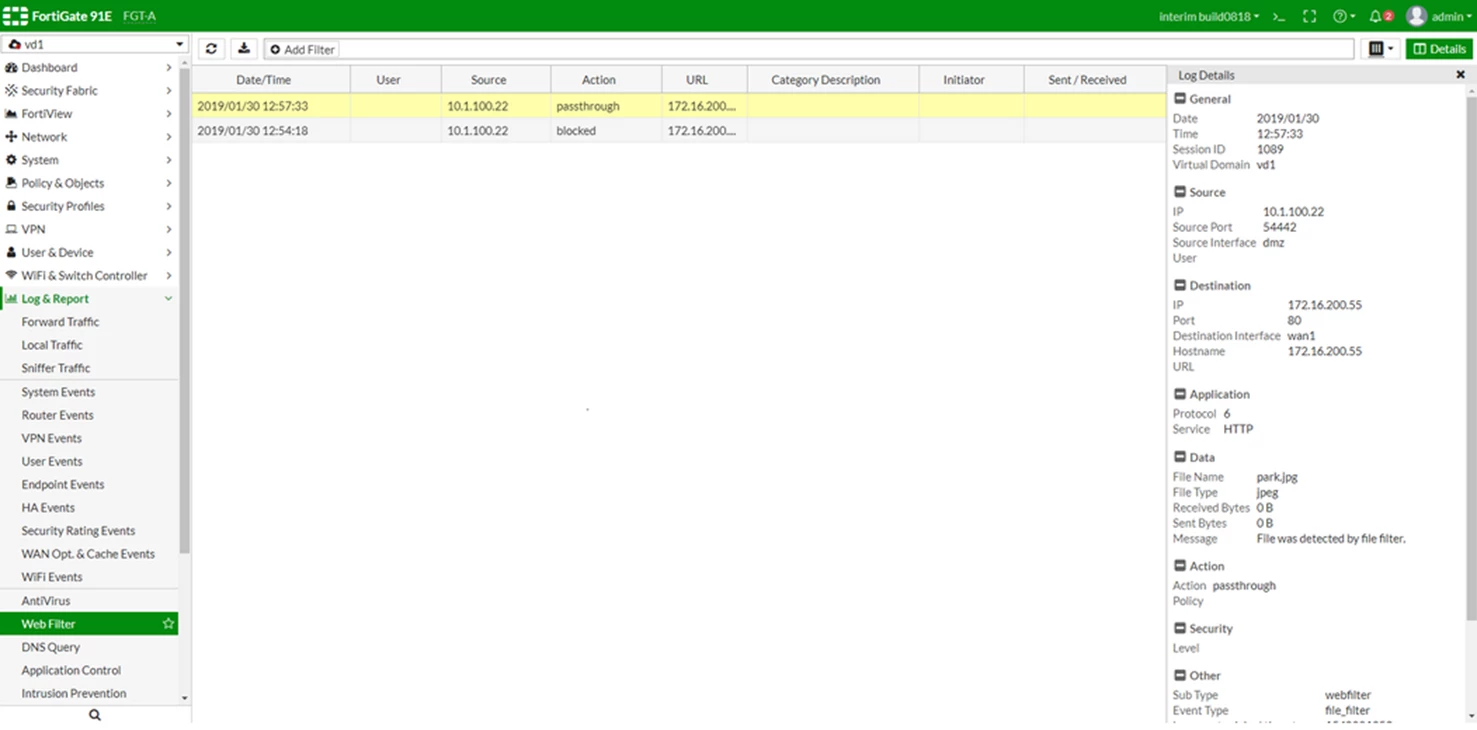
File filter log action:
2: date=2019-03-19 time=10:48:23 logid="0346012672" type="utm" subtype="webfilter" eventtype="file_filter" level="notice" vd="vd1" eventtime=1548442102 policyid=1 sessionid=521 srcip=10.1.100.22 srcport=52894 srcintf="dmz" srcintfrole="undefined" dstip=172.16.200.55 dstport=80 dstintf="wan1" dstintfrole="undefined" proto=6 service="HTTP" hostname="172.16.200.55" profile="webfilter-filefilter" action="passthrough" reqtype="direct" url="/app_data/park.jpg" sentbyte=0 rcvdbyte=0 direction="incoming" filename="park.jpg" filtername="filter2" filetype="jpeg" msg="File was detected by file filter."In the GUI:
In newer version 6.4.1 and above, the File Filter profile has been moved to its own profile:
