| Solution | In general, a firewall policy and correct route is required for FortiGate to forward the traffic accordingly. When a VDOM is disabled, the FortiGate firewall will not perform firewall policy lookup for traffic that is reaching the FortiGate on that VDOM. Example setup: 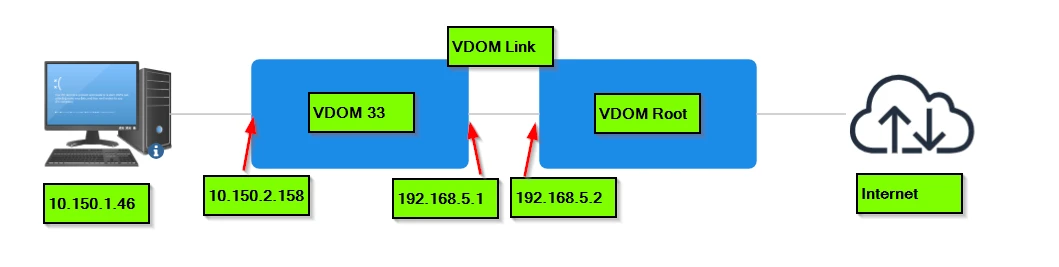
- When VDOM 33 is enabled, it is possible to ping from 10.150.1.46 to 8.8.8.8. The following is the debug flow output collected in VDOM 33 in a normal working scenario:
id=20085 trace_id=1923 func=print_pkt_detail line=5844 msg="vd-VDOM33:0 received a packet(proto=1, 10.150.1.46:1->8.8.8.8:2048) tun_id=0.0.0.0 from port6. type=8, code=0, id=1, seq=11."
id=20085 trace_id=1923 func=init_ip_session_common line=6023 msg="allocate a new session-011684c4, tun_id=0.0.0.0"
id=20085 trace_id=1923 func=vf_ip_route_input_common line=2605 msg="find a route: flag=04000000 gw-8.8.8.8 via 33Root1"
id=20085 trace_id=1923 func=fw_forward_handler line=881 msg="Allowed by Policy-1:"
id=20085 trace_id=1924 func=print_pkt_detail line=5844 msg="vd-root:0 received a packet(proto=1, 10.150.1.46:1->8.8.8.8:2048) tun_id=0.0.0.0 from 33Root0. type=8, code=0, id=1, seq=11."
id=20085 trace_id=1924 func=init_ip_session_common line=6023 msg="allocate a new session-011684c5, tun_id=0.0.0.0"
id=20085 trace_id=1924 func=vf_ip_route_input_common line=2605 msg="find a route: flag=00000000 gw-10.47.15.254 via port1"
id=20085 trace_id=1924 func=get_new_addr line=1221 msg="find SNAT: IP-10.47.2.158(from IPPOOL), port-60417"
id=20085 trace_id=1924 func=fw_forward_handler line=881 msg="Allowed by Policy-2: SNAT"
id=20085 trace_id=1924 func=__ip_session_run_tuple line=3470 msg="SNAT 10.150.1.46->10.47.2.158:60417" - When VDOM 33 is disabled, the computer is not able to ping 8.8.8.8. Debug flow output shows that VDOM 33 does not proceed to match any firewall policy after route lookup, and there is no error message displaying further information:
id=20085 trace_id=1935 func=print_pkt_detail line=5844 msg="vd-VDOM33:0 received a packet(proto=1, 10.150.1.46:1->8.8.8.8:2048) tun_id=0.0.0.0 from port6. type=8, code=0, id=1, seq=19."
id=20085 trace_id=1935 func=init_ip_session_common line=6023 msg="allocate a new session-01168bda, tun_id=0.0.0.0"
id=20085 trace_id=1935 func=vf_ip_route_input_common line=2605 msg="find a route: flag=04000000 gw-8.8.8.8 via 33Root1" - If VDOM 33 performs a ping check to the internet, the ping check works as expected (local-out traffic from VDOM33):
id=20085 trace_id=1939 func=print_pkt_detail line=5844 msg="vd-VDOM33:0 received a packet(proto=1, 192.168.5.2:1024->8.8.8.8:2048) tun_id=0.0.0.0 from local. type=8, code=0, id=1024, seq=0."
id=20085 trace_id=1939 func=init_ip_session_common line=6023 msg="allocate a new session-011693d0, tun_id=0.0.0.0"
id=20085 trace_id=1940 func=print_pkt_detail line=5844 msg="vd-root:0 received a packet(proto=1, 192.168.5.2:1024->8.8.8.8:2048) tun_id=0.0.0.0 from 33Root0. type=8, code=0, id=1024, seq=0."
id=20085 trace_id=1940 func=init_ip_session_common line=6023 msg="allocate a new session-011693d1, tun_id=0.0.0.0"
id=20085 trace_id=1940 func=vf_ip_route_input_common line=2605 msg="find a route: flag=04000000 gw-10.47.15.254 via port1"
id=20085 trace_id=1940 func=get_new_addr line=1221 msg="find SNAT: IP-10.47.2.158(from IPPOOL), port-61440"
id=20085 trace_id=1940 func=fw_forward_handler line=881 msg="Allowed by Policy-2: SNAT" - In summary, if the computer is unable to reach the internet through VDOM, all of the configuration files (VDOM link, firewall policy, static route etc.) are configured correctly, and the debug flow does not show any error message: check whether the VDOM is enabled under system settings.
Lotus-kvm24# config vdom Lotus-kvm24# edit VDOM33 Lotus-kvm24 (VDOM33) # show sys settings
config system settings set status disable <-----
end Note: The same information can also be obtained directly from Global VDOM, where all VDOMs are listed. This view simplifies configuration comparisons between VDOMs, including their status settings. FGT # config global
FGT (global) # diagnose system vdom list
system fib version=100
list virtual firewall info:
[...]
name=Test1/Test1 index=3 enabled fib_ver=10 rpdb_ver=0 use=269 rt_num=0 asym_rt=0 sip_helper=0, sip_nat_trace=1, mc_fwd=0, mc_ttl_nc=0, tpmc_sk_pl=0
[...]
name=Test2/Test2 index=4 disabled fib_ver=11 rpdb_ver=0 use=269 rt_num=0 asym_rt=0 sip_helper=0, sip_nat_trace=1, mc_fwd=0, mc_ttl_nc=0, tpmc_sk_pl=0
[...]
name=Test3/Test3 index=5 enabled fib_ver=10 rpdb_ver=0 use=269 rt_num=0 asym_rt=0 sip_helper=0, sip_nat_trace=1, mc_fwd=0, mc_ttl_nc=0, tpmc_sk_pl=0
[...] |



