


Technical Tip: Creating a static route for Predefined Internet Services (ISDB)
Description
This article describes how to add a static route for predefined internet services (ISDB) available in FortiGate.
Scope
FortiGate.
Solution
Important note: Consider these factors while testing the static routes:
Ensure that the service or protocol being tested is already included in the corresponding ISDB entry.
ISDB matching is based on a 3-tuple: IP address, protocol, and port. Therefore, the traffic used for testing must match the criteria defined in the ISDB entry.
This article includes instructions to route traffic via an IPsec tunnel as well.
For example, if the Google DNS ISDB object is selected, testing it using ICMP will not work if ICMP is not included in the ISDB entry. The test must use the appropriate protocol and port defined for the service.
From the GUI:
Go to Network -> Static Routes.
Select 'Create New'.
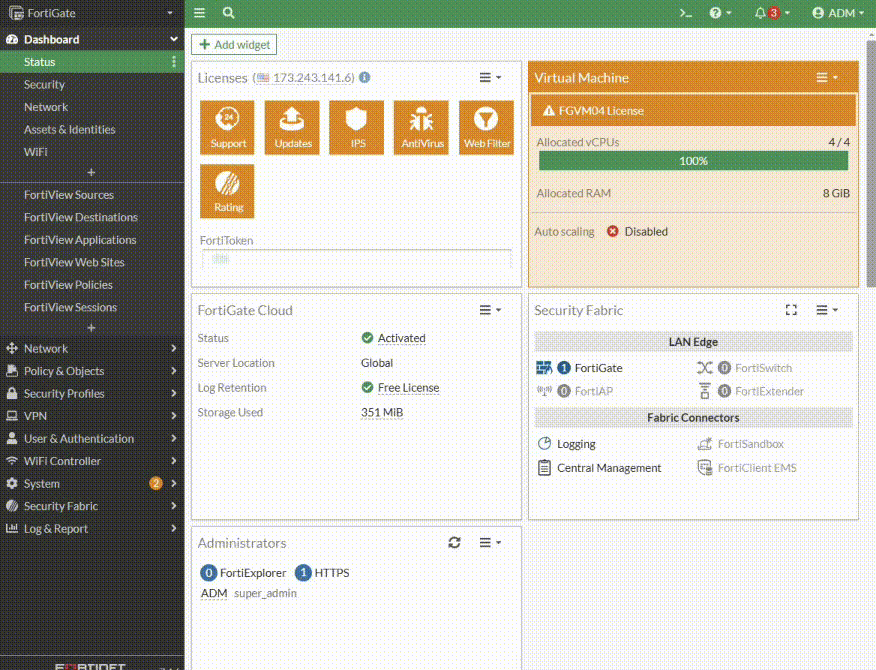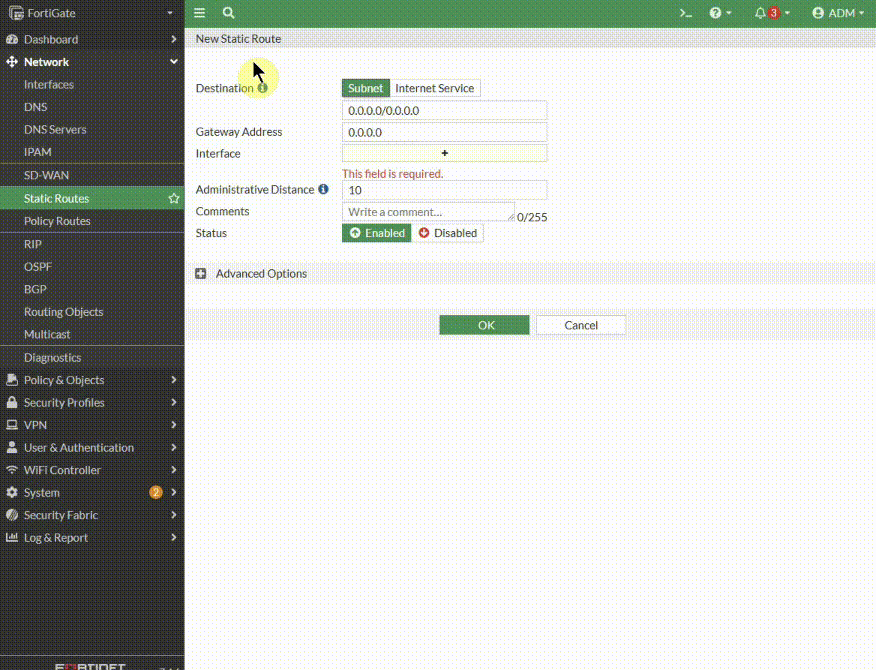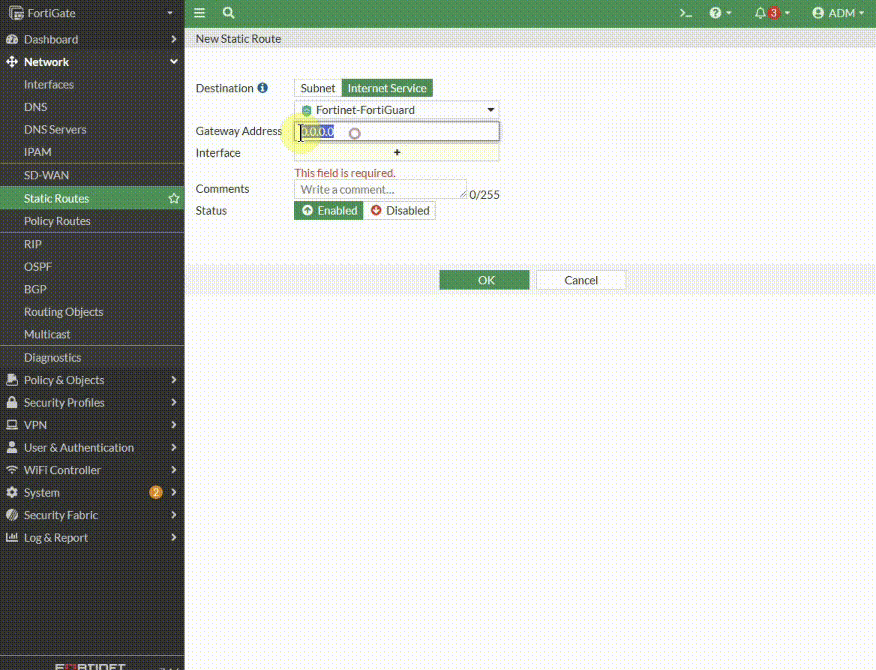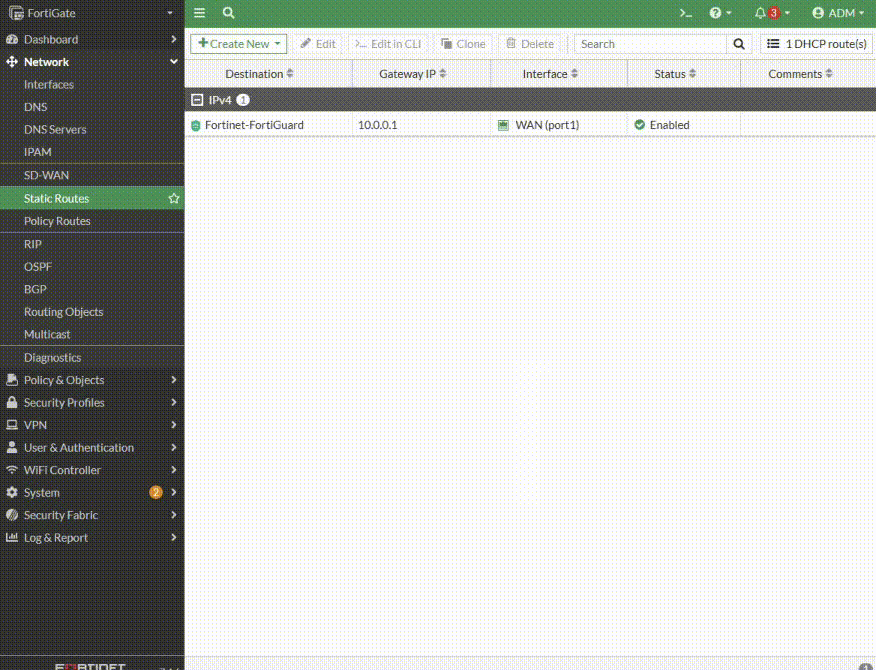
Select 'Internet Service' as the Destination.
Select the Internet service from the drop-down menu.
Add the gateway IP address.
Select the Internet Interface.
Select 'OK' to save the changes.
From the CLI:
config router static
    edit <ID>
        set gateway <Gateway of Internet interface>
        set device <internet interface>
        set internet-service <Internet Service ID #>
    next
end
The following command will provide the list of available Internet services:
diagnose firewall internet-service list
The ISDB static route will not create an entry directly in the routing-table.
Here, ISDB acts as a policy route. To verify the ISDB route, run:
diagnose firewall proute list
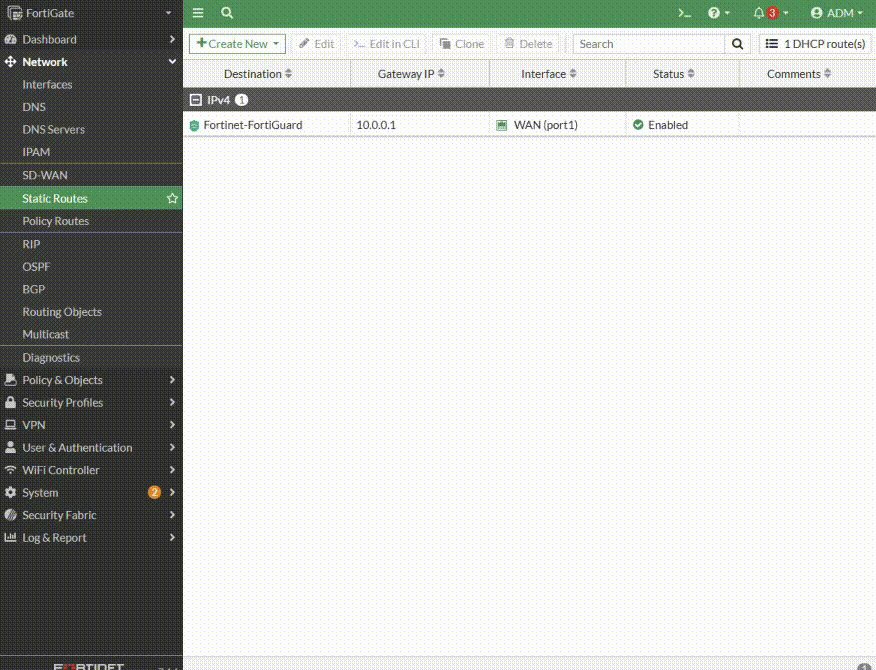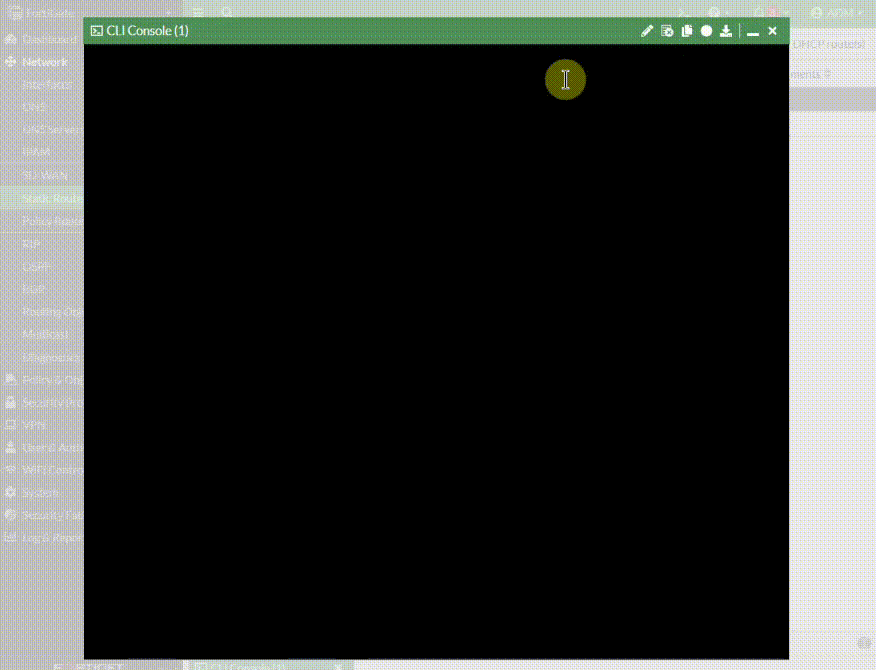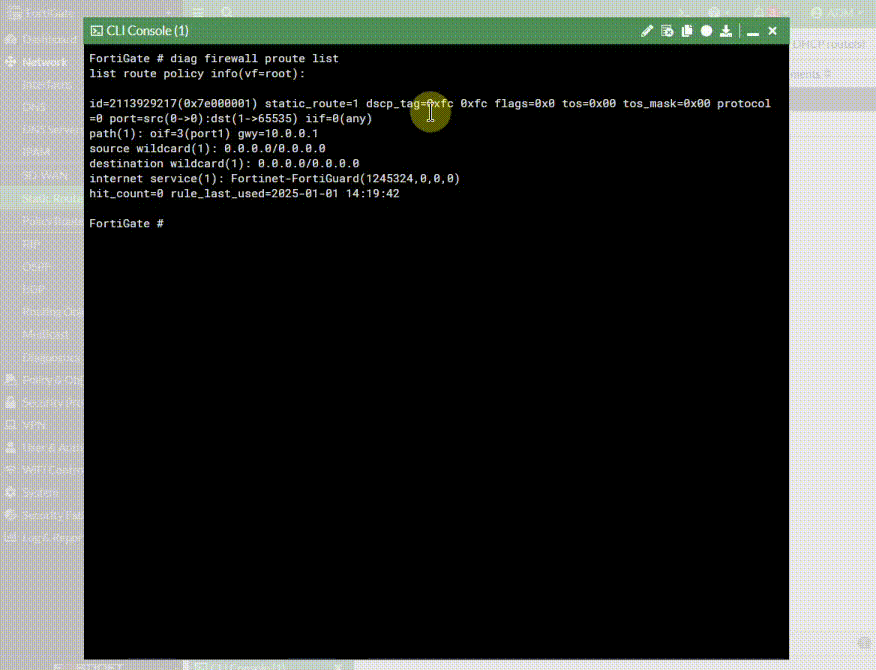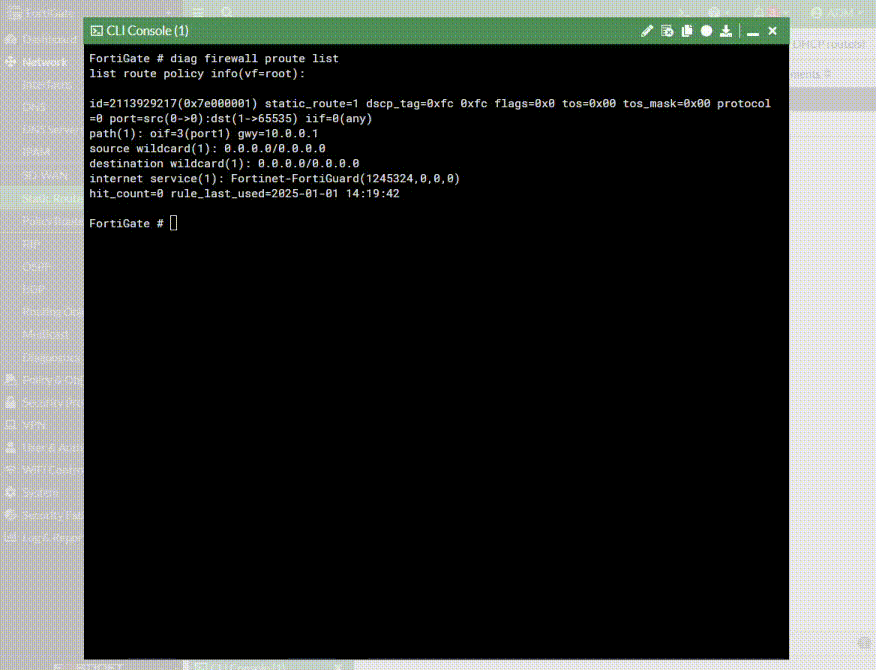
This means that ISDB routes apply the same rules as policy-routes.
For policy-routes to work, it is necessary to have a valid route in the routing-table for the outgoing interface because the traffic will not follow a policy route otherwise.
Consider a scenario where the ISDB route is used with IPsec as the exit interface.
For example: routing the traffic for 'Microsoft-Office365', 'Microsoft-Office365.Published' and 'Microsoft-Skupe_Teams' via IPsec with a configuration that looks like the following:
config router static
	edit 1
		set gateway 10.191.31.254
		set device "port3"
	next
	edit 2
		set device "ipsec"
		set internet-service 327782
	next
	edit 3
		set device "ipsec"
		set internet-service 327880
	next
	edit 4
		set device "ipsec"
		set internet-service 327781
	next
end
In this case, the ISDB routes associated with IPsec will not be respected because a next hop is not available.
When configuring an ISDB route, it is necessary to configure a next-hop. This is not possible for IPsec, so it is necessary to configure a second static default route with the same AD and a different priority than the primary default route to make ISDB routes with IPsec work:
get router info routing-table database
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
> - selected route, * - FIB route, p - stale info

Routing table for VRF=0
S *> 0.0.0.0/0 [10/0] via 10.191.31.254, port3, [1/0]
*> [10/0] via ipsec tunnel 10.10.250.1, [40/0]      <- Newly added.
C *> 10.10.250.0/24 is directly connected, port1
C *> 10.10.251.0/24 is directly connected, port2
C *> 10.191.16.0/20 is directly connected, port3
C *> 190.190.190.0/24 is directly connected, port4
With this additional default static route, it is possible to have working ISDB routes with an IPsec interface. There is a valid route pointing to the next hop 10.10.250.1. This is necessary to route ISDB routes via IPsec.
Related article:


