Technical Tip: Configuring IS-IS route summarization
Description
This article describes how to configure route summarization in Intermediate System to Intermediate System (IS-IS) networks to effectively manage the scale of the Link State Database (LSDB) and optimize routing tables on FortiGate devices.
While summarization is typically configured on Level-1/2 (L1/L2) border routers to aggregate Level-1 internal routes before advertising them into the Level-2 backbone, FortiOS also supports summarizing external routes directly within a Level-1 area.
When external prefixes (such as local connected networks, static routes, or routes redistributed from other routing protocols like BGP or OSPF) are injected into an IS-IS Level-1 area, the redistributing router advertises each individual subnet. In environments with numerous local subnets, this default behavior can quickly bloat the routing tables of Level-1-only neighboring routers and increase Shortest Path First (SPF) calculation overhead.
By utilizing the summary-address feature, FortiGate can suppress these individual component prefixes and inject a single, aggregated summary prefix into the routing domain. Depending on the topology, this can be applied at Level-1, Level-2, or Level-1-2.
Scope
FortiGate, IS-IS, Route Summarization.
Solution
To demonstrate the solution, the following scenario was used:
FGT-B has two local subnets (192.168.200.0/24 on port3 and 192.168.201.0/24 on port4) that will be summarized into a single 192.168.200.0/23 block before being advertised over the point-to-point IS-IS link (port2) to FGT-A.
Step 1: Enable connected route redistribution on FGT-B.
Configure the redistribution of the local connected subnets under the IS-IS routing process.
config router isis
    config redistribute "connected"
        set status enable
        set level level-1
    end
end
Step 2: Configure the Level-1 summary address on FGT-B.
Add the summary address entry to aggregate 192.168.200.0/24 and 192.168.201.0/24 into 192.168.200.0/23. The target level must be specified using the set level level-1 parameter.
config router isis
    config summary-address
        edit 1
            set prefix 192.168.200.0 255.255.254.0
            set level level-1
        next
    end
end
Verification:
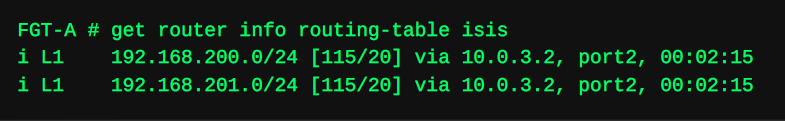
Verify the routing table on FGT-A (the Level-1 neighbor) before applying the summarization on FGT-B. FGT-A learns both individual subnets via next-hop 10.0.3.2 on port2:
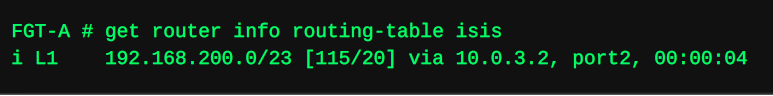
After enabling the summary-address on FGT-B, verify the routing table on FGT-A again. The specific /24 subnets are suppressed, and only the single aggregated /23 prefix is present:
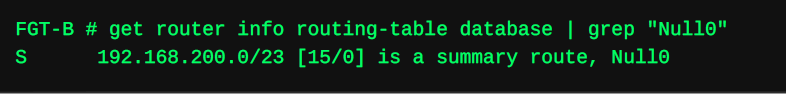
Additionally, verify that FortiOS has automatically installed a discard route (pointing to Null0) on the summarizing router (FGT-B) to prevent routing loops for the summary block: