Technical Tip: Blocking ServiceNow Remote Code Execution Attack in FortiGate
| Description | This article describes how to block the 'ServiceNow Remote Code Execution' attack with FortiGate. |
| Scope | FortiGate, Intrusion Prevention. |
| Solution | There is already a newly created signature which handles the block of the 3 CVEs involved to this attack. The CVEs are CVE-2024-4879, CVE-2024-5217, CVE-2024-5178. More information is disclosed in the corresponding FortiGuard encyclopedia article.
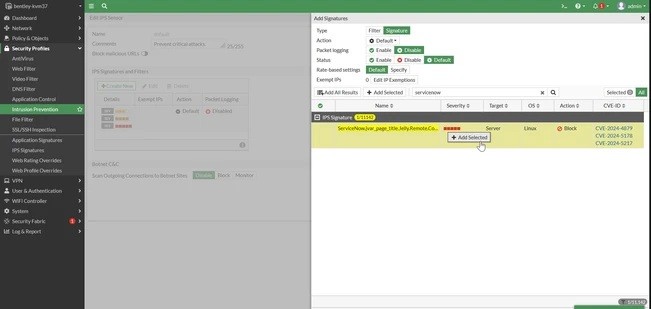
In order to block this attack via FortiGate, it is necessary to add the 'ServiceNow.jvar_page_title.Jelly.Remote.Code.Execution' signature in the Intrusion Prevention profile. For this attack, the default action is 'Block'. In this example, it was used on FortiGate in firmware 7.0.15.
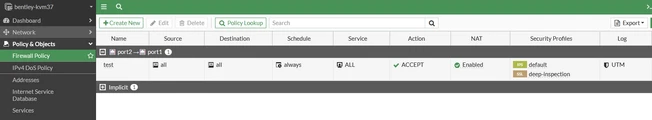
After, apply the Intrusion Prevention profile in a Firewall Policy which handles traffic to and from this application:
If the signature is not shown in the FortiGate Intrusion Prevention profile, run the following command to update the IPS database: execute update-now |