mle2802
Staff
Staff
Sep 7, 2023 2:54 PM UTC

Technical Tip: Authentication type with IPsec dial-up

  • Apr 24, 2026 3:24 PM UTC
  • 1 reply
  • 3520 views
  • Translate All
Description

This article describes why RADIUS is configured with PAP but IPsec dial-up authentication is still sent using MS-CHAP v2.

Scope

FortiGate.

Solution

A RADIUS server is configured using PAP as the authentication type:


show

config user radius

    edit "Duo-RADIUS"

        set server "172.16.2.1"

        set radius-port 1812

        set auth-type pap

    next

end


However, when running fnbamd debug for IPsec VPN, it is possible to see that the authentication type is sent using MS-CHAPv2 instead:


Debug Commands to collect the logs for external authentication: 


diagnose debug enable

diagnose debug console timestamp enable
diagnose debug application fnbamd -1


To stop this debug type:


diagnose debug application fnbamd 0

diagnose debug reset


[1906] handle_req-Rcvd auth req 963834393 for henry@test.com in FortiClient IPSEC Users opt=00000000 prot=5
[466] __compose_group_list_from_req-Group 'FortiClient IPSEC Users', type 1
[616] fnbamd_pop3_start-henry@test.com
[587] __fnbamd_cfg_get_radius_list_by_group-Loading RADIUS server 'Duo-RADIUS' for usergroup 'FortiClient IPSEC Users' (1)
[342] fnbamd_create_radius_socket-Opened radius socket 13
[342] fnbamd_create_radius_socket-Opened radius socket 14
[1394] fnbamd_radius_auth_send-Compose RADIUS request
[1351] fnbamd_rad_dns_cb-172.16.2.1->172.16.2.1
[1323] __fnbamd_rad_send-Sent radius req to server 'Duo-RADIUS': fd=13, IP=172.16.2.1(172.16.2.1:11812) code=1 id=167 len=213 user="henry@test.com" using MS-CHAPv2

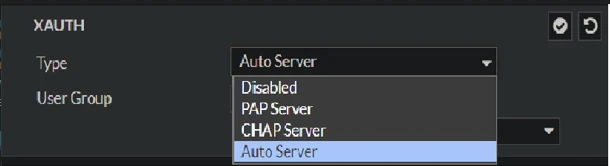
This happens because the xauth type under IPsec configuration is set to 'auto'. It is possible to force the device to use PAP with the following commands:


config vpn ipsec phase1-interface

     edit <Tunnel_name>

         set xauthtype pap
end

Note: For the GUI, convert the tunnel to 'custom'. The 'Type' section will then be possible to change in the XAUTH tab.

Untitled.png


After that, run the fnbamd debug again. Upon trying to authenticate, PAP will be used accordingly:


diagnose debug enable

diagnose debug console timestamp enable
diagnose debug application fnbamd -1


To stop this debug type:


diagnose debug application fnbamd 0

diagnose debug reset


[1802] fnbamd_radius_auth_validate_pkt-RADIUS resp code 3
[1385] fnbamd_auth_handle_radius_result-->Result for radius svr 'Duo-RADIUS' 172.16.2.1(1) is 1
[1394] fnbamd_radius_auth_send-Compose RADIUS request
[1323] __fnbamd_rad_send-Sent radius req to server 'Duo-RADIUS': fd=13, IP=172.16.2.1(172.16.2.1:11812) code=1 id=169 len=149 user="henry@test.com" using PAP
[319] radius_server_auth-Timer of rad 'Duo-RADIUS' is added
[2612] handle_auth_rsp-Continue pending for req 963834393
[47] handle_rad_timeout-rad 'Duo-RADIUS' 172.16.2.1 timed out, resend request.
[1323] __fnbamd_rad_send-Sent radius req to server 'Duo-RADIUS': fd=13, IP=172.16.2.1(172.16.2.1:11812) code=1 id=169 len=149 user="henry@test.com" using PAP


Related article:

Troubleshooting Tip: Using IKEv2 for a dial-up IPsec tunnel with a RADIUS server and Local user

1 reply

dhu2022
Staff
Staff
May 22, 2024 10:44 PM UTC

This post is very helpful!!

Translate
Risk and Resilience in the Age of AI. An OT Thought Leadership Summit for Houston's Critical Infrastructure Leaders. Date: Thursday, December 3, 2026. Time: 8:30 am - 1:30 pm (CT). Location: The Westin Houston, Memorial City | 945 Gessner Road, Houston, TX 77024