There are significant differences on connectivity behavior when it comes to Copilot, which introduces some caveats specifically for Microsoft 365 Copilot. The following are three ways to access Copilot and an explanation of how FortiGate can block it: When using the browser to access copilot.microsoft.com, a simple firewall policy that uses Certificate Inspection in conjunction with either DNS Profile/Web Filter (matching on copilot.microsoft.com) or Application Control (Application ID 53352) will suffice to block it. This can be verified via the CLI. For example:
Firewall-1 # diagnose sys session list | grep -A 5 -B 10 53352

session info: proto=6 proto_state=11 duration=4 expire=28 timeout=3600 flags=00000000 socktype=0 sockport=443
hook=post dir=org act=snat 10.127.11.87:64955->104.18.23.222:443(10.5.211.222:64955)
hook=pre dir=reply act=dnat 104.18.23.222:443->10.5.211.222:64955(10.127.11.87:64955)
hook=post dir=reply act=noop 104.18.23.222:443->10.127.11.87:64955(0.0.0.0:0)
pos/(before,after) 0/(0,0), 0/(0,0)
misc=0 policy_id=95 pol_uuid_idx=1193 auth_info=0 chk_client_info=0 vd=0
serial=0002378a tos=08/08 app_list=2007 app=53352 url_cat=0
rpdb_link_id=00000000 ngfwid=n/a
npu_state=0x041108
no_ofld_reason: redir-to-av block-by-ips redir-to-ips denied-by-nturbo non-npu-intf
In this case, there is a match for Copilot App ID 53352.
Note how the traffic is destined for 104.18.23.222, which is one of the two current A Records for Copilot: C:\Users est>nslookup copilot.microsoft.com
Non-authoritative answer:
Name: copilot.microsoft.com.cdn.cloudflare.net
104.18.22.222
104.18.23.222
Copilot Application: The same configurations shown in point 1 can be used and the connection will be blocked. This can be observed in the packet capture below, which shows how the traffic is directly destined for Copilot:
 Microsoft 365 Copilot uses a different way of pushing traffic with its embedded Copilot Chat. In this case, there are no DNS requests seen to copilot.microsoft.com or any Layer3 connectivity towards the two well-known IPs 104.18.22.222 and 104.18.23.222. Even after enabling Deep Inspection, the traffic logs, application control, and session list logs show flows for the Application Microsoft Portal (App IDs 41468 & 41469) and not Copilot (App ID 53352), and there are several DNS requests to 'substrate.office.com', the client calls the Copilot agent list (GetGptList) on 'substrate.office.com' first and then on 'substrate.svc.cloud.microsoft', so traffic is allowed as FortiGate cannot recognize it as belonging to Copilot.
In this case, traffic is not directly pushed to Copilot. The only way to block it is by matching Microsoft Portal or substrate.office.com, although this can have undesired effects since this will likely affect other Microsoft flows. As a result, the recommendation is to block it at the host level: Firewall-1 # diagnose sys session list | grep -A 5 -B 10 41469
hook=post dir=org act=snat 192.168.2.22:34321->20.44.10.123:443(10.10.10.1:34321)
hook=pre dir=reply act=dnat 20.44.10.123:443->10.10.10.1:34321(10.10.10.1:34321) <----- Microsoft IP.
hook=post dir=reply act=noop 20.44.10.123:443->192.168.2.22:34321(0.0.0.0:0)
pos/(before,after) 0/(0,0), 0/(0,0)
misc=0 policy_id=114 pol_uuid_idx=1118 auth_info=0 chk_client_info=0 vd=0
serial=09d6e92d tos=08/08 app_list=2010 app=41469 url_cat=0
sdwan_mbr_seq=2 sdwan_service_id=5
rpdb_link_id=ff000005 ngfwid=n/a
npu_state=0x001001 no_offload
no_ofld_reason: block-by-ips disabled-by-policy redir-to-ips
To keep Outlook search and other features working, block only the Copilot paths(which can be verified from a HAR file also) using a web-filter profile:
Create the URL filter table for specific URL paths.
config webfilter urlfilter
edit 1
set name "Block-M365-Copilot-URLs"
config entries

edit 1
set url "*.outlook.office.com/hosted/semanticoverview*"
set type wildcard
set action block
set status enable
next

edit 2
set url "*.substrate.office.com/m365Copilot*"
set type wildcard
set action block
set status enable
next

edit 3
set url "**.substrate.svc.cloud.microsoft/m365Copilot*"
set type wildcard
set action block
set status enable
next

end
next
end
The above paths are for Copilot chats, agent list, prompts, settings, and side pane.
Create the web filter profile.
config webfilter profile
edit "WF-Block-M365-Copilot"
config web
set urlfilter-table 1
end
next
end
Apply it to the firewall policy.
config firewall policy
edit "WF-Block-M365-Copilot"
set utm-status enable
set ssl-ssh-profile "deep-inspection"
set webfilter-profile "WF-Block-M365-Copilot"
next
end
In GUI:
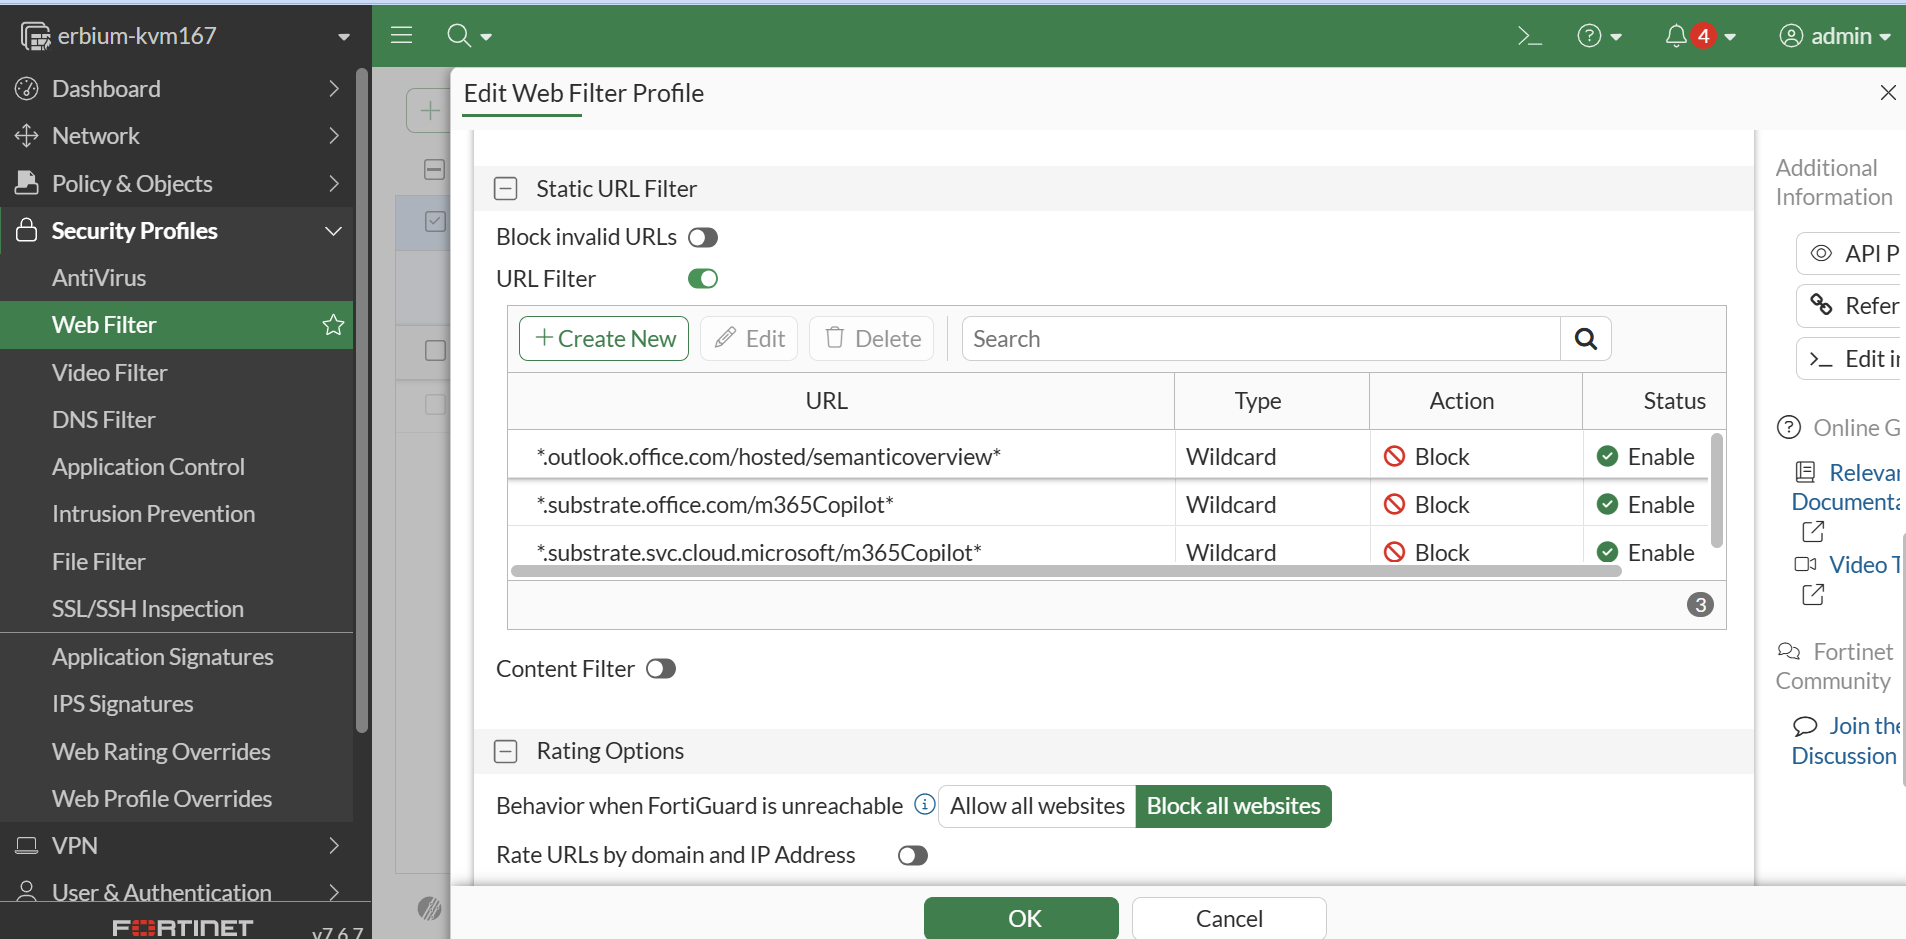
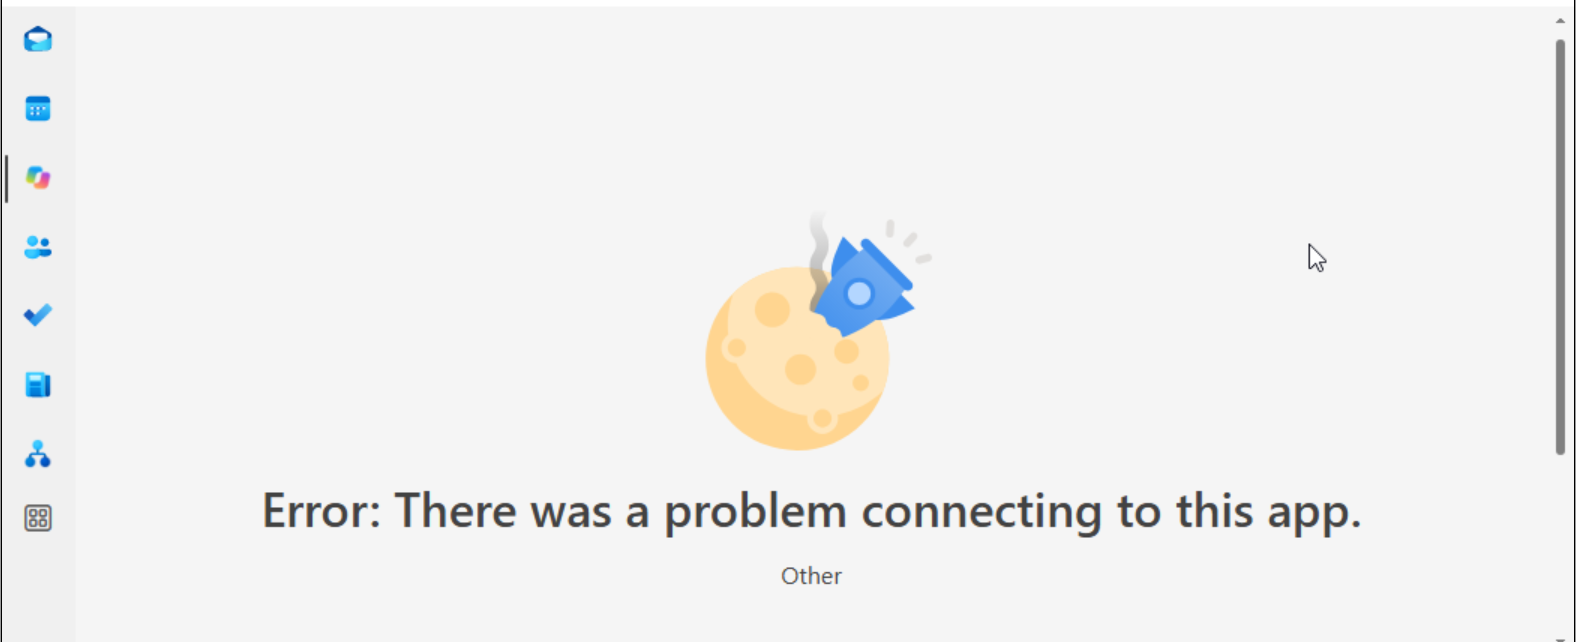
Once the Web Filter profile is applied to the relevant firewall policy with deep inspection enabled, and the client machines are configured to trust the FortiGate inspection CA certificate, Copilot will be blocked, as indicated by the log and error message below.
date=2026-10-28 time=01:50:11 eventtime=1793177410720254153 tz="-0700" logid="0315012544" type="utm" subtype="webfilter"
eventtype="urlfilter" level="warning" vd="root" urlfilteridx=1 urlfilterlist="Auto-webfilter-urlfilter_ecankkk98" policyid=1
policytype="policy" sessionid=104012 srcip=x.x.x.x srcport=53940 srccountry="Reserved" srcintf="port3" srcintfrole="undefined"
dstip=52.98.151.242 dstport=443 dstcountry="France" dstintf="port1" proto=6 httpmethod="GET" service="HTTPS" hostname="outlook.office.com"
agent="Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KH" profile="default" action="blocked" reqtype="direct"
url="https://outlook.office.com/hosted/semanticoverview/Users..." sentbyte=537964 rcvdbyte=339264 direction="outgoing"
urlsource="Local URLfilter Block" msg="URL was blocked because it is in the URL filter list" crscore=30 craction=8 crlevel="high"
 | 



