


FortiAppSec Cookie Security causing HTTP 403 Forbidden errors
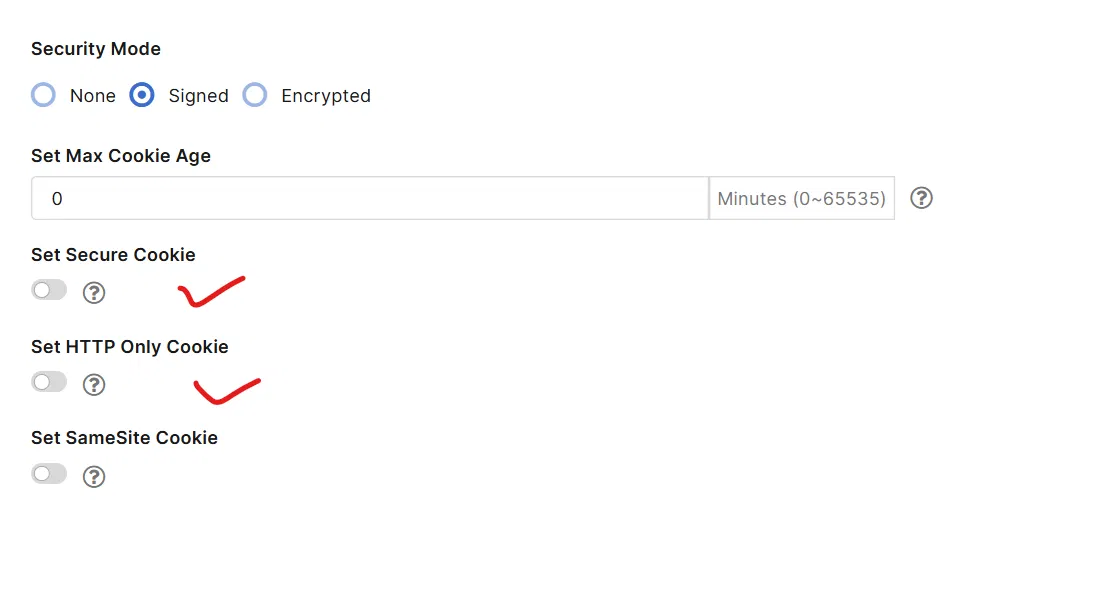
Description | Enabling the Set HttpOnly Cookie feature in FortiWeb Cloud may cause applications to return HTTP 403 Forbidden errors if the application relies on JavaScript to read CSRF tokens from cookies. |
Scope | FortiAppSec Cloud. |
Solution | SymptomsUsers encounter HTTP 403 Forbidden (Authentication Error) responses on various application pages after a successful login. These errors occur specifically when Cookie Security features are enabled in FortiWeb Cloud. No corresponding security violations or blocks appear in the Web Application Firewall (WAF) event logs, even when the policy is set to Alert mode. Root CauseThe issue is caused by the ResolutionDisable the
|

