Technical Tip: Using VIP with specific phase2 selectors for bidirectional traffic requirements
| Description | This article describes how to use a VIP object in FortiGate for bidirectional traffic when the requirement involves a specific Phase 2 selector, without needing to use an IP Pool for SNAT. This setup is typically necessary for business-to-business connections where both parties need to specify which IP addresses are permitted to communicate. |
| Scope | 7.0, 7.2, 7.4. |
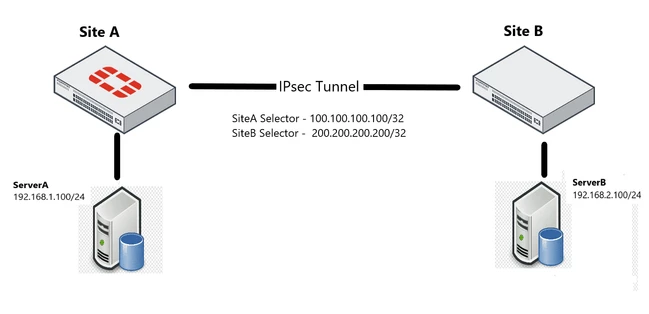
| Solution | In this diagram, both Server A and Server B need to communicate with each other through the IPsec tunnel, with either side allowed to initiate the traffic. Server A is required to use 100.100.100.100 as its NAT IP.
Phase2-interface configuration
config vpn ipsec phase2-interface edit "ToSiteB" set phase1name "ToSiteB" next Only the VIP object is required in Site A (FortiGate) for this requirement to be fulfilled.
config firewall vip edit "ServerA-SiteB-VIP" set uuid 1cd14a88-6b51-51ef-736a-2feef4af85c7 next end For outbound traffic (Server A to Server B):
edit 4 set name "FromLANtoSiteB" next
For inbound traffic (Server B to Server A):
config firewall policy edit 3 set name "FromSiteBtoLAN" end |