syao
Staff & Editor
Staff & Editor
August 16, 2023

Technical Tip: Using NTRadPing with RSSO

  • August 16, 2023
  • 0 replies
  • 3413 views
Description

This article describes that NTRadPing is a freeware Windows utility that can be used to test RADIUS authentications.

It can act as a RADIUS user to any RADIUS server to test.

It is possible to use NTRadPing to send an accounting request (start or stop) directly to FortiGate for troubleshooting isolation purposes. This can be done without using a separate RADIUS server.

Scope FortiGate, Windows 7, Windows 10, Windows 11.
Solution
  1. Configure the RSSO Agent in the FortiGate:


config user radius
    edit "RSSO Agent"
        set rsso enable
        set rsso-radius-response enable
        set rsso-validate-request-secret enable
        set rsso-secret fortinet
        set rsso-endpoint-attribute User-Name
    next
end


     2. Enable Radius Accounting on the FortiGate interface:


config system interface
    edit "port3"
         set vdom "root"
         set ip 10.129.3.71 255.255.240.0

append allowaccess radius-acct 
end

     3. Create the RSSO User group:


config user group
    edit "RSSO-GRP1"
        set group-type rsso
        set sso-attribute-value "Group1"
    next
end

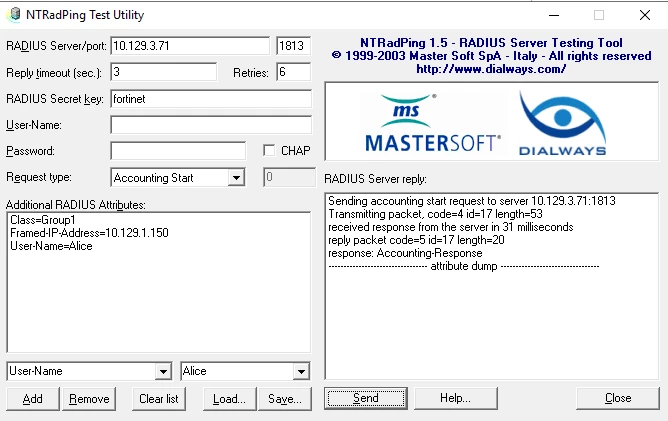
     4. On the NTRadPing, specify the following:


start.png


  1. Radius Server/Port: Specify the FortiGate IP.
  2. Radius Secret Key: Specify the secret key.
  3. Request Type: From the drop-down option, choose 'Accounting Start'.
  4. Class: This should match the value of 'sso-attribute-value ' of the RSSO group.
  5. Framed-IP-Address: This value will be used by the FortiGate for user-ip mapping.
  6. User-Name: This value will be used by the FortiGate for user-ip mapping.


     5. Select the Send button to generate the test packet and check the user mapping in the FortiGate:


FORTIGATE # diagnose firewall auth list

10.129.1.150, Alice
type: rsso, id: 0, duration: 100, idled: 100
flag(10): radius
server: root
packets: in 0 out 0, bytes: in 0 out 0
group_id: 2
group_name: RSSO-GRP1

----- 1 listed, 0 filtered ------


Enable RSSO debug:


FORTIGATE # diagnose debug application radiusd -1

FORTIGATE # diagnose debug enable


Received radius accounting event
vd 0:root Add/Update auth logon for IP 10.129.1.150 for user Alice
DB 0 insert [ep='Alice' pg='Group1' ip='10.129.1.150/32'] success <-----


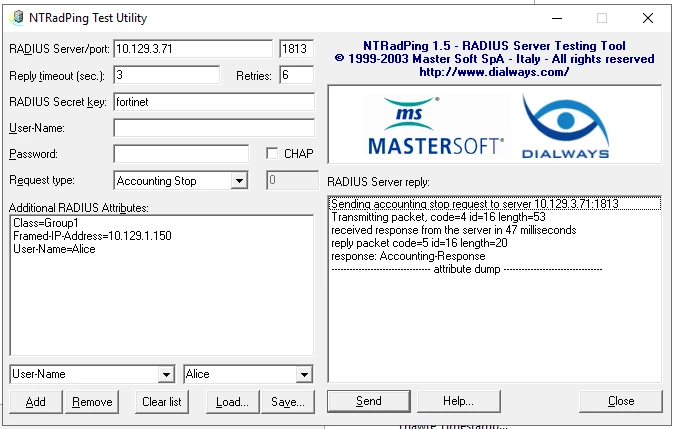
     6. (Optional) Change the Request Type to 'Accounting Stop' to log off the test user:


stop.png


FORTIGATE # diagnose firewall auth list

----- 0 listed, 0 filtered ------


Enable RSSO debug:


FORTIGATE # diagnose debug application radiusd -1

FORTIGATE # diagnose debug enable


Received radius accounting event
vd 0:root Remove auth logon for IP 10.129.1.150 for user Alice
DB 0 remove by IP [ep='Alice' pg='Group1' ip='10.129.1.150/32'] success <-----
Send accounting response

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.