When configuring FortiGate for service publishing, two primary methods are available: Virtual Server and Virtual IP (VIP). Each method functions differently, particularly in how traffic is inspected and handled. The mapping of a specific IP address to another specific IP address is usually referred to as Destination NAT (DNAT). On FortiGate VIP and Virtual server features can be used as DNAT. VIP: When the Central NAT is not being used, FortiOS calls this a Virtual IP Address, sometimes called a VIP. FortiOS uses a DNAT or Virtual IP address to map an External IP address to an IP address. This address does not have to be an individual host, it can also be an address range. Virtual server: This is a special virtual IP type. Use this type of VIP to implement server load balancing.
Preference:
Virtual Server and VIP do not have a fixed preference over each other.
When Central NAT is disabled, FortiGate evaluates Virtual Servers and VIPs using the same DNAT policy list, and the first matching object under config firewall vip is used for destination NAT.
Scenario 1:
Under 'config firewall vip'
VIP is Placed above the Virtual Server:
config firewall vip
    edit "testVIP"
        set extip 10.0.0.46
        set mappedip "192.168.11.100"
        set extintf "wan1"
        set portforward enable
        set extport 3389
        set mappedport 3389
    next
    edit "testVirtualServer"
        set type server-load-balance
        set server-type tcp
        set extip 10.0.0.46
        set extintf "any"
        set extport 3389
        config realservers
            edit 1
                set ip 192.168.11.100
                set port 3389
            next
        end
FIrewall policy handling VIP is placed below the policy with Virtual server,

Traffic is matched to VIP firewall policy:
FortiWiFi-70G-POE # id=65308 trace_id=313 func=print_pkt_detail line=6019 msg="vd-root:0 received a packet(proto=6, 206.47.132.11:56397->10.0.0.46:3389) tun_id=0.0.0.0 from wan1. flag [S], seq 996625816, ack 0, win 65535"
id=65308 trace_id=313 func=init_ip_session_common line=6220 msg="allocate a new session-0044c7b2"
id=65308 trace_id=313 func=get_new_addr line=1280 msg="find DNAT: IP-192.168.11.100, port-3389"
id=65308 trace_id=313 func=fw_pre_route_handler line=191 msg="VIP-192.168.11.100:3389, outdev-wan1"
id=65308 trace_id=313 func=__ip_session_run_tuple line=3539 msg="DNAT 10.0.0.46:3389->192.168.11.100:3389"
id=65308 trace_id=313 func=__vf_ip_route_input_rcu line=1989 msg="find a route: flag=00000000 gw-0.0.0.0 via VM"
id=65308 trace_id=313 func=__iprope_tree_check line=524 msg="gnum-100004, use int hash, slot=74, len=5"
id=65308 trace_id=313 func=fw_forward_handler line=1002 msg="Allowed by Policy-14:"
Scenario 2:
Under 'config firewall vip'
Virtual Server is Placed above the VIP:
   config firewall vip
    edit "testVirtualServer"
        set type server-load-balance
        set server-type tcp
        set extip 10.0.0.46
        set extintf "any"
        set extport 3389
        config realservers
            edit 1
                set ip 192.168.11.100
                set port 3389
            next
        end
    next
    edit "testVIP"
        set extip 10.0.0.46
        set mappedip "192.168.11.100"
        set extintf "wan1"
        set portforward enable
        set extport 3389
        set mappedport 3389
    next
Firewall policy handling the Virtual server is placed below the policy with the VIP:
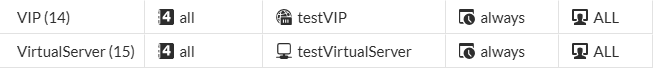
Traffic is matched to the Virtual Server firewall policy:
FortiWiFi-70G-POE # id=65308 trace_id=318 func=print_pkt_detail line=6019 msg="vd-root:0 received a packet(proto=6, 206.47.132.11:60011->10.0.0.46:3389) tun_id=0.0.0.0 from wan1. flag [S], seq 634539142, ack 0, win 65535"
id=65308 trace_id=318 func=init_ip_session_common line=6220 msg="allocate a new session-0044c9ba"
id=65308 trace_id=318 func=fw_pre_route_handler line=191 msg="VIP-192.168.11.100:3389, outdev-wan1"
id=65308 trace_id=318 func=__ip_session_run_tuple line=3539 msg="DNAT 10.0.0.46:3389->192.168.11.100:3389"
id=65308 trace_id=318 func=__vf_ip_route_input_rcu line=1989 msg="find a route: flag=00000000 gw-0.0.0.0 via VM"
id=65308 trace_id=318 func=__iprope_tree_check line=524 msg="gnum-100004, use int hash, slot=74, len=5"
id=65308 trace_id=318 func=fw_forward_handler line=1002 msg="Allowed by Policy-15:"
Behavioral Differences:
Traffic published via a VIP does not undergo the same level of deep inspection as a Virtual Server. This is why traffic may pass through without issues when using a VIP, while it may face certificate errors with a Virtual Server. Load Balancing Considerations: One advantage of Virtual Servers is built-in load balancing across multiple backend servers, making them ideal for large-scale environments. However, this feature can introduce traffic inspection issues, such as certificate mismatches or failures. Recommendation: If advanced features such as load balancing and SSL inspection are required, a Virtual Server is the better choice. However, for a more straightforward service publishing setup with minimal configuration, using a VIP is recommended. This explanation should help clarify the behavioral differences between Virtual Servers and Virtual IPs, and guide the selection of the most suitable option based on network requirements. | 



