


Technical Tip: Setup FortiAP as sniffer to collect air packet capture
Description
This document describes how to configure FortiAP as a sniffer to collect air packet capture.
Related links.
https://docs.fortinet.com/product/wireless-controller/8.5
Page# 502: https://fortinetweb.s3.amazonaws.com/docs.fortinet.com/v2/attachments/f8902d66-dfb2-11e9-8977-00505692583a/Fortiwlc-sd-v8.5.1-userguide.pdf
Solution
Below steps explain how to collect Wireless captures using the nearest sibling AP.
The sniffing FortiAP has to be near by the problem client and its associated AP within -60 dbm RSSI for better results.
1) Need to remove the ess-profile/vap entries from the sniffer FortiAP before starting the capture.
2) Commands to enable the sniffer:
After getting the captures, make sure to disable the sniffer and add the initially removed ess-ap-table entries back on the sniffer FortiAP.
From GUI.
Before starting the FortiAP packet capture, remove the ess-profile/VAP from the sniffer FortiAP.
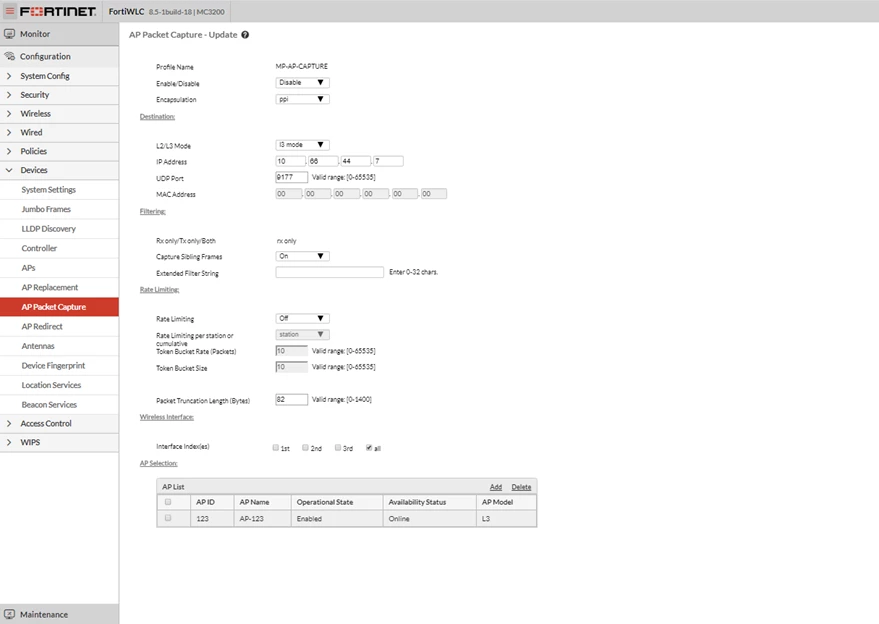
Go to Configuration -> Devices -> AP Packet Capture and add a profile.
This document describes how to configure FortiAP as a sniffer to collect air packet capture.
Related links.
https://docs.fortinet.com/product/wireless-controller/8.5
Page# 502: https://fortinetweb.s3.amazonaws.com/docs.fortinet.com/v2/attachments/f8902d66-dfb2-11e9-8977-00505692583a/Fortiwlc-sd-v8.5.1-userguide.pdf
Solution
Below steps explain how to collect Wireless captures using the nearest sibling AP.
The sniffing FortiAP has to be near by the problem client and its associated AP within -60 dbm RSSI for better results.
1) Need to remove the ess-profile/vap entries from the sniffer FortiAP before starting the capture.
2) Commands to enable the sniffer:
wlc#conn ap <ap-id>3) Once capture is completed, stop the sniffer on the FortiAP by executing the below command.
ap-id>sniff destport 9177
ap-id>sniff destmode l3
ap-id>sniff destaddr <----- IP of the PC with Wireshark.
ap-id>sniff enable on all
ap-id>sniff enable off allNote.
After getting the captures, make sure to disable the sniffer and add the initially removed ess-ap-table entries back on the sniffer FortiAP.
From GUI.
Before starting the FortiAP packet capture, remove the ess-profile/VAP from the sniffer FortiAP.
Go to Configuration -> Devices -> AP Packet Capture and add a profile.


