

Technical Tip: Terminal server sessions missing in Fortinet Single-Sign-On
Description
This article describes an interaction between FortiAuthenticator and TS Agent that can cause user sessions to go missing from FortiAuthenticator unexpectedly.
Scope
FortiAuthenticator.
Solution
In environments with terminal servers and Fortinet Single-Sign-On (FSSO), under some circumstances user sessions might be missing from FortiAuthenticator, and thus cause dependent FortiGates to not identify the traffic correctly.
In particular, this can happen for very long-lasting terminal server/RDP sessions.
This arises from how Terminal Server (TS) Agent handles logins, and a timeout setting on FortiAuthenticator:
- Terminal Server Agent only reports new user sessions to FortiAuthenticator and the assigned port ranges; it does not keep track or inform FortiAuthenticator of persisting user sessions
- FortiAuthenticator has a hard timeout configured for Single-Sign-On sessions under Fortinet SSO -> Settings -> FortiGate, the 'Login Expiry' timer:
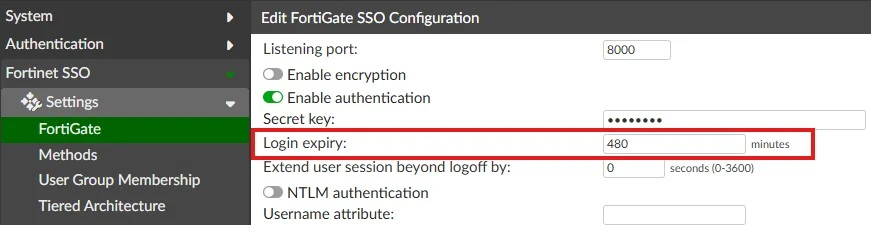
For Event log/DC Agent user sessions, typically, there will be frequent new login events observed for logged-in users, resetting the timer.
This does not happen for user sessions from the TS Agent, meaning that even if the user session is still present on the Terminal Server, FortiAuthenticator will apply the Expiry timer and remove the login.
Affected users will need to actively log out and log in to the Terminal Server again (not just resume an existing session) to generate a new login that TS Agent will share with FortiAuthenticator.
A possible solution is to configure a timeout for RDP/Terminal Server sessions on the Windows side to be in line with the Login expiry on FortiAuthenticator, as described here for example: http://woshub.com/remote-desktop-session-time-limit/
Affected users will need to actively log out and log in to the Terminal Server again (not just resume an existing session) to generate a new login that TS Agent will share with FortiAuthenticator.
A possible solution is to configure a timeout for RDP/Terminal Server sessions on the Windows side to be in line with the Login expiry on FortiAuthenticator, as described here for example: http://woshub.com/remote-desktop-session-time-limit/
