Firasbg
Explorer II
July 30, 2022
Question

Where is my data of fortinet?

  • July 30, 2022
  • 4 replies
  • 3263 views

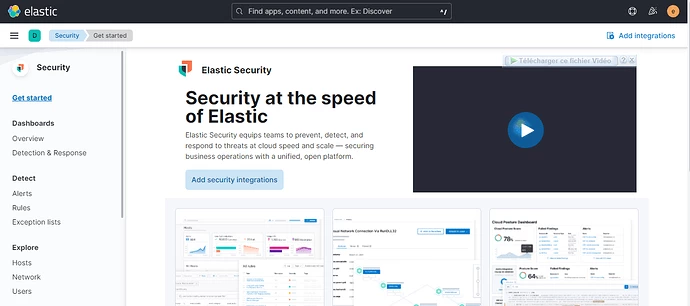
Hello, I installed Elasticsearch and kibana and filebeat in ubuntu 22.04 VM and i installed FortiGate 7.2.0 in other VM in VMware workstation, I follow the steps to upload the Fortinet logs in elastic and kibana as the first screenshot, and the data is successfully received from the Filebeat Fortinet module but when i clic in "security App" i don't find anything
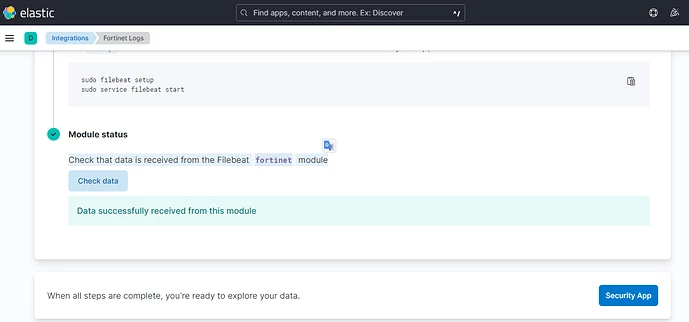
Firasbg_0-1659176241769.pngFirasbg_1-1659176253108.png

this my nano /etc/filebeat/modules.d/fortinet.yml:

- module: fortinet
firewall:
enabled: true

# Set which input to use between tcp, udp (default) or file.
var.input: udp

# The interface to listen to syslog traffic. Defaults to
# localhost. Set to 0.0.0.0 to bind to all available interfaces.
var.syslog_host: 192.168.37.2

# The port to listen for syslog traffic. Defaults to 9004.
var.syslog_port: 9004

# Set internal interfaces. used to override parsed network.direction
# based on a tagged interface. Both internal and external interfaces must be
# set to leverage this functionality.

and this my config log syslogd setting of fortigate :

FortiGate-VM64 # config log syslogd setting 
 
FortiGate-VM64 (setting) # show 
config log syslogd setting
    set status enable
    set server "192.168.37.2"
    set port 9004
end
 
FortiGate-VM64 (setting) #


4 replies

Anthony_E
Staff
Staff
August 2, 2022

Hello Firasbg,


Thank you for using the Community Forum.

I will seek to get you an answer or help. We will reply to this thread with an update as soon as possible.


Regards,

Best Regards
Markus_M
Staff & Editor
Staff & Editor
August 2, 2022

Hi Firasbg,


with a packet capture you should see whether FortiGate sends logs on the respective port 9004. Cannot really help on kibana or elasticsearch, but first I would make sure the devices receive the data from the FortiGate.

Then see whether the devices can read the data as to see the correct syslog format, separated correctly with correct delimiters.


Best regards,


Markus

Best regards, Markus
Firasbg
FirasbgAuthor
Explorer II
August 4, 2022

how to do that? how to do capture? how to see if the devices receive the FortiGate logs ??

i'am new in fortigate 

Debbie_FTNT
Staff & Editor
Staff & Editor
August 4, 2022

Hey Firasberg,

regarding a capture on FortiGate, you can check as outlined in the screenshot below:

Debbie_FTNT_0-1659629127018.png

Once you click on start, the screen will show a display of the ongoing capture with some basic info; if you end the capture, you can download a resulting pcap file and look at it in wireshark or similar.

This way you can verify if FortiGate is actually sending on port 9004.

As for checking on the receiving hosts, you should be able to use the tcpdump command in Ubuntu for example, but I'm not terribly familiar with it, my apologies.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT