RichardKo
New Member
January 9, 2023
Question

What setting can let splashtop go through

  • January 9, 2023
  • 10 replies
  • 5506 views

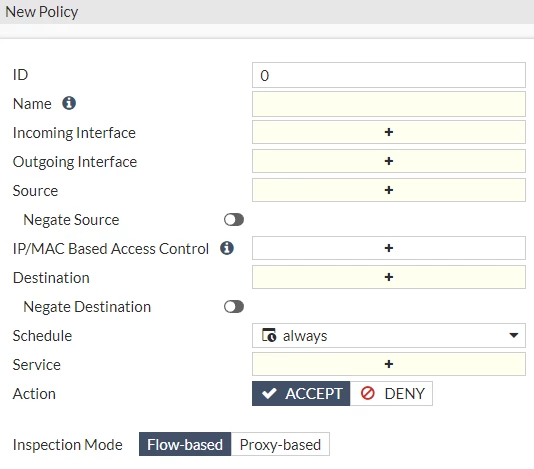
Does anyone know how to set up a policy that Splashtop can go through?

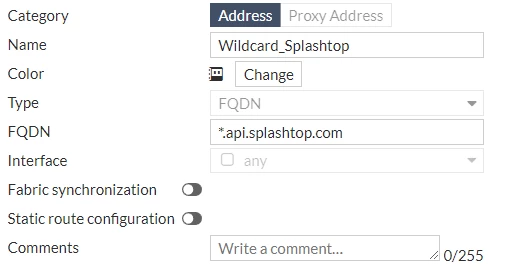
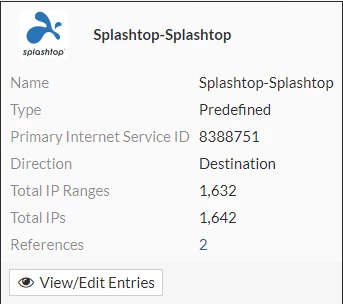
I try to create a wildcard address and use Internet Service in Destination, but none of those works.


Product: Fortigate 100E

Firmware: v7.2.2 build1255
FortiGate 

RichardKo_1-1673288515962.png


RichardKo_2-1673288634957.png


RichardKo_0-1673288430653.png


10 replies

AlexC-FTNT
Staff
Staff
January 10, 2023

Does it work when you allow all the traffic out? (without filtering by application/ISDB,etc? )

What protocol/ports does this app uses/needs? Did you disable SIP-ALG (by mistake or for some other reason)? What does the logs or debug flow tells you?

RichardKo
RichardKoAuthor
New Member
January 10, 2023

Because I have more than one subnet that, I need to set a specific policy for it.
It works if I allow all traffic, but that's not what I need.

The protocol is Internet Service.

RichardKo_0-1673379520843.png


RichardKo_1-1673379575747.png


gfleming
Staff
Staff
January 10, 2023

What are you trying to accomplish? By default all applications / web sites will be allowed through a firewall policy (assuming all ports and all IP addresses are allowed).


So, what is your end goal here in terms of "letting Splashtop through"?

RichardKo
RichardKoAuthor
New Member
January 10, 2023

I need to set up a specific policy for one subnet that only Splashtop can pass through.

gfleming
Staff
Staff
January 10, 2023

OK so create a policy for that one subnet that allows all traffic (including Splashtop). Then below it create another policy for all other networks that allows all traffic but blocks Splashtop.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!