fred_q
New Member
February 18, 2019
Solved

What Mode Should I Configure on the Port of My Switching that Connecting My Fortigate?

  • February 18, 2019
  • 1 reply
  • 3897 views

Hi All,

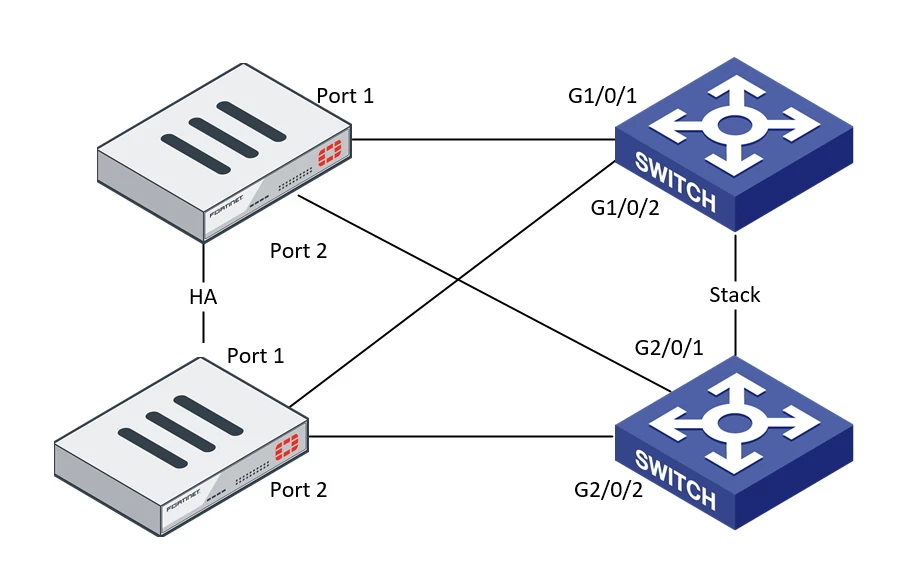
As show below picture

Fortigate 1 port 1 connects to Cisco switch G1/0/1

Fortigate 1 port 2 connects to Cisco switch G2/0/1

Fortigate 2 port 1 connects to Cisco switch G1/0/2

Fortigate 2 port 2 connects to Cisco switch G2/0/2


My questions are

1) My fortigates work on Active-Active mode, port 1 and port 2 are set as  1 802.3ad aggragate port. What should I configure my switch ports? All the four ports in one channel group? Or G1/0/1 and G2/0/1 in one channel group, G1/0/2 and G2/0/2 in other channel group?


2)  If my fortigates work on Active-Passive mode, port 1 and port 2 are set as  1 802.3ad aggragate port. What should I configure my switch ports? All the four ports in one channel group? Or G1/0/1 and G2/0/1 in one channel group, G1/0/2 and G2/0/2 in other channel group?


Thanks in advance!  Best regards

Best answer by Markus

Hi Maybe this can help https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-high-availability-52/HA_full_meshExample.htm We have coupleof FG in Production, but for now, we've never used Full-Mesh. We do 802.3ad aggragate too, but we don't use A-A, only A-P FG1 --> SW1 FG2 --> SW2 Best regards

1 reply

Markus
MarkusAnswer
New Member
February 25, 2019

Hi Maybe this can help https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-high-availability-52/HA_full_meshExample.htm We have coupleof FG in Production, but for now, we've never used Full-Mesh. We do 802.3ad aggragate too, but we don't use A-A, only A-P FG1 --> SW1 FG2 --> SW2 Best regards

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!