raffaeledp
Explorer III
February 14, 2025
Solved

What is wrong whit this policy?

  • February 14, 2025
  • 7 replies
  • 2616 views

Hello everybody,

I'm the Fortigate 60F (v7.2.10) admin, and I log into it at:


https://vpn.xxx.com:40443/


or


https://10.1.0.1:40443/


I defined a local-in policy to momentaneously deny the access to this page to all the users. All the policy above this one are disabled:


edit 5
set uuid d5c73f7a-eae5-51ef-8ecd-4cb99f22bef3
set intf "any"
set srcaddr "all"
set dstaddr "login"
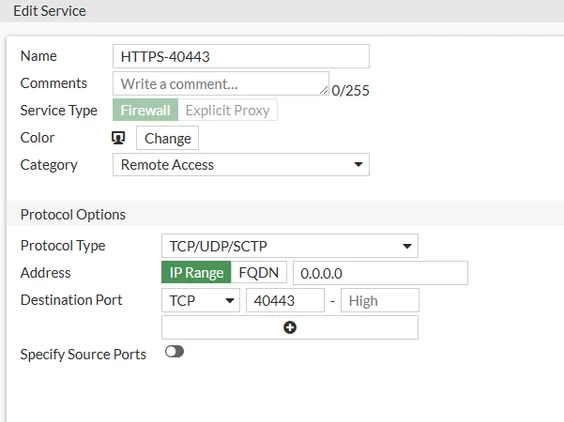
set service "HTTPS-40443"
set schedule "always"
next


The dstaddr is: 
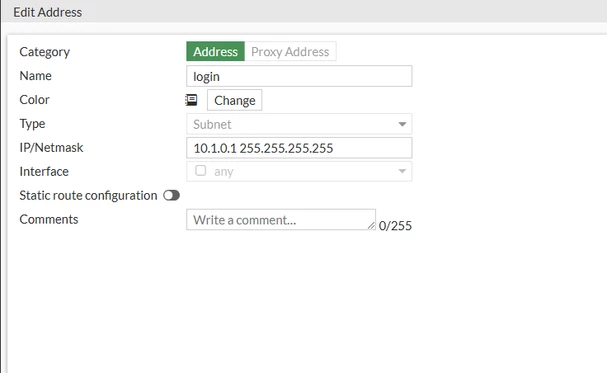
 

1.PNG


while the service is:


2.PNG


I should access the login page from everywhere. Why? What I am doing wrong?


vpn.xxx.com is a DNS entry: 
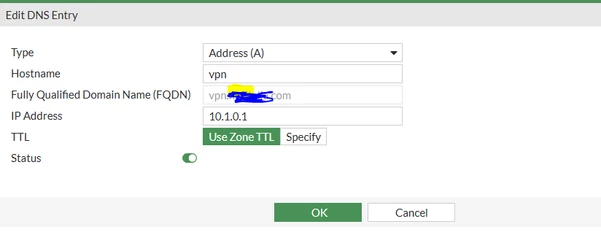
 

3.PNG


Best answer by dingjerry_FTNT

Hi @raffaeledp ,


That's not correct.  The WAN IP is something like you check your PC's WAN IP via https://www.whatismyip.com/ ,  the public IP is not configured on your PC directly. It's a NATted IP by your ISP.


It's the same thing for FGT. The real IP configured on the WAN interface on your FGT device is the one you configured, it might be 10.1.0.1 or 192.168.1.4, I don't know which one is because you never showed the FGT WAN interface configuration either in GUI or in CLI.


I suspect that 192.168.1.4 is the IP on your FGT WAN interface and 10.1.0.1 is the IP on your internal PC. 


That would explain why the local-in policy was not working

7 replies

dingjerry_FTNT
Staff
Staff
February 14, 2025

Hi @raffaeledp ,


I tried using your local-in policy configuration and I got blocked.


So we can debug with the following commands:


diag debug flow show iprope enable

diag debug flow filter proto 6

diag debug flow filter addr 10.1.0.1

diag debug flow filter port 40443

diag debug flow trace start 100

diag debug enable


Then try it with https://10.1.0.1:40443/ first

raffaeledp
Explorer III
February 17, 2025

Hello, you are right. I noticed that when I'm inside the company network (so vpn.xxx.com is directly to 10.1.0.1) I'm blocked. Anyway, when I'm outside, and vpn.xxx.com is resolved to 79.x.x.x, I'm not blocked anymore. I tried to create the same policy (from 6 to 10) with dstaddre "79.x.x.x", but, I can reach vpn.xxx.com:40443. How is it possible? Thanks

raffaeledp
Explorer III
February 17, 2025

Hello,

I found the solution. The problem was the address 79.x.x.x. You have to include inside the policy the private address of the interface (192.168.1.4, and not the public 79.x.x.x)

funkylicious
SuperUser
SuperUser
February 15, 2025

hi,

the dns entry is only significant to the firewall locally.

is vpn.xxx.com resolved by the workstation that you are connecting from, to the same private ip, 10.1.0.1 that would also match the object login that you defined in the local-in ?

if so, the commands that @dingjerry_FTNT provided should shed some light.

"jack of all trades, master of none"
Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT