wamendoza
Explorer II
March 21, 2022
Solved

Webfilter & App Control DONT's WORK :'(

  • March 21, 2022
  • 4 replies
  • 4634 views

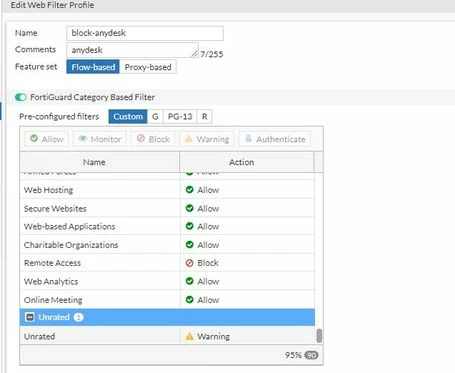
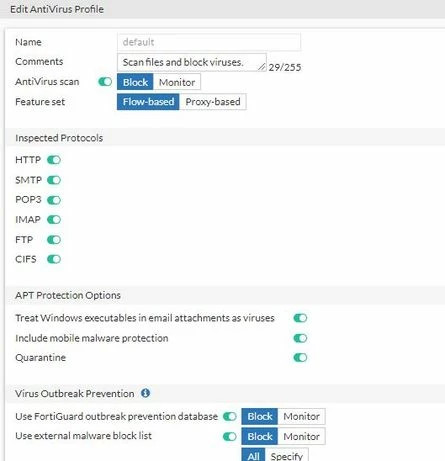
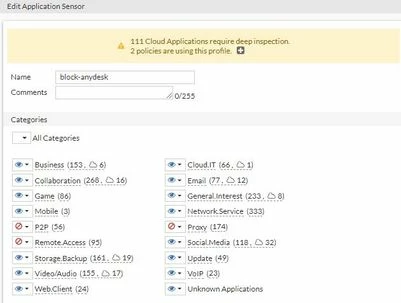
I have a problem with the webfilter and app control of my Fortigate60E


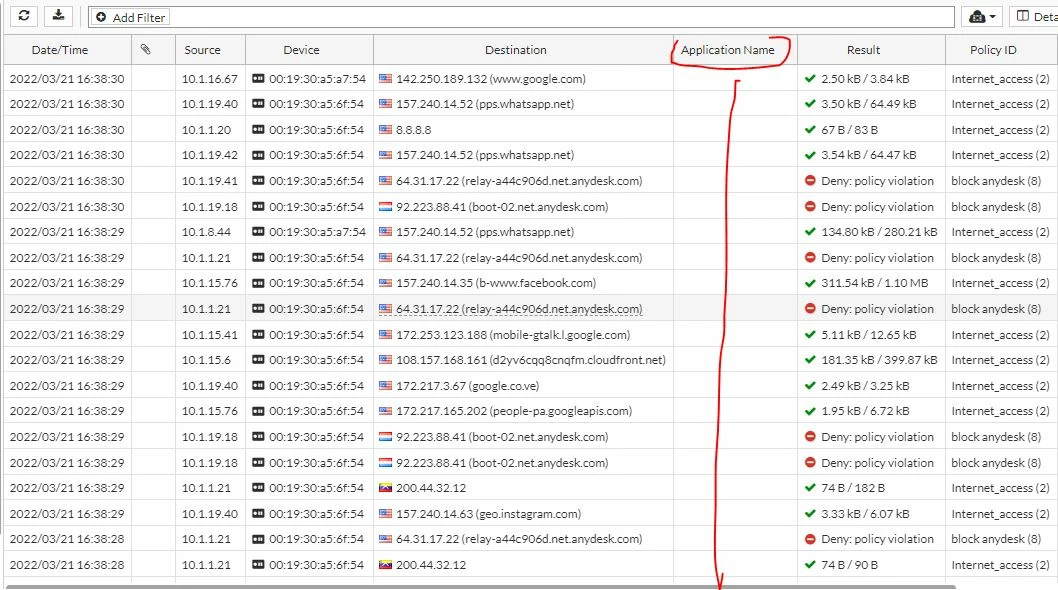
I am blocking EVERYTHING that is remote access and it is not working, which it is but if I go to Log&Report>FowardTraffic absolutely NOTHING is reflected in "Application Name", which makes me assume that my traffic passes without SSL inspection.


I'm using a basic Monitoring setup profiel on App Control and Webfilter, and it doesn't work either, I don't really see anything.


What's going on?
app.JPGwebfil.JPGav.JPGpolicy.JPG

fowartraffic.JPG

Best answer by wamendoza

yes, that's right, there was a crash related to ipsengine process so the restart of the ips engine was carried out using the CLI


 " diagnose test application ipsengine 99".


Thanks for all your time Sir. :)


4 replies

jhussain_FTNT
Staff
Staff
March 22, 2022

You need to configure the policy with deep inspection .When using SSL Certificate Inspection, the SSL Handshake is not interrupted, but the FortiGate reads the CN part of the certificate. This CN part, has the URL for the certificate was signed to. This way, the FortiGate has an URL to check into its categories database. But the TLS/SSL content is not read in any way.

When you use deep inspection, the FortiGate impersonates the recipient of the originating SSL session, then decrypts and inspects the content to find threats and block them. It then re-encrypts the content and sends it to the real recipient.


Kindly refer the below document

https://community.fortinet.com/t5/FortiGate/Technical-Note-Differences-between-SSL-Certificate-Inspection/ta-p/192301


https://docs.fortinet.com/document/fortigate/6.2.0/cookbook/122078/deep-inspection

wamendoza
wamendozaAuthor
Explorer II
March 23, 2022

Hi

After reviewing traffic flow diagram a bit and understanding that the IPS ENGINE encompasses all the traffic inspection(app control, webfilter, av, etc) , i realized that the ipsengine was not running in the "dig sys top",


fortia.JPG


so the restart was carried out through the CLI of ips process via " diagnose test application ipsengine 99".


Now you can see the inspection of packets through FG.

ftlog.JPG


I was also able to notice that there was a crash:

273: 2022-01-24 10:51:29 ipsengine 07.000.044 crashed 3 times. The latest crash was at 2022-01-24


jhussain_FTNT
Staff
Staff
March 24, 2022

Hi,

The IPS crash log date was in month of Jan ( 2022-01-24  ). Are you noticing the same crashlog currently also.

wamendoza
wamendozaAuthorAnswer
Explorer II
March 24, 2022

yes, that's right, there was a crash related to ipsengine process so the restart of the ips engine was carried out using the CLI


 " diagnose test application ipsengine 99".


Thanks for all your time Sir. :)


Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT