Solved
VPN on multiple WAN IP
Hello,
I have WAN network with multiple IP ( subnet )
The wan ip is the x.x.x.228 but but .229 - .232 are available.
I already used different wan IP with VIP to map service for a specific public address
to internal address without problem.
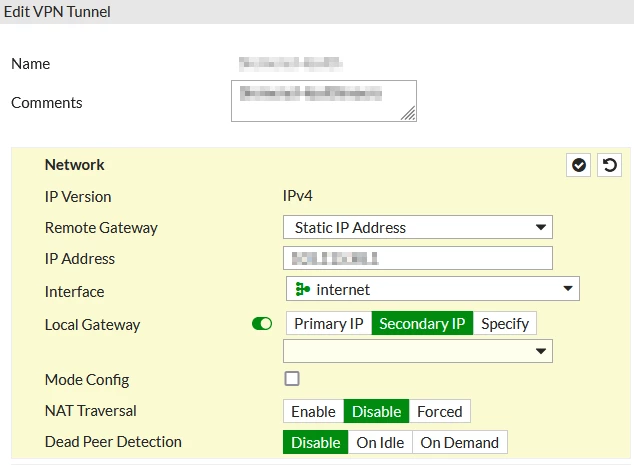
Now I set up a site2site IPsec tunnel and I can't use x.x.x.228 as public IP.
I want my tunnel use x.x.x.229 instead of x.x.x.228 as incoming and outgoing IP
I tried to use IP pool ( 1-to-1 to x.x.x.229) and use NAT on outgoing ( local vpn address-> vpn interface )
vpn policy without success
Which is the best way to manage this situation ?
Do I need to set something on incoming policy ( vpn interface -> local vpn address ) ?
Thank you
Giuseppe