


Solved
VPN IPSEC FORTIGATE - TELTONIKA RUT950
HI,
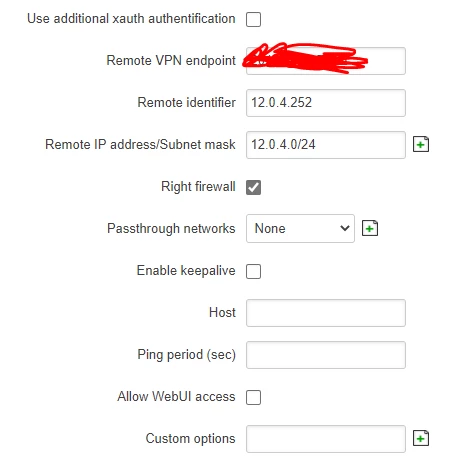
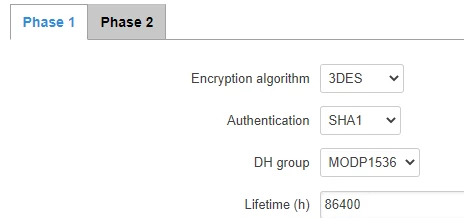
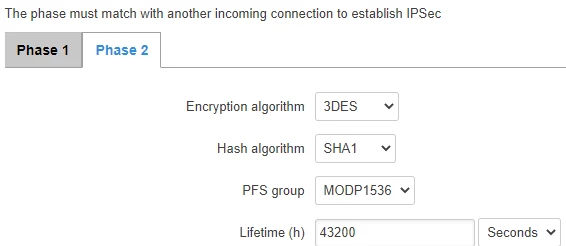
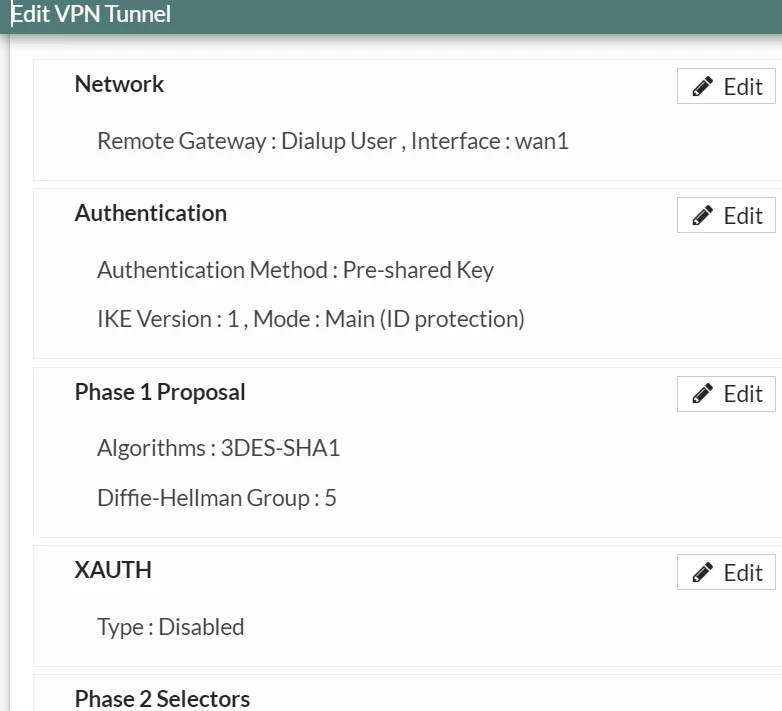
I'm trying to perform an ipsec between a fortigate device and a teltonika rut950, and I can't get it, I'm looking for an idea of why or if there is no compatibility



HI,
I'm trying to perform an ipsec between a fortigate device and a teltonika rut950, and I can't get it, I'm looking for an idea of why or if there is no compatibility
What I can see in this IKE debug output is, despite what you showed on Teltonika side config, the router is initiating IKEv2 IPSec and the negotiation is successful all the way to the point the FGT side accepted and came up, then sent the reply back to the router. Then the router rejected.
I think the reason is you're using LAN side IP for identifier on the router's config. The FGT wouldn't check the received identifier unless you configured "peer ID" on the FGT side. But FGT doesn't send the identifier you configured on the router side unless you configure "local ID" on the FGT side.
First option I would try is to disable identification checking on the router side by like setting FQDN, and leave the FQDN config box empty, which I saw at Teltonika's KB.
https://wiki.teltonika-networks.com/view/IPsec_configuration_examples
Since this seems to be site-to-site, it wouldn't break anything without identification checking.
If you have to do it for security reason, you can try configuring peer ID/local ID on the FGT side to match the router side. There should be some FTNT KBs for that part of config but mostly for dialup IPSec situations.
Toshi
Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.

