


Question
Very large logs
Good afternoon, I need to implement the fortianalyzer, but my current log storage configuration seems to be misconfigured, my firewall is generating 40TB of logs per day, so it is not possible to store it on any device, is there any good practice or ideal filter than storing it in logs? I believe to be storing much more than is necessary due to the size.
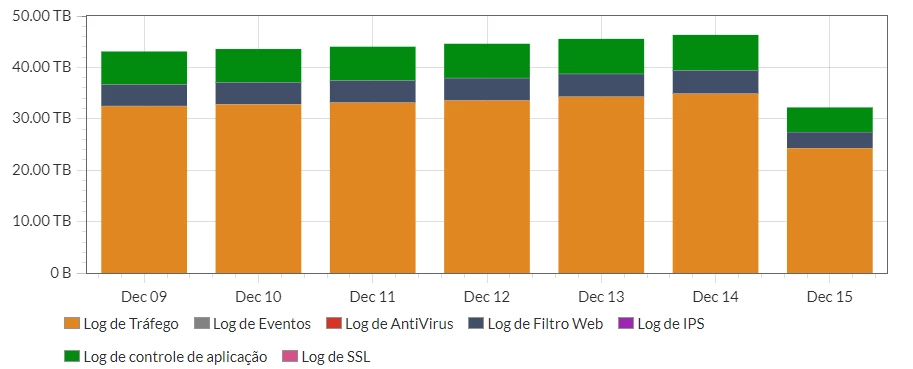
currently the policies are configured to store only the security logs (before it was to record all the logs), but the size has not decreased.

