


Robert_Brumm
New Member
March 20, 2024
Question

udp_flood from from our IPSec Tunnel

  • March 20, 2024
  • 3 replies
  • 2702 views


While troubleshooting a VPN problem, I noticed a lot of udp_flood entries from the other side of the tunnel. The Source IP listed is ours. I changed the policy from block to detect for now, but I can't find a reason for all this traffic. We have 3 other IPsec tunnels that are pretty much identical, but this is the only Fortigate having this occurrence.


Source and destination port 4500. Service is IKE.
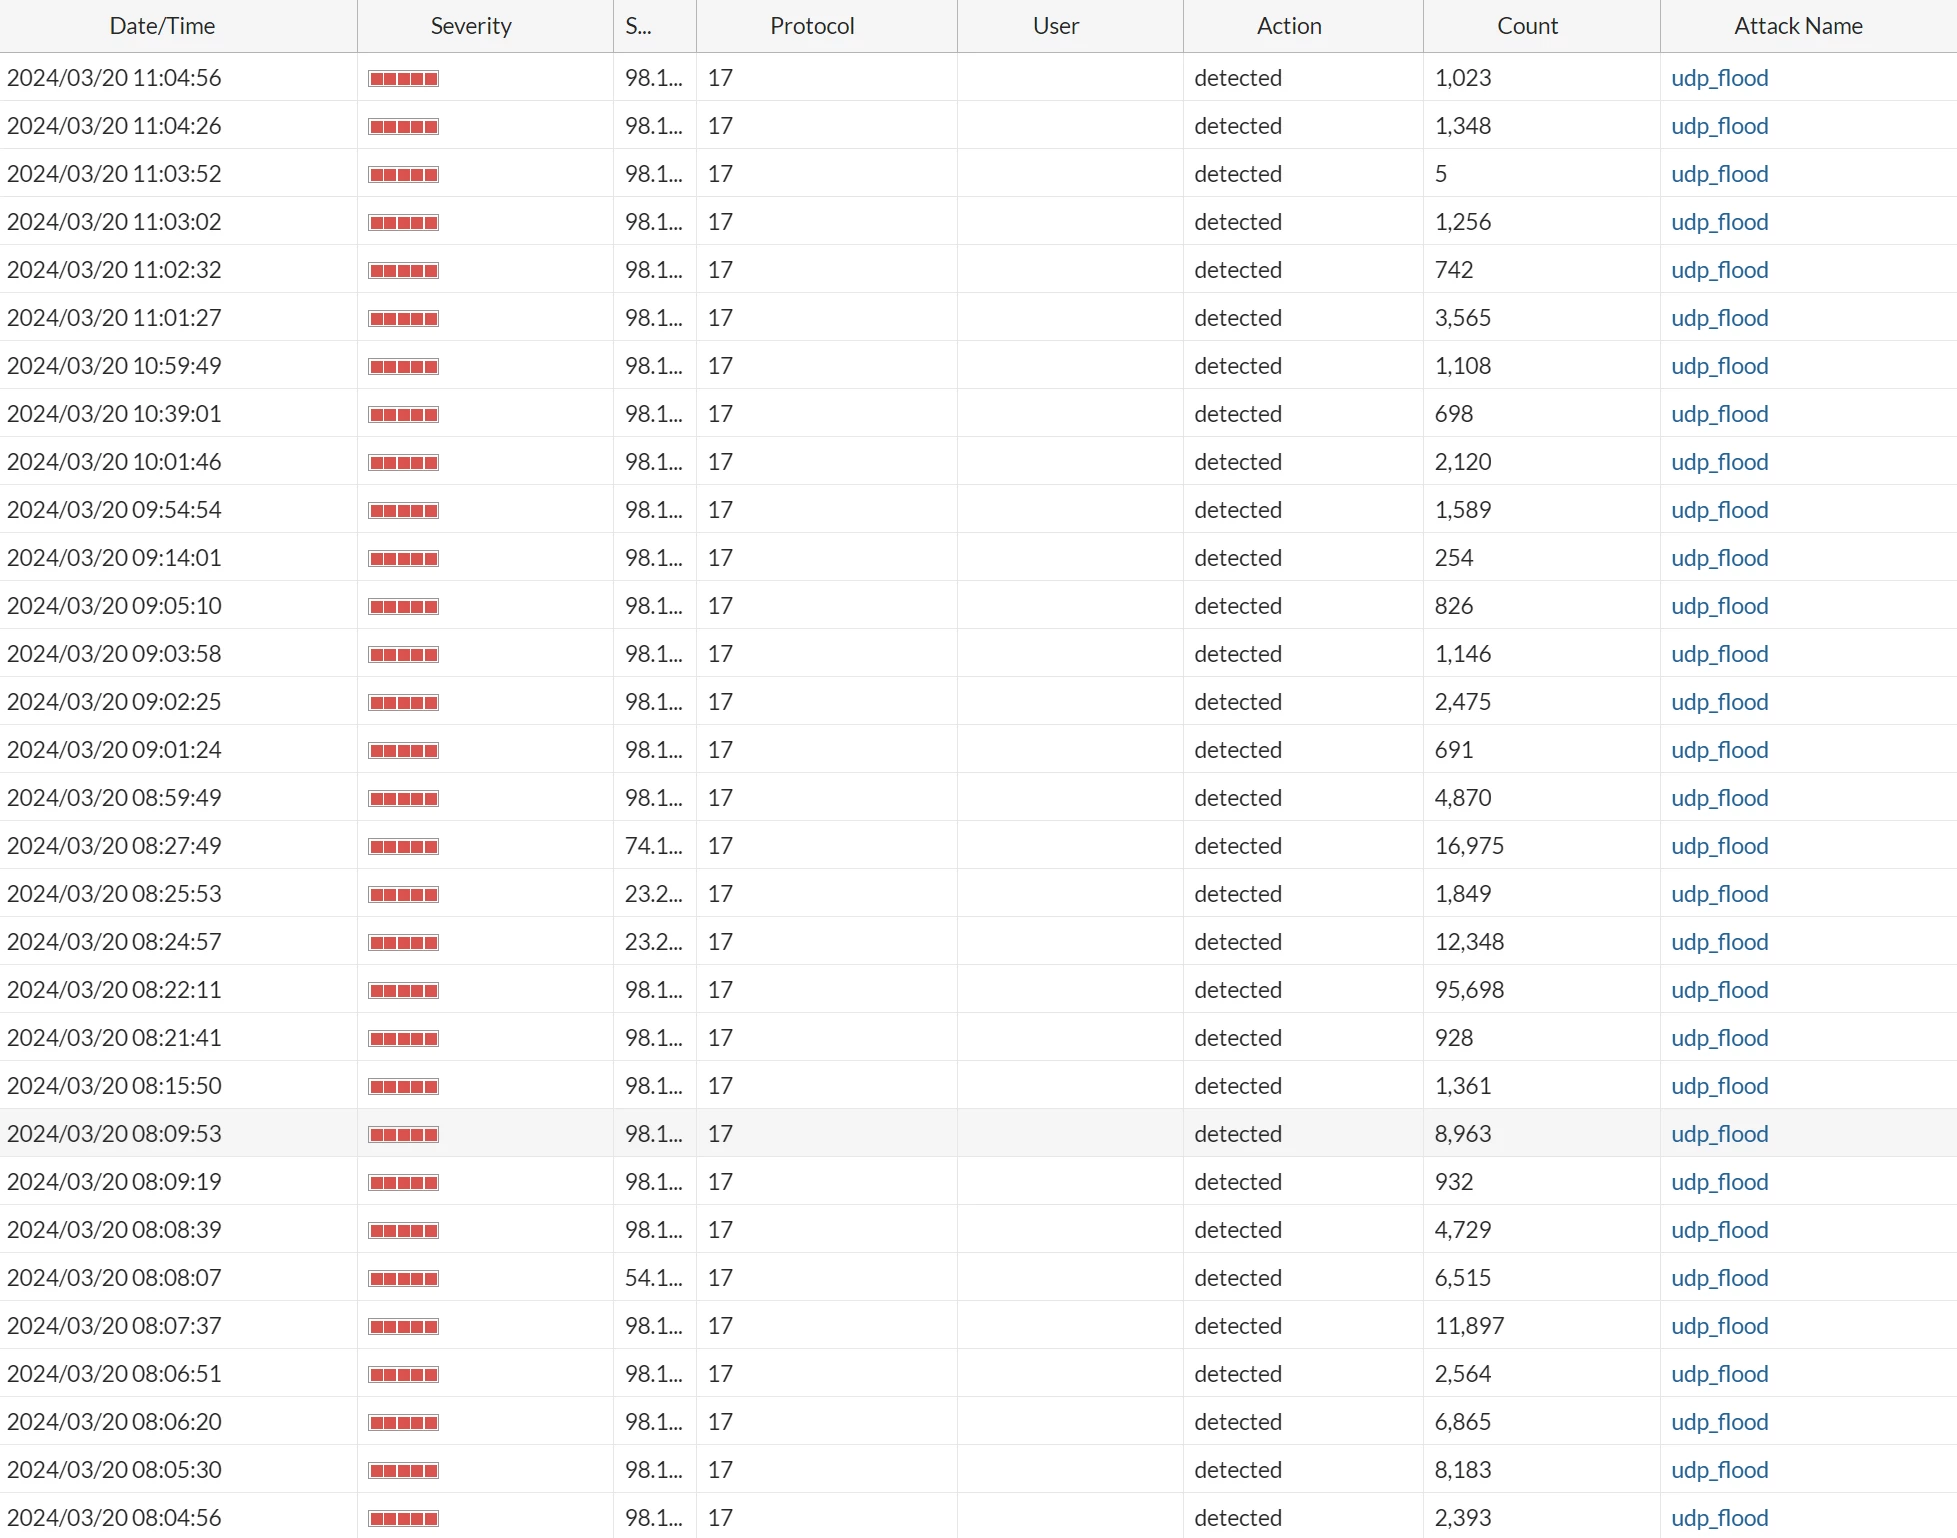
 

2024-03-20 11_06_46-FortiGate - Spring and 6 more pages - Work Regular - Microsoft​ Edge.png

3 replies

johnathan
Staff
Staff
March 20, 2024

Just a false positive. When you have NAT Traversal enabled on your tunnel, it will use UDP port 4500.
It is recommended to exclude either the remote side's Public IP, or port 4500 from the DOS Policy.

See this document: https://community.fortinet.com/t5/Customer-Service/Technical-Tip-DoS-policy-can-cause-slowness-in-traffic-and-IPsec/ta-p/240076

Never trust a computer you can't throw out a window.
Robert_Brumm
New Member
March 20, 2024

Yes, NAT Traversal is on by default so I never paid it much attention and I don't know if we should use it or not. I'm still confused if all 4 of our tunnels have NAT Traversal enabled, why this is only happening on one of our Gates.

johnathan
Staff
Staff
March 20, 2024

NAT-T is usually fine to leave on. Your traffic probably just so happen to match the characteristics your DOS policy is looking for; e.g amount of pkts. in a specific timeframe.

Never trust a computer you can't throw out a window.
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

