



Team Meeting failed because of Forticlient injecting Team network to be routed over vpn tunnel
these 2 microsoft team network are injected into mac route table to be sent over vpn tunnel and when it does this, user fails to join the meeting (see attached screenshot). Our vpn set up is ssl vpn and with split tunnel based on firewall policy destination with FQDN route injection
Below are those network:
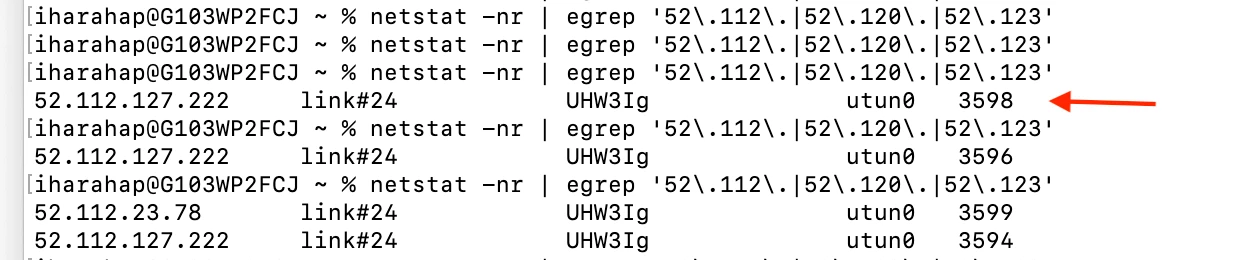
Below are microsoft team network on netstat -nr above
52.112.127.222
Query name (QNAME):
- api.flightproxy.teams.microsoft.com
Answer (A record) name (RRNAME):
- epx-enterpriseproxy.d03-058.ic3-calling-enterpriseproxy.01-eastus-prod.cosmic.office.net
Returned IP
- 52.112.127.222
52.112.23.78
Query name (QNAME):
- epx.usea-03.ic3-calling-enterpriseproxy.eastus-prod.cosmic.office.net
Answer (A record) name (RRNAME):
- epx-enterpriseproxy-1.d03-058.ic3-calling-enterpriseproxy.01-eastus-prod.cosmic.office.net
Returned IP:
- 52.112.23.78
It appears so far only mac user having this issue . The issue is reproducible easily.
We run through diagnose firewall fqdn list-all and the injected IP is not a part of it. So We really suspect the issue most likely triggered by forticlient software . I use the latest 7.4.3. forticlient on mac OS Sequoia version 15.7.4 and having this issue
Thank you for your assistance


